Search
Search for projects by name or address
 ApeChain
Critical contracts can be upgraded by an EOA which could result in the loss of all funds.
Badges
About
ApeChain is an Optimistic Rollup built on the Arbitrum Orbit stack utilizing $APE as its native gas token. It fuels culture by being the chain for digital and IRL communities, builders, creators, collectors, gamers and beyond.
Badges
About
ApeChain is an Optimistic Rollup built on the Arbitrum Orbit stack utilizing $APE as its native gas token. It fuels culture by being the chain for digital and IRL communities, builders, creators, collectors, gamers and beyond.
Why is the project listed in others?
Consequence: projects without a sufficiently decentralized set of challengers rely on few entities to safely update the state. A small set of challengers can collude with the proposer to finalize an invalid state, which can cause loss of funds.
Learn more about the recategorisation here.
ApeChain switches from DAC to Arbitrum One calldata
2026 Jul 1st
ApeChain stops posting data via the AnyTrust DAC and starts posting batches directly to Arbitrum One as calldata.
 Arbitrum One
Funds can be stolen if
MEV can be extracted if
| SEQUENCER FAILURE | STATE VALIDATION | DATA AVAILABILITY | EXIT WINDOW | PROPOSER FAILURE | |
| Arbitrum One L2 | Self sequence | Fraud proofs (INT) | Onchain | None | Self propose |
| ApeChain L3 • Individual | Self sequence | Fraud proofs (INT) | Onchain | None | Self propose |
| ApeChain L3 • Combined | Self sequence | Fraud proofs (INT) | Onchain | None | Self propose |
In the event of a sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. failure, users can force transactions to be included in the project’s chain by sending them to L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development.. There can be up to a 4d delay on this operation.
No actor outside of the single ProposerIn the context of L2s, the actor that proposes a claimed state root on L1. The term is also used in the context of Ethereum to refer to the actor that proposes a new block. can submit fraud proofs. Interactive proofs (INT) require multiple transactions over time to resolve. The challenge protocol can be subject to delay attacks. There is a 6d 8h challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled..
All of the data needed for proof construction is published on Ethereum L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development..
There is no window for users to exit in case of an unwanted upgrade since contracts are instantly upgradable.
Anyone can become a ProposerIn the context of L2s, the actor that proposes a claimed state root on L1. The term is also used in the context of Ethereum to refer to the actor that proposes a new block. after 12d 17h of inactivity from the currently whitelisted Proposers.
All transaction data is recorded on chain
All executed transactions are submitted to an on chain smart contract. The execution of the rollupA blockchain that inherits consensus and data availability from another blockchain called L1. Rollups enable trust minimized bridges with the base layer via proof systems, either optimistic or zero-knowledge. A rollup without a bridge, or without considering the bridge, is called a sovereign rollup. is based entirely on the submitted transactions, so anyone monitoring the contract can know the correct state of the rollup chain.
- Sequencing followed by deterministic execution - Arbitrum documentation
- SequencerInbox.sol - source code, addSequencerL2BatchFromOrigin function
 Ethereum
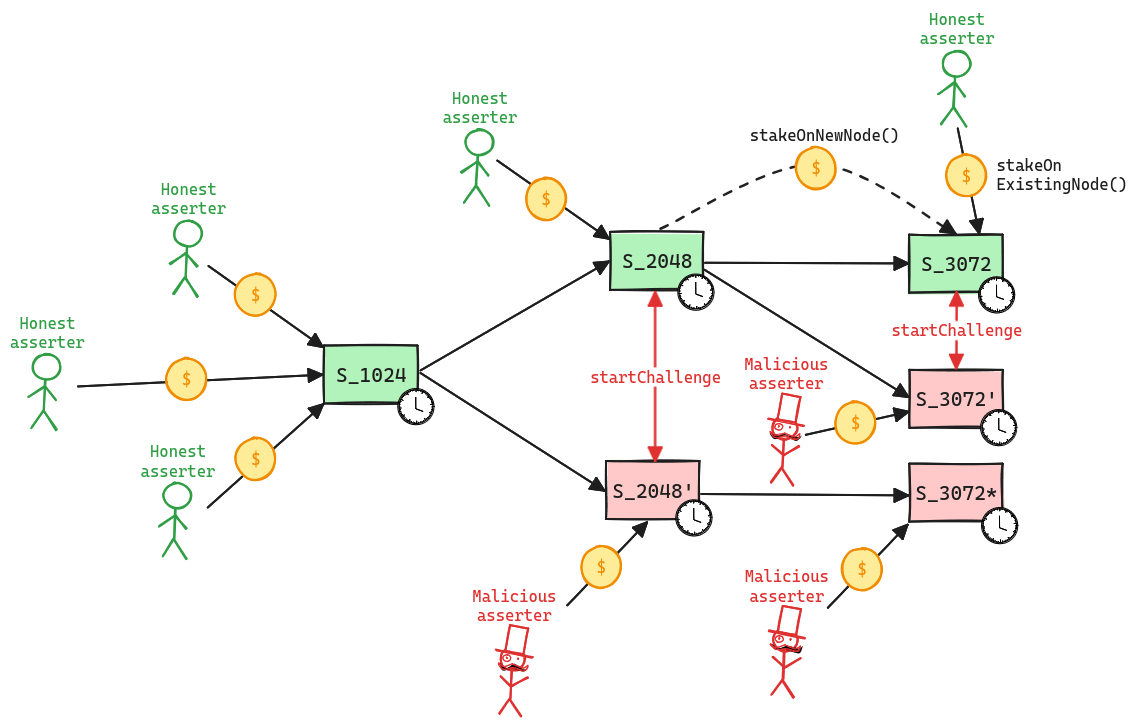
Updates to the system state can be proposed and challenged by a set of whitelisted validatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier. If a state rootA cryptographic hash succinctly representing a state using a Merkle tree. passes the challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled., it is optimistically considered correct and made actionable for withdrawals.
Whitelisted validatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier propose state rootsA cryptographic hash succinctly representing a state using a Merkle tree. as children of a previous state root. A state root can have multiple conflicting children. This structure forms a graph, and therefore, in the contracts, state roots are referred to as nodes. Each proposal requires a stake, currently set to 0.1 ETH, that can be slashed if the proposal is proven incorrect via a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system.. Stakes can be moved from one nodeA software client that participates in the network. to one of its children, either by calling stakeOnExistingNode or stakeOnNewNode. New nodes cannot be created faster than the minimum assertion period by the same validator, currently set to 15m. The oldest unconfirmed node can be confirmed if the challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled. has passed and there are no siblings, and rejected if the parent is not a confirmed node or if the challenge period has passed and no one is staked on it.
Funds can be stolen if none of the whitelisted verifiers checks the published state. Fraud proofs assume at least one honest and able validator (CRITICAL).
A challenge can be started between two siblings, i.e. two different state rootsA cryptographic hash succinctly representing a state using a Merkle tree. that share the same parent, by calling the startChallenge function. ValidatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier cannot be in more than one challenge at the same time, meaning that the protocol operates with partial concurrency. Since each challenge lasts 6d 8h, this implies that the protocol can be subject to delay attacks, where a malicious actor can delay withdrawals as long as they are willing to pay the cost of losing their stakes. If the protocol is delayed attacked, the new stake requirement increases exponentially for each challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled. of delay. Challenges are played via a bisection game, where asserter and challenger play together to find the first instruction of disagreement. Such instruction is then executed onchain in the WASM OneStepProver contract to determine the winner, who then gets half of the stake of the loser. As said before, a state root is rejected only when no one left is staked on it. The protocol does not enforces valid bisections, meaning that actors can propose correct initial claim and then provide incorrect midpoints.
Past upgrades
The metrics include upgrades on the currently used proxy contracts. Historical proxy contracts and changes of such are not included.
2026 October 01, 21:59 UTC1changeSequencerInbox: since 2026-08-31 batches are posted as calldata on Arbitrum One instead of AnyTrust DAC certificates.
SequencerInbox: since 2026-08-31 batches are posted as calldata on Arbitrum One instead of AnyTrust DAC certificates.
| contract SequencerInbox (arb1:0xE6a92Ae29E24C343eE66A2B3D3ECB783d65E4a3C) [orbitstack/SequencerInbox_Espresso] { | |
| +++ description: The Espresso TEE sequencer (registered in this contract) can submit transaction batches or commitments here. | |
| values.sequencerVersion: | |
| - | "0x88" |
| + | "0x00" |
| } | |
2026 August 10, 11:02 UTC1changeSequencerInbox: the latest batch was posted as an AnyTrust DAC certificate rather than as data on the host chain.
SequencerInbox: the latest batch was posted as an AnyTrust DAC certificate rather than as data on the host chain.
| contract SequencerInbox (arb1:0xE6a92Ae29E24C343eE66A2B3D3ECB783d65E4a3C) [orbitstack/SequencerInbox_Espresso] { | |
| +++ description: The Espresso TEE sequencer (registered in this contract) can submit transaction batches or commitments here. | |
| values.sequencerVersion: | |
| - | "0x00" |
| + | "0x88" |
| } | |
2026 July 03, 10:11 UTC3changesSequencerInbox sequencerVersion flipped 0x88 → 0x00 : latest batch posted as Ethereum calldata instead of a DAC certificate (AnyTrust fall-back). ApeChainMultisig dropped one signer; threshold 3/7 → 3/6.
SequencerInbox sequencerVersion flipped 0x88 → 0x00: latest batch posted as Ethereum calldata instead of a DAC certificate (AnyTrust fall-back). ApeChainMultisig dropped one signer; threshold 3/7 → 3/6.
| contract ApeChainMultisig (arb1:0x2B1FbeE3c7D278bFD9E179893FF304fE49FA7DDF) [GnosisSafe] { | |
| +++ description: None | |
| values.$members.3: | |
| - | "arb1:0x83F58bBB1a940E364ED2dE775D1FD5218135cCE3" |
| values.multisigThreshold: | |
| - | "3 of 7 (43%)" |
| + | "3 of 6 (50%)" |
| } | |
| contract SequencerInbox (arb1:0xE6a92Ae29E24C343eE66A2B3D3ECB783d65E4a3C) [orbitstack/SequencerInbox_Espresso] { | |
| +++ description: The Espresso TEE sequencer (registered in this contract) can submit transaction batches or commitments here. | |
| values.sequencerVersion: | |
| - | "0x88" |
| + | "0x00" |
| } | |
2026 June 26, 08:39 UTC26changesRemoved SGX TEE verifier flow from tee attestation verification, leaving only Nitro. Registered new wasm module root (ArbOS commitment) and valid TEE enclave hash. Both are not known from other depoloyments and are not verified. Also, rotated one Apechain ms member and added two more.
Removed SGX TEE verifier flow from tee attestation verification, leaving only Nitro.
Registered new wasm module root (ArbOS commitment) and valid TEE enclave hash. Both are not known from other depoloyments and are not verified.
Also, rotated one Apechain ms member and added two more.
| - | Status: DELETED |
| contract EspressoSGXTEEVerifier (arb1:0x05A16513BF74629b834878731f07b075Cca33f55) [espresso/Sequencing/EspressoSGXTEEVerifier] | |
| +++ description: Verifies attestations of an Intel SGX TEE. | |
| contract ApeChainMultisig (arb1:0x2B1FbeE3c7D278bFD9E179893FF304fE49FA7DDF) [GnosisSafe] { | |
| +++ description: None | |
| values.$members.0: | |
| + | "arb1:0xe2d8761a2a87b06413e39D08C31b683cDD4dF4a4" |
| values.$members.1: | |
| + | "arb1:0x6c447467FED500eEa91309c0b0c302Aa9763412d" |
| values.$members.2: | |
| - | "arb1:0x651cF50272Ffa8f6D954080DF743410Bb0aa7AFa" |
| + | "arb1:0xbc1Cb7133f080eB61262dafB77788B95e208B77F" |
| values.multisigThreshold: | |
| - | "3 of 5 (60%)" |
| + | "3 of 7 (43%)" |
| } | |
| contract RollupProxy (arb1:0x374de579AE15aD59eD0519aeAf1A23F348Df259c) [orbitstack/RollupProxy_fastConfirm] { | |
| +++ description: Central contract for the project's configuration like its execution logic hash (`wasmModuleRoot`) and addresses of the other system contracts. Entry point for Proposers creating new Rollup Nodes (state commitments) and Challengers submitting fraud proofs (In the Orbit stack, these two roles are both held by the Validators). | |
| +++ description: ArbOS version derived from known wasmModuleRoots. | |
| values.arbOsFromWmRoot: | |
| - | "0x5b82aa008989d331bf6f3cf75b85a04c9ee809447c19b85fecaf3b7d749a6576" |
| + | "0x2dc824fed99dcdf659f2523ad68d1ec70bd5f08e3c533996be3a2d2b19813e83" |
| +++ description: Root hash of the WASM module used for execution, like a fingerprint of the L2 logic. Can be associated with ArbOS versions. | |
| values.wasmModuleRoot: | |
| - | "0x5b82aa008989d331bf6f3cf75b85a04c9ee809447c19b85fecaf3b7d749a6576" |
| + | "0x2dc824fed99dcdf659f2523ad68d1ec70bd5f08e3c533996be3a2d2b19813e83" |
| } | |
| - | Status: DELETED |
| contract EspressoTEEVerifier (arb1:0x4fd6D0995B3016726D5674992c1Ec1bDe0989cF5) [espresso/Sequencing/EspressoTEEVerifier_gateway] | |
| +++ description: TEE gateway contract that can be used to 1) register signers that were generated inside a TEE and 2) verify the signatures of such signers. It supports both Intel SGX and AWS Nitro TEEs through modular contracts. | |
| - | Status: DELETED |
| contract QuoteVerifier (arb1:0x69523d25E25e5c78d828Df90459b75F189D40Cf7) [espresso/Sequencing/QuoteVerifier] | |
| +++ description: The QuoteVerifier contract is used by the EspressoTEEVerifier to verify the validity of the TEE quote. It references a PCCSRouter (arb1:0x0d089B3fA00CBAD0a5098025519e9e4620622acF), an access point for Intel SGX 'collateral', crucial references of which some modular contracts are unverified. | |
| contract SafeL2 (arb1:0x6Dc61D9E366697979f69D89a154f2F8cd2F11dA5) [GnosisSafe] { | |
| +++ description: None | |
| receivedPermissions.0.description: | |
| - | "set the enclaveHash (hash of enclave's code and initial data) and delete all registered signers." |
| + | "add, remove or disable supported enclave hashes." |
| receivedPermissions.0.from: | |
| - | "arb1:0x05A16513BF74629b834878731f07b075Cca33f55" |
| + | "arb1:0x9440e52851706A261965c128A6CB3b5C455177Fb" |
| receivedPermissions.1.description: | |
| - | "change the modular TEE verifier contracts." |
| + | "change the TEE verifier contract." |
| receivedPermissions.1.from: | |
| - | "arb1:0x4fd6D0995B3016726D5674992c1Ec1bDe0989cF5" |
| + | "arb1:0x9440e52851706A261965c128A6CB3b5C455177Fb" |
| } | |
| - | Status: DELETED |
| contract EspressoNitroTEEVerifier (arb1:0x9bE8dA826D2C6E6708372f0d056f57B97e6dB029) [apechain/EspressoNitroTEEVerifier_modifiableVerifier] | |
| +++ description: Verifies attestations of an AWS Nitro TEE. | |
| Note: currently only Succinct proofs are used. | |
| contract SequencerInbox (arb1:0xE6a92Ae29E24C343eE66A2B3D3ECB783d65E4a3C) [orbitstack/SequencerInbox_Espresso] { | |
| +++ description: The Espresso TEE sequencer (registered in this contract) can submit transaction batches or commitments here. | |
| values.espressoTEEVerifier: | |
| - | "arb1:0x4fd6D0995B3016726D5674992c1Ec1bDe0989cF5" |
| + | "arb1:0x9440e52851706A261965c128A6CB3b5C455177Fb" |
| } | |
| EOA (arb1:0xFb259F30199B4f4AB9c9a26019f83b195837075E) { | |
| +++ description: None | |
| receivedPermissions.0: | |
| - | {"permission":"interact","from":"arb1:0x9bE8dA826D2C6E6708372f0d056f57B97e6dB029","description":"set the enclaveHash (hash of enclave's code and initial data) and delete all registered signers.","role":".owner"} |
| receivedPermissions.1.via: | |
| + | [{"address":"arb1:0x927dCF5D08795eEFd7C2bEC89777CFCD67950870"}] |
| receivedPermissions.1.role: | |
| - | ".owner" |
| + | "admin" |
| receivedPermissions.1.description: | |
| - | "set the nitro enclave verifier that checks the TEE attestations." |
| receivedPermissions.1.from: | |
| - | "arb1:0x9bE8dA826D2C6E6708372f0d056f57B97e6dB029" |
| + | "arb1:0x9440e52851706A261965c128A6CB3b5C455177Fb" |
| receivedPermissions.1.permission: | |
| - | "interact" |
| + | "upgrade" |
| eoaWithUpgradePermissions: | |
| + | true |
| directlyReceivedPermissions: | |
| + | [{"permission":"act","from":"arb1:0x927dCF5D08795eEFd7C2bEC89777CFCD67950870","role":".owner"}] |
| } | |
| + | Status: CREATED |
| contract ProxyAdmin (arb1:0x927dCF5D08795eEFd7C2bEC89777CFCD67950870) [global/ProxyAdmin] | |
| +++ description: None | |
| + | Status: CREATED |
| contract EspressoTEEVerifier (arb1:0x9440e52851706A261965c128A6CB3b5C455177Fb) [espresso/Sequencing/EspressoTEEVerifier_onlyNitro] | |
| +++ description: TEE gateway contract that can be used to 1) register signers that were generated inside a TEE and 2) verify the signatures of such signers. It supports AWS Nitro TEEs through modular contracts. | |
| + | Status: CREATED |
| contract EspressoNitroTEEVerifier (arb1:0xBA7E3C18A16FfD8062047422c63027459105BB35) [espresso/Sequencing/EspressoNitroTEEVerifier_WithServices] | |
| +++ description: Verifies attestations of an AWS Nitro TEE. | |
| Note: currently only Succinct proofs are used. | |
2026 June 05, 10:09 UTCHigh severity7changesSwitched to checking TEE attestations with zk in the style of Appchain. Appchain contracts resued (a slightly older version though): https://disco.l2beat.com/diff/eth:0x9E490ce0203d191Cae0ABF5614D561cC6fdc771f/arb1:0x9bE8dA826D2C6E6708372f0d056f57B97e6dB029, the only difference is that owner can change the TEE verifier contact.
Switched to checking TEE attestations with zk in the style of Appchain. Appchain contracts resued (a slightly older version though): https://disco.l2beat.com/diff/eth:0x9E490ce0203d191Cae0ABF5614D561cC6fdc771f/arb1:0x9bE8dA826D2C6E6708372f0d056f57B97e6dB029, the only difference is that owner can change the TEE verifier contact.
| - | Status: DELETED |
| contract CertManager (arb1:0x27CA506AC6567Ef79d364b56cf4dE9C4141d803A) [espresso/Sequencing] | |
| +++ description: The CertManager is used for anchoring TEE attestation keys to a trusted Certificate Authority (CA). | |
| contract EspressoTEEVerifier (arb1:0x4fd6D0995B3016726D5674992c1Ec1bDe0989cF5) [espresso/Sequencing/EspressoTEEVerifier_gateway] { | |
| +++ description: TEE gateway contract that can be used to 1) register signers that were generated inside a TEE and 2) verify the signatures of such signers. It supports both Intel SGX and AWS Nitro TEEs through modular contracts. | |
| +++ severity: HIGH | |
| values.espressoNitroTEEVerifier: | |
| - | "arb1:0xC17cd192bd0aF90a0a5c6021ee038E9223bf390C" |
| + | "arb1:0x9bE8dA826D2C6E6708372f0d056f57B97e6dB029" |
| } | |
| contract SafeL2 (arb1:0x6Dc61D9E366697979f69D89a154f2F8cd2F11dA5) [GnosisSafe] { | |
| +++ description: None | |
| receivedPermissions.2: | |
| - | {"permission":"interact","from":"arb1:0xC17cd192bd0aF90a0a5c6021ee038E9223bf390C","description":"set the enclaveHash (hash of enclave's code and initial data) and delete all registered signers.","role":".owner"} |
| } | |
| - | Status: DELETED |
| contract EspressoNitroTEEVerifier (arb1:0xC17cd192bd0aF90a0a5c6021ee038E9223bf390C) [espresso/Sequencing/EspressoNitroTEEVerifier] | |
| +++ description: Verifies attestations of an AWS Nitro TEE. | |
| Note: currently only Succinct proofs are used. | |
| + | Status: CREATED |
| contract NitroEnclaveVerifier (arb1:0x1b467761E7a125381c4f654e11B397023Fc53DD8) [espresso/Sequencing/NitroEnclaveVerifier] | |
| +++ description: ZK-backed verifier for AWS Nitro enclave attestations. Verifies ZK proofs (RiscZero, Succinct SP1 or Pico) that attest AWS Nitro cert chain validation was executed correctly off-chain. | |
| + | Status: CREATED |
| contract EspressoNitroTEEVerifier (arb1:0x9bE8dA826D2C6E6708372f0d056f57B97e6dB029) [apechain/EspressoNitroTEEVerifier_modifiableVerifier] | |
| +++ description: Verifies attestations of an AWS Nitro TEE. | |
| Note: currently only Succinct proofs are used. | |
| + | Status: CREATED |
| contract SP1Verifier (arb1:0xD9d5C8456a168Dd25561064F47bF116111131B1D) [succinct/SP1Verifier] | |
| +++ description: Verifier contract for SP1 proofs (v6.1.0). | |
Arbitrum OneThe system has a centralized sequencer
While forcing transaction is open to anyone the system employs a privileged sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. that has priority for submitting transaction batches and ordering transactions.
MEV can be extracted if the operator exploits their centralized position and frontruns user transactions.
Users can force any transaction
Because the state of the system is based on transactions submitted on the underlying host chain and anyone can submit their transactions there it allows the users to circumvent censorship by interacting with the smart contract on the host chain directly. After a delay of 3d in which a SequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. has failed to include a transaction that was directly posted to the smart contract, it can be forcefully included by anyone on the host chain, which finalizes its ordering.
Delayed forced transactions
To force transactions from the host chain, users must first enqueue “delayed” messages in the “delayed” inbox of the BridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. contract. Only authorized Inboxes are allowed to enqueue delayed messages, and the so-called Inbox contract is the one used as the entry point by calling the sendMessage or sendMessageFromOrigin functions. If the centralized sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. doesn’t process the request within some time bound, users can call the forceInclusion function on the SequencerInbox contract to include the message in the canonical chain. The time bound is hardcoded to be 3d.
Arbitrum OneRegular messaging
The user initiates L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups.->L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. messages by submitting a regular transaction on this chain. When the blockAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over. containing that transaction is settled, the message becomes available for processing on L1. The process of block finalization usually takes several days to complete.
Autonomous exit
Users can (eventually) exit the system by pushing the transaction on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. and providing the corresponding state rootA cryptographic hash succinctly representing a state using a Merkle tree.. The only way to prevent such withdrawal is via an upgrade.
EVM compatible smart contracts are supported
Arbitrum One uses Nitro technology that allows running fraud proofs by executing EVM code on top of WASM.
Arbitrum One
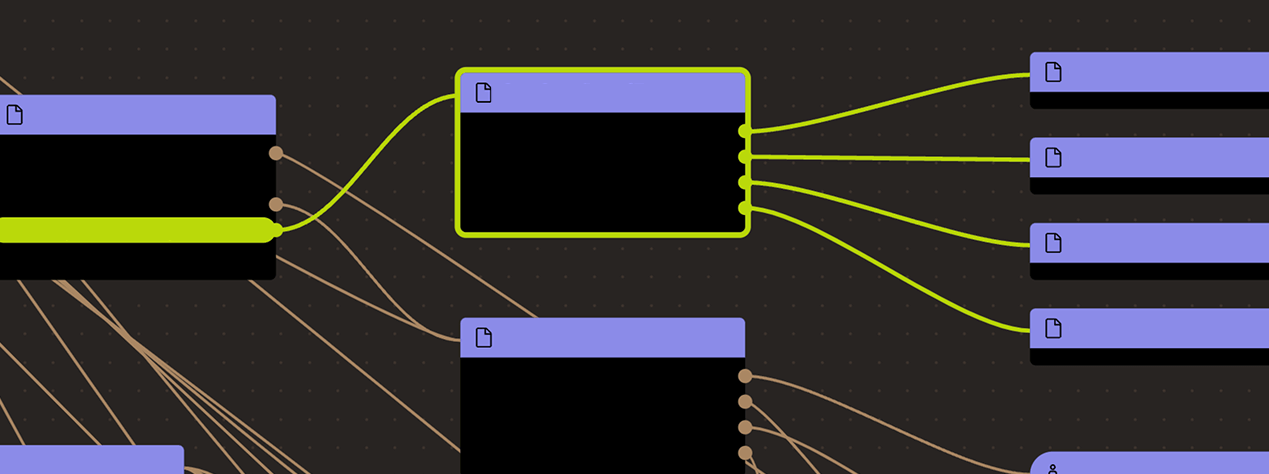
Actors:
A Multisig with 3/6 threshold.
- Can upgrade with no delay
- Inbox UpgradeExecutor → ProxyAdmin
- RollupProxy UpgradeExecutor
- Outbox UpgradeExecutor → ProxyAdmin
- BridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. UpgradeExecutor → ProxyAdmin
- ChallengeManager UpgradeExecutor → ProxyAdmin
- UpgradeExecutor UpgradeExecutor → ProxyAdmin
- SequencerInbox UpgradeExecutor → ProxyAdmin
- RollupEventInbox UpgradeExecutor → ProxyAdmin
- Can interact with RollupProxy
- Pause and unpause and set important roles and parameters in the system contracts: Can delegate SequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. management to a BatchPosterManager address, manage data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium., DACs and the fastConfirmer role, set the Sequencer-only window, introduce an allowList to the bridge and whitelist Inboxes/Outboxes UpgradeExecutor
A Multisig with 2/3 threshold.
- Can interact with EspressoTEEVerifier
- add, remove or disable supported enclave hashes
- change the TEE verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. contract
TEE gateway contract that can be used to 1) register signers that were generated inside a TEE and 2) verify the signatures of such signers. It supports AWS Nitro TEEs through modular contracts.
- Can interact with EspressoNitroTEEVerifier
- set the enclaveHash (hashA fixed-length fingerprint of variable-size input, produced by a hash function. of enclave’s code and initial data) and delete all registered signers
- Can interact with SequencerInbox
- Add/remove batchPosters (Sequencers)
- Can submit transaction batches or commitments to the SequencerInbox contract on the host chain
- Can interact with RollupProxy
- Can propose new state rootsA cryptographic hash succinctly representing a state using a Merkle tree. (called nodes) and challenge state roots on the host chain
- Can upgrade with no delay
- EspressoTEEVerifier ProxyAdmin
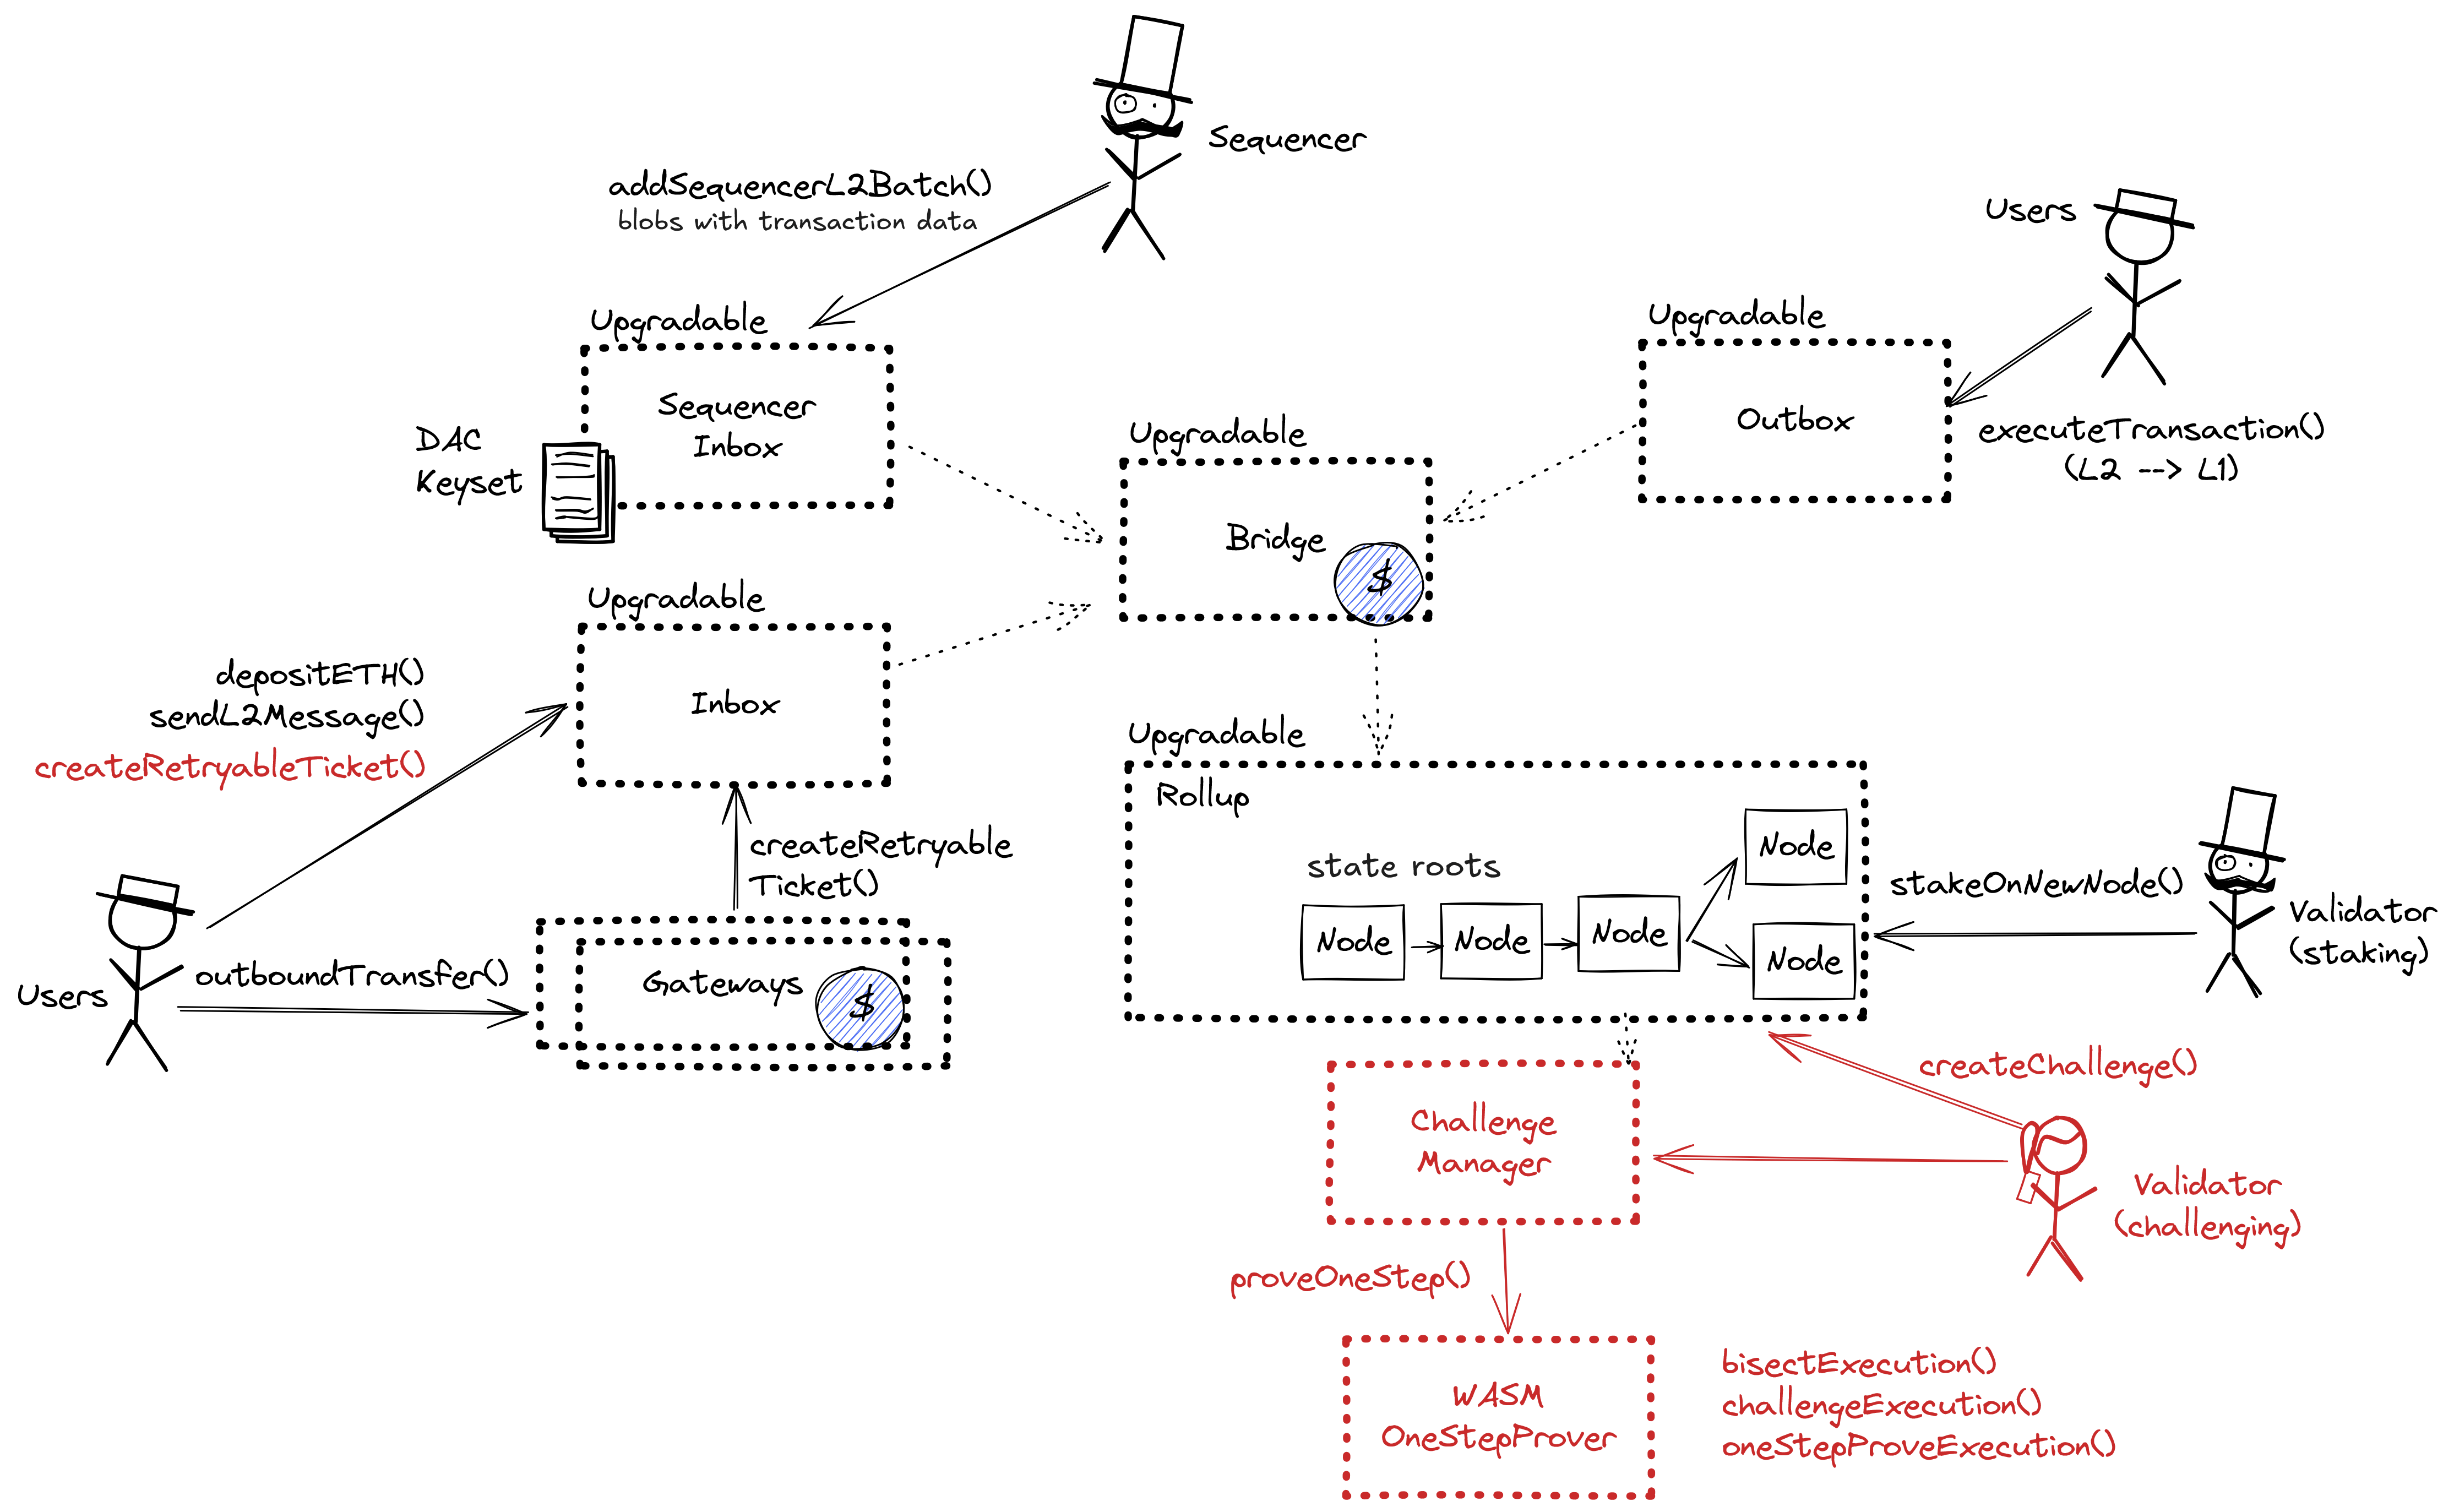
Arbitrum One
Central contract for the project’s configuration like its execution logic hashA fixed-length fingerprint of variable-size input, produced by a hash function. (wasmModuleRoot) and addresses of the other system contracts. Entry point for Proposers creating new RollupA blockchain that inherits consensus and data availability from another blockchain called L1. Rollups enable trust minimized bridges with the base layer via proof systems, either optimistic or zero-knowledge. A rollup without a bridge, or without considering the bridge, is called a sovereign rollup. Nodes (state commitments) and Challengers submitting fraud proofs (In the Orbit stack, these two roles are both held by the ValidatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier).
- Roles:
- admin: UpgradeExecutor; ultimately ApeChainMultisig
- owner: UpgradeExecutor; ultimately ApeChainMultisig
- validators: EOA 2
Escrow contract for the project’s gasA virtual fuel used to execute smart contracts on a rollup. The EVM (or other VM within the rollup) uses an accounting mechanism to correspond the consumption of gas to the consumption of computing resources, and to limit the consumption of computing resources. token (can be different from ETH). Keeps a list of allowed Inboxes and Outboxes for canonical bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. messaging.
- Roles:
- admin: ProxyAdmin; ultimately ApeChainMultisig
Contract that allows challenging state rootsA cryptographic hash succinctly representing a state using a Merkle tree.. Can be called through the RollupProxy by ValidatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier or the UpgradeExecutor.
- Roles:
- admin: ProxyAdmin; ultimately ApeChainMultisig
The Espresso TEE sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. (registered in this contract) can submit transaction batches or commitments here.
- Roles:
- admin: ProxyAdmin; ultimately ApeChainMultisig
- batchPosterManager: EOA 1
- batchPosters: EOA 1
Central contract defining the access control permissions for upgrading the system contract implementations.
- Roles:
- admin: ProxyAdmin; ultimately ApeChainMultisig
- executors: ApeChainMultisig
Facilitates sending L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. to L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. messages like depositing ETH, but does not escrow funds.
- Roles:
- admin: ProxyAdmin; ultimately ApeChainMultisig
Facilitates L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. to L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. contract calls: Messages initiated from L2 (for example withdrawal messages) eventually resolve in execution on L1.
- Roles:
- admin: ProxyAdmin; ultimately ApeChainMultisig
ZK-backed verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for AWS Nitro enclave attestations. Verifies ZK proofs (RiscZero, Succinct SP1 or Pico) that attest AWS Nitro cert chain validation was executed correctly off-chain.
- Roles:
- owner: EOA 3
- Roles:
- owner: UpgradeExecutor
One of the modular contracts used for the last step of a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system., which is simulated inside a WASM virtual machine.
One of the modular contracts used for the last step of a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system., which is simulated inside a WASM virtual machine.
One of the modular contracts used for the last step of a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system., which is simulated inside a WASM virtual machine.
- Roles:
- owner: EOA 4
One of the modular contracts used for the last step of a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system., which is simulated inside a WASM virtual machine.
One of the modular contracts used for the last step of a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system., which is simulated inside a WASM virtual machine.
This contract implements view only utilities for validatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier.
Verifies attestations of an AWS Nitro TEE. Note: currently only Succinct proofs are used.
- Roles:
- teeVerifier: EspressoTEEVerifier
VerifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. contract for SP1 proofs (v6.1.0).
Helper contract sending configuration data over the bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. during the systems initialization.
- Roles:
- admin: ProxyAdmin; ultimately ApeChainMultisig
The current deployment carries some associated risks:
Funds can be stolen if a contract receives a malicious code upgrade. There is no delay on code upgrades (CRITICAL).