Search
Search for projects by name or address
 ApeX Pro
 and the associated StarkEx instances were sunset.
Critical contracts can be upgraded by an EOA which could result in the loss of all funds.
Badges
About
ApeX Pro is a non-custodial trading platform that delivers limitless cross-margined perpetual contracts trading.
Badges
About
ApeX Pro is a non-custodial trading platform that delivers limitless cross-margined perpetual contracts trading.
Why is the project listed in others?
Consequence: projects with a low DAC threshold rely on the honesty of few entities to safely attest data availability on Ethereum. These entities can collude with the proposer to finalize an unavailable state, which can cause loss of funds.
Learn more about the recategorisation here.
ApeX Pro public beta launched
2022 Nov 21st
ApeX Pro beta is launched, with incentives program for users.
ApeX Pro live on Mainnet
2022 Aug 31st
ApeX Pro, a non-custodial decentralized exchange is now live on Mainnet.
ApeX Pro is a non-custodial trading platform that delivers limitless cross-margined perpetual contracts trading.
ApeX Pro is running two independent StarkEx instances, one for USDC and one for USDT, but that technical distinction is not visible to the user.
Funds can be stolen if
Funds can be lost if
Users can be censored if
MEV can be extracted if
Users can force the sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. to include a trade or a withdrawal transaction by submitting a request through L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development.. If the sequencer censors or is down for 7d, users can use the exit hatch to withdraw their funds. Users are required to find a counterparty for the trade by out of system means.
STARKs are zero knowledge proofs that ensure state correctness.
Proof construction relies fully on data that is NOT published onchain. There exists a Data Availability Committee (DAC)A set of members whose task is attesting and ensuring that the data is available for the public. An onchain DAC verifier checks that a threshold of signatures from the DAC members is reached before considering a data commitment as available and therefore valid to be used in the system. with a threshold of 3/5 that is tasked with protecting and supplying the data.
Users have 1d to exit funds in case of an unwanted upgrade. There is a 8d delay before a upgrade is applied, and withdrawals can take up to 7d to be processed.
Users are able to trustlessly exit by submitting a Merkle proof of funds. Positions will be closed using the average price from the last batch state updateA mechanism that allows to update the claimed state of a project. It usually involves verifying a state transition proof, but it can also be done in a trusted manner by a permissioned actor..
Set of parties responsible for signing and attesting to the availability of data.
There are no onchain assets at risk of being slashed in case of a data withholding attack, and the committee members are not publicly known.
There is no fraud detection mechanism in place. A data withholding attack can only be detected by nodes downloading the full data from the DA layerAn infrastructure that is used to make publish data so that it's available to the public. They take the form of Data Availability Committees (DACs) or blockchains. Not to confuse with the layer responsible with ordering, since ordering and DA can be separated..
The committee does not meet basic security standards, either due to insufficient size, lack of member diversity, or poorly defined threshold parameters. The system lacks an effective DA bridgeSystem that verifies that data has been made available. It takes the form of a smart contract verifying a consensus or, if the data is verified directly by either downloading the full data or sampling, of an enshrined bridge. and it is reliant on the assumption of an honest sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs., creating significant risks to data integrity and availability.
The bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. smart contract is immutable and cannot be updated. The bridge committee security is low and cannot be improved.
Anyone can relay data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium. commitments to the DA bridgeSystem that verifies that data has been made available. It takes the form of a smart contract verifying a consensus or, if the data is verified directly by either downloading the full data or sampling, of an enshrined bridge.. In case of current relayer failure, users can collect attestations from committee members and propose new data availability commitments to the DA bridge.
Architecture
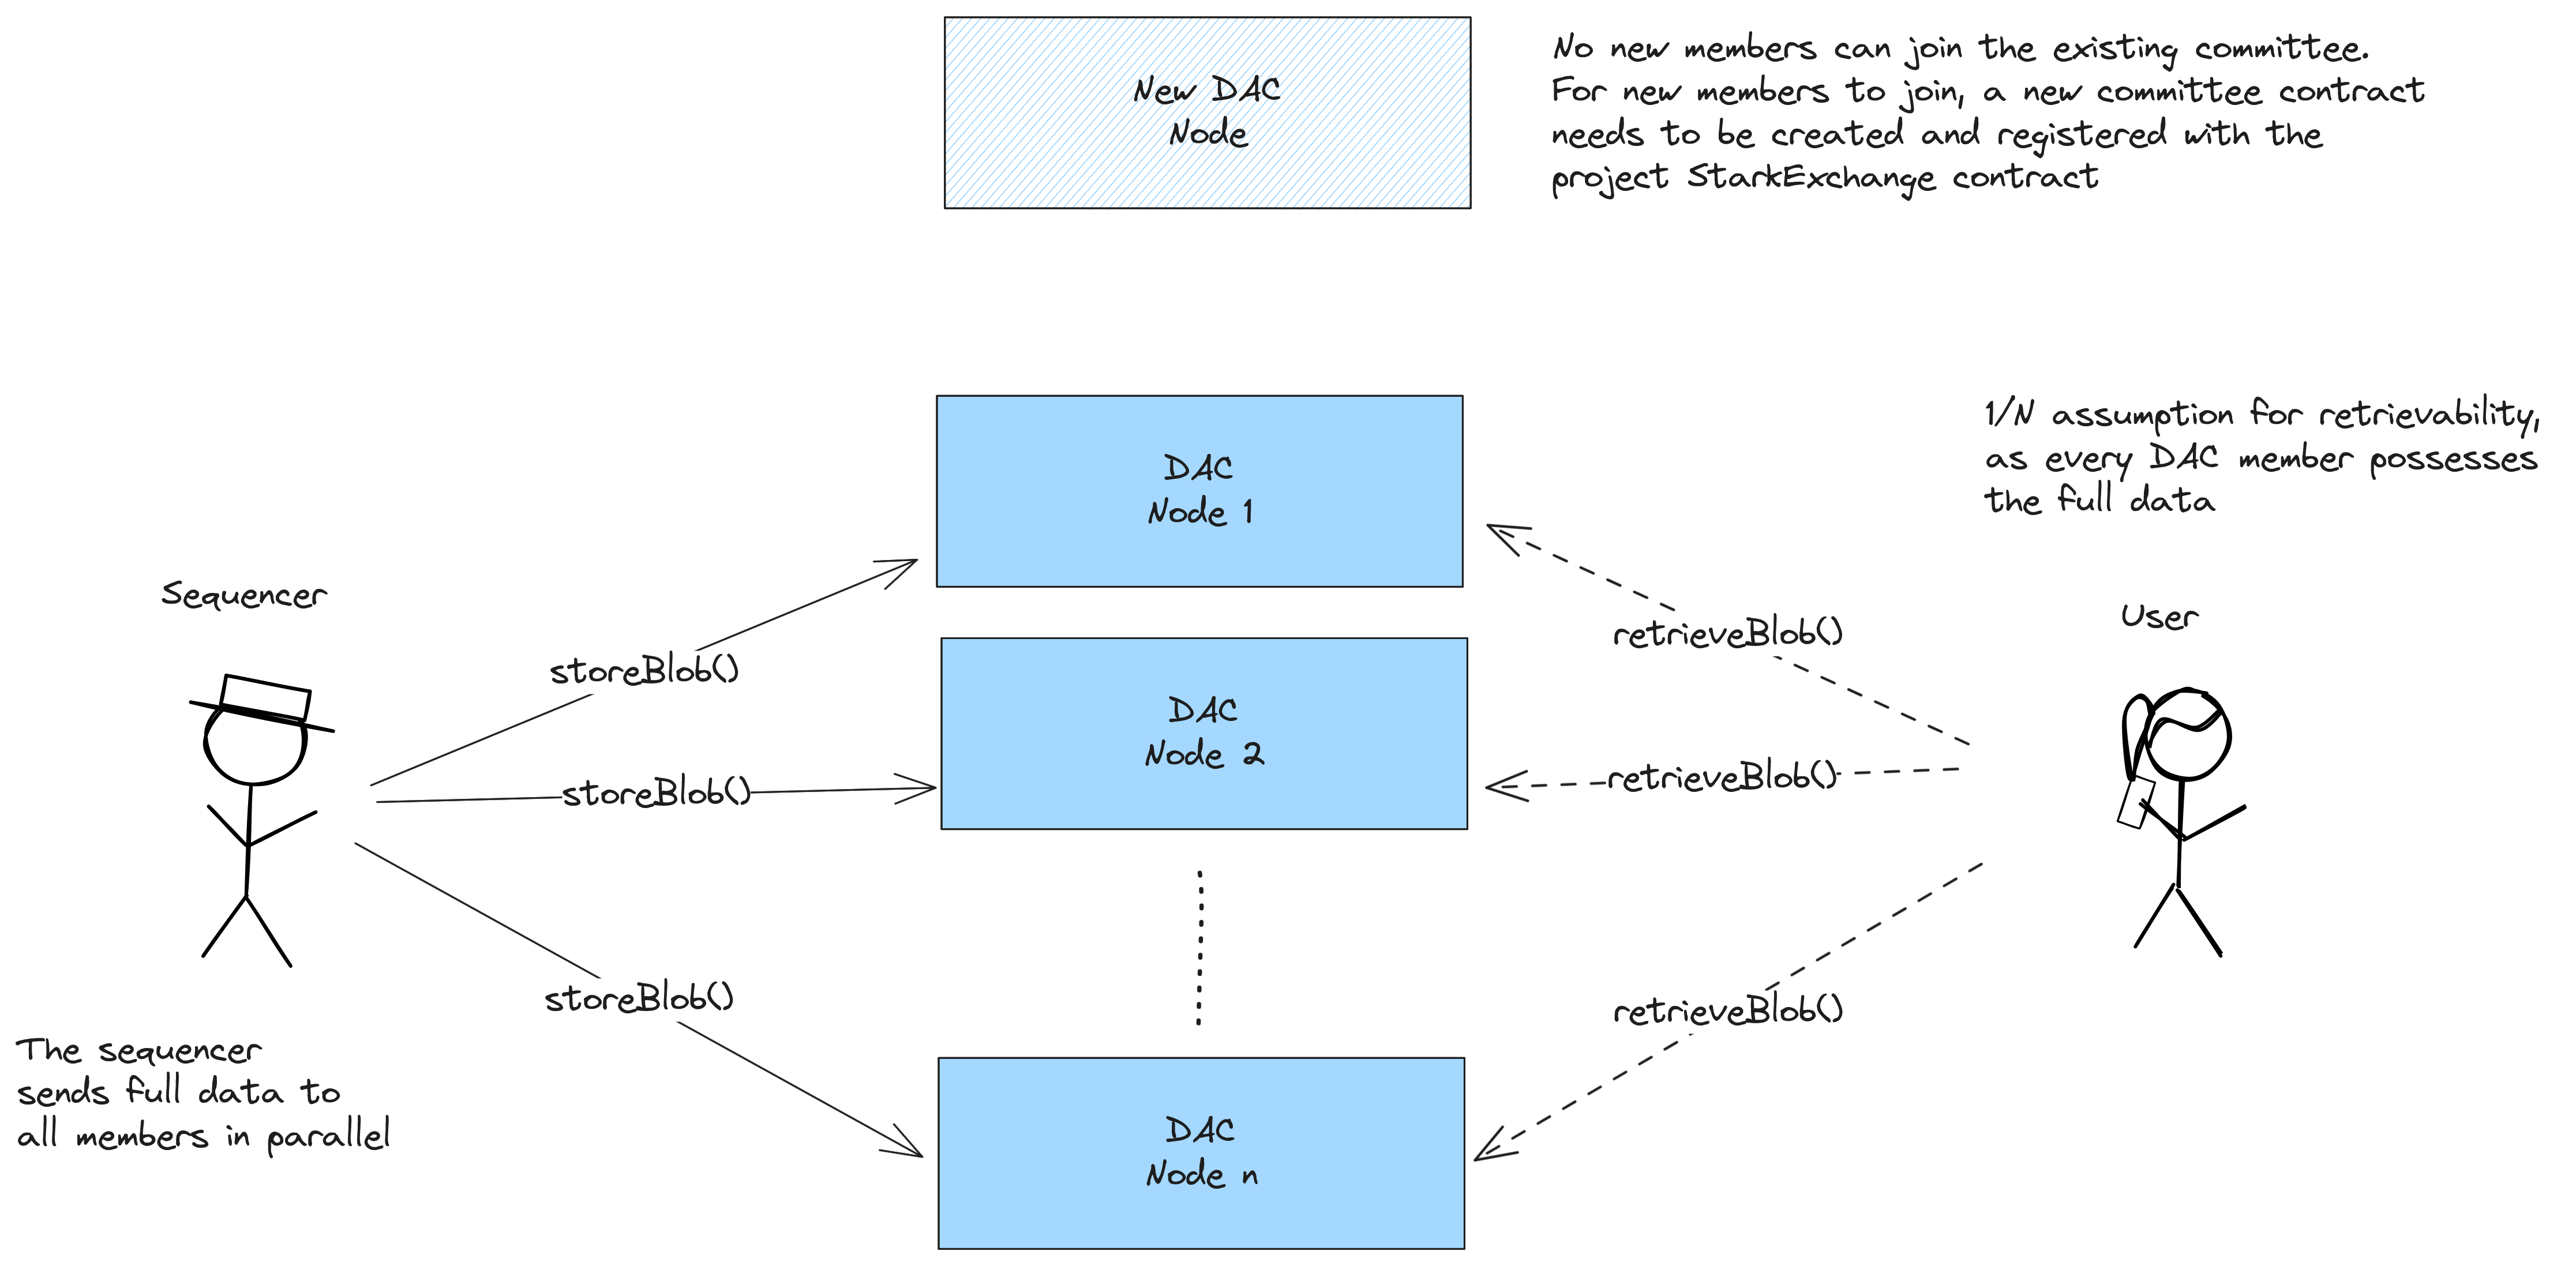
The Starkware application utilizes a data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium. solution that relies on a Committee Service to ensure data persistence. This architecture comprises the following components:
- Availability Gateway: The primary interface provided by the operatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades. for committee members to access new batch information and submit signed availability claims.
- Data Availability Committee (DAC)A set of members whose task is attesting and ensuring that the data is available for the public. An onchain DAC verifier checks that a threshold of signatures from the DAC members is reached before considering a data commitment as available and therefore valid to be used in the system.: A group of nodes responsible for storing state data associated with each Merkle root and attesting to data availability by signing claims.
- Data Batches: Collections of transactions processed in batches that update the state of accounts, resulting in a new Merkle root representing the updated state.
Committee members run services that interact with the Availability Gateway to obtain information about new batches and submit their signed availability claims. Each batch includes a unique batch_id, a reference to a previous batch, and a list of account updates. Committee members combine this information with data from the reference batch to compute the new state and verify the Merkle root.
When the operator produces a new batch, it must be signed by a minimum number of committee members—as defined by the application’s configuration—for it to be accepted onchain. This includes all members designated as mandatory signers. If the operator attempts to submit a batch without the required signatures, it will be rejected, thereby ensuring that data remains available and consistent.
Committee members are expected to maintain a database that stores the data associated with each batch, making use of storage solutions with a replication factor of at least 2.
DA BridgeSystem that verifies that data has been made available. It takes the form of a smart contract verifying a consensus or, if the data is verified directly by either downloading the full data or sampling, of an enshrined bridge. Architecture
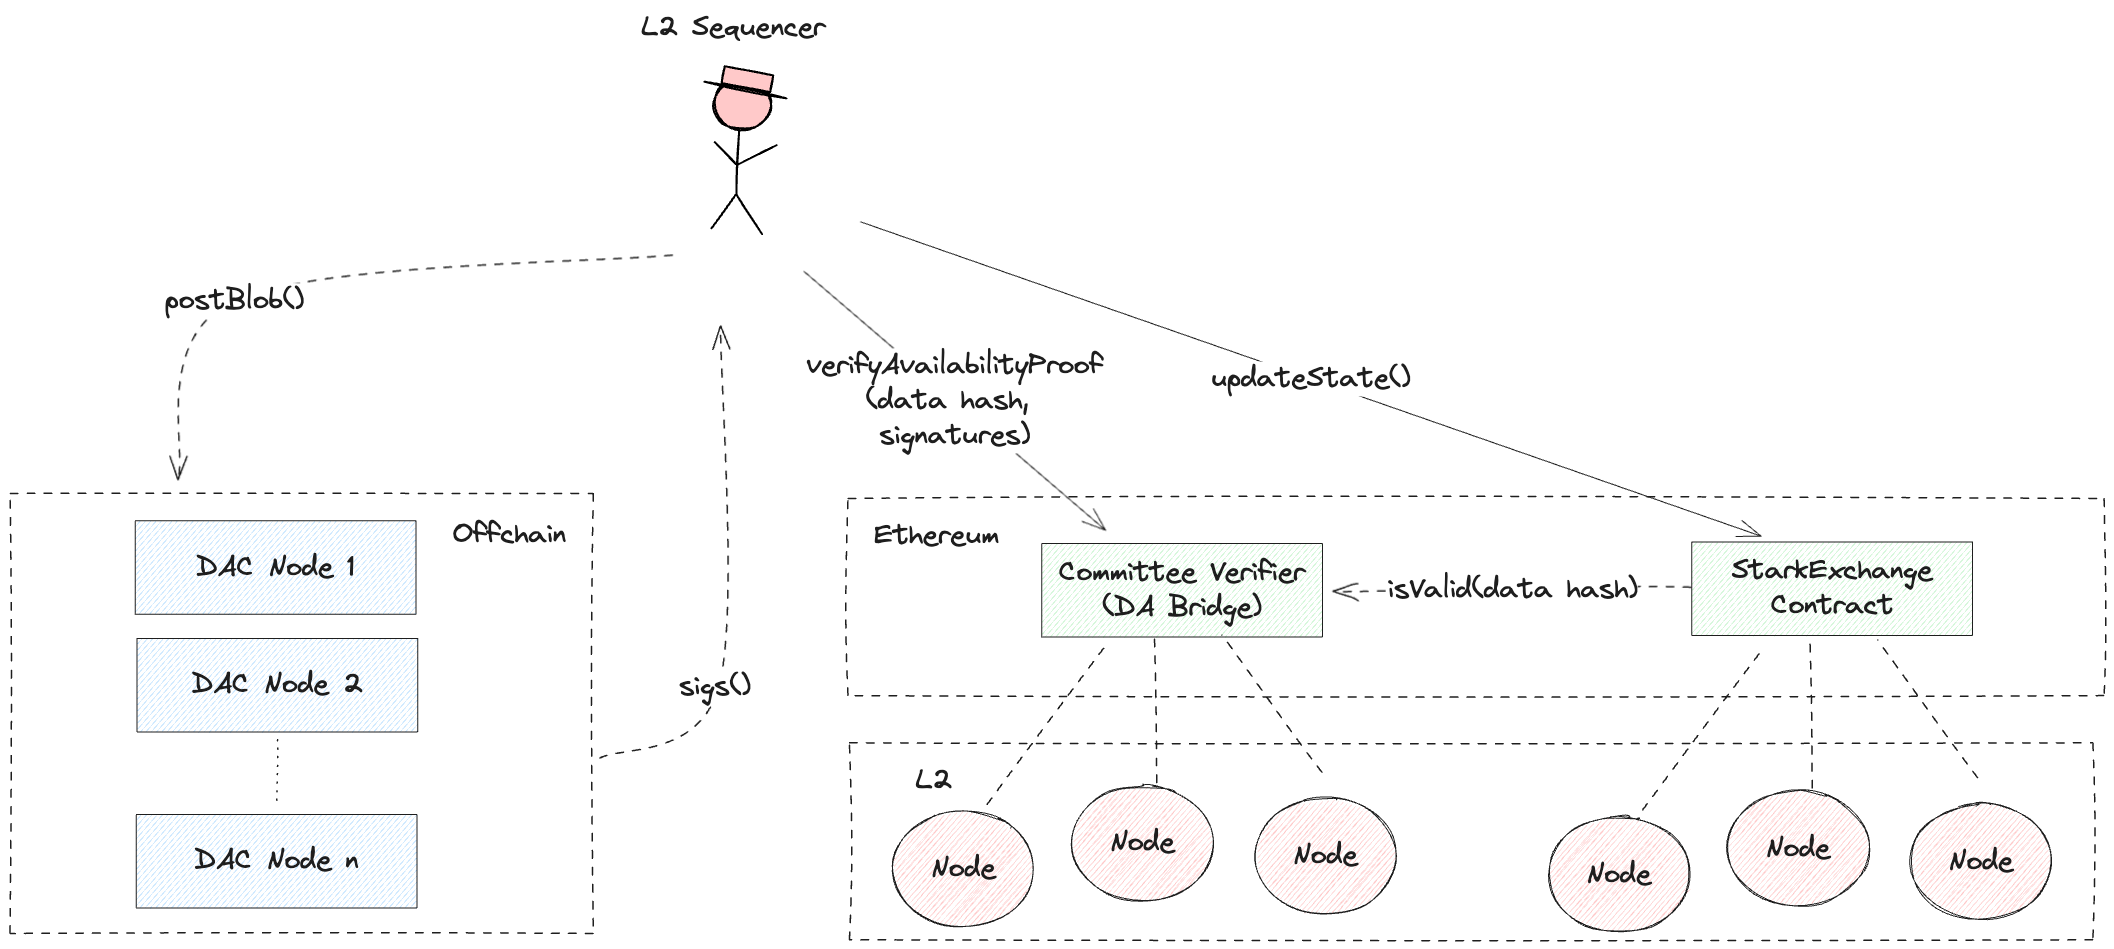
The DA commitments are posted to the destination chain, using the Committee VerifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. contract as a DA bridge. The DA commitment consists of a data hashA fixed-length fingerprint of variable-size input, produced by a hash function. of the transaction batch the Committee has signed off on and a concatenation of ec-signatures by signatories.
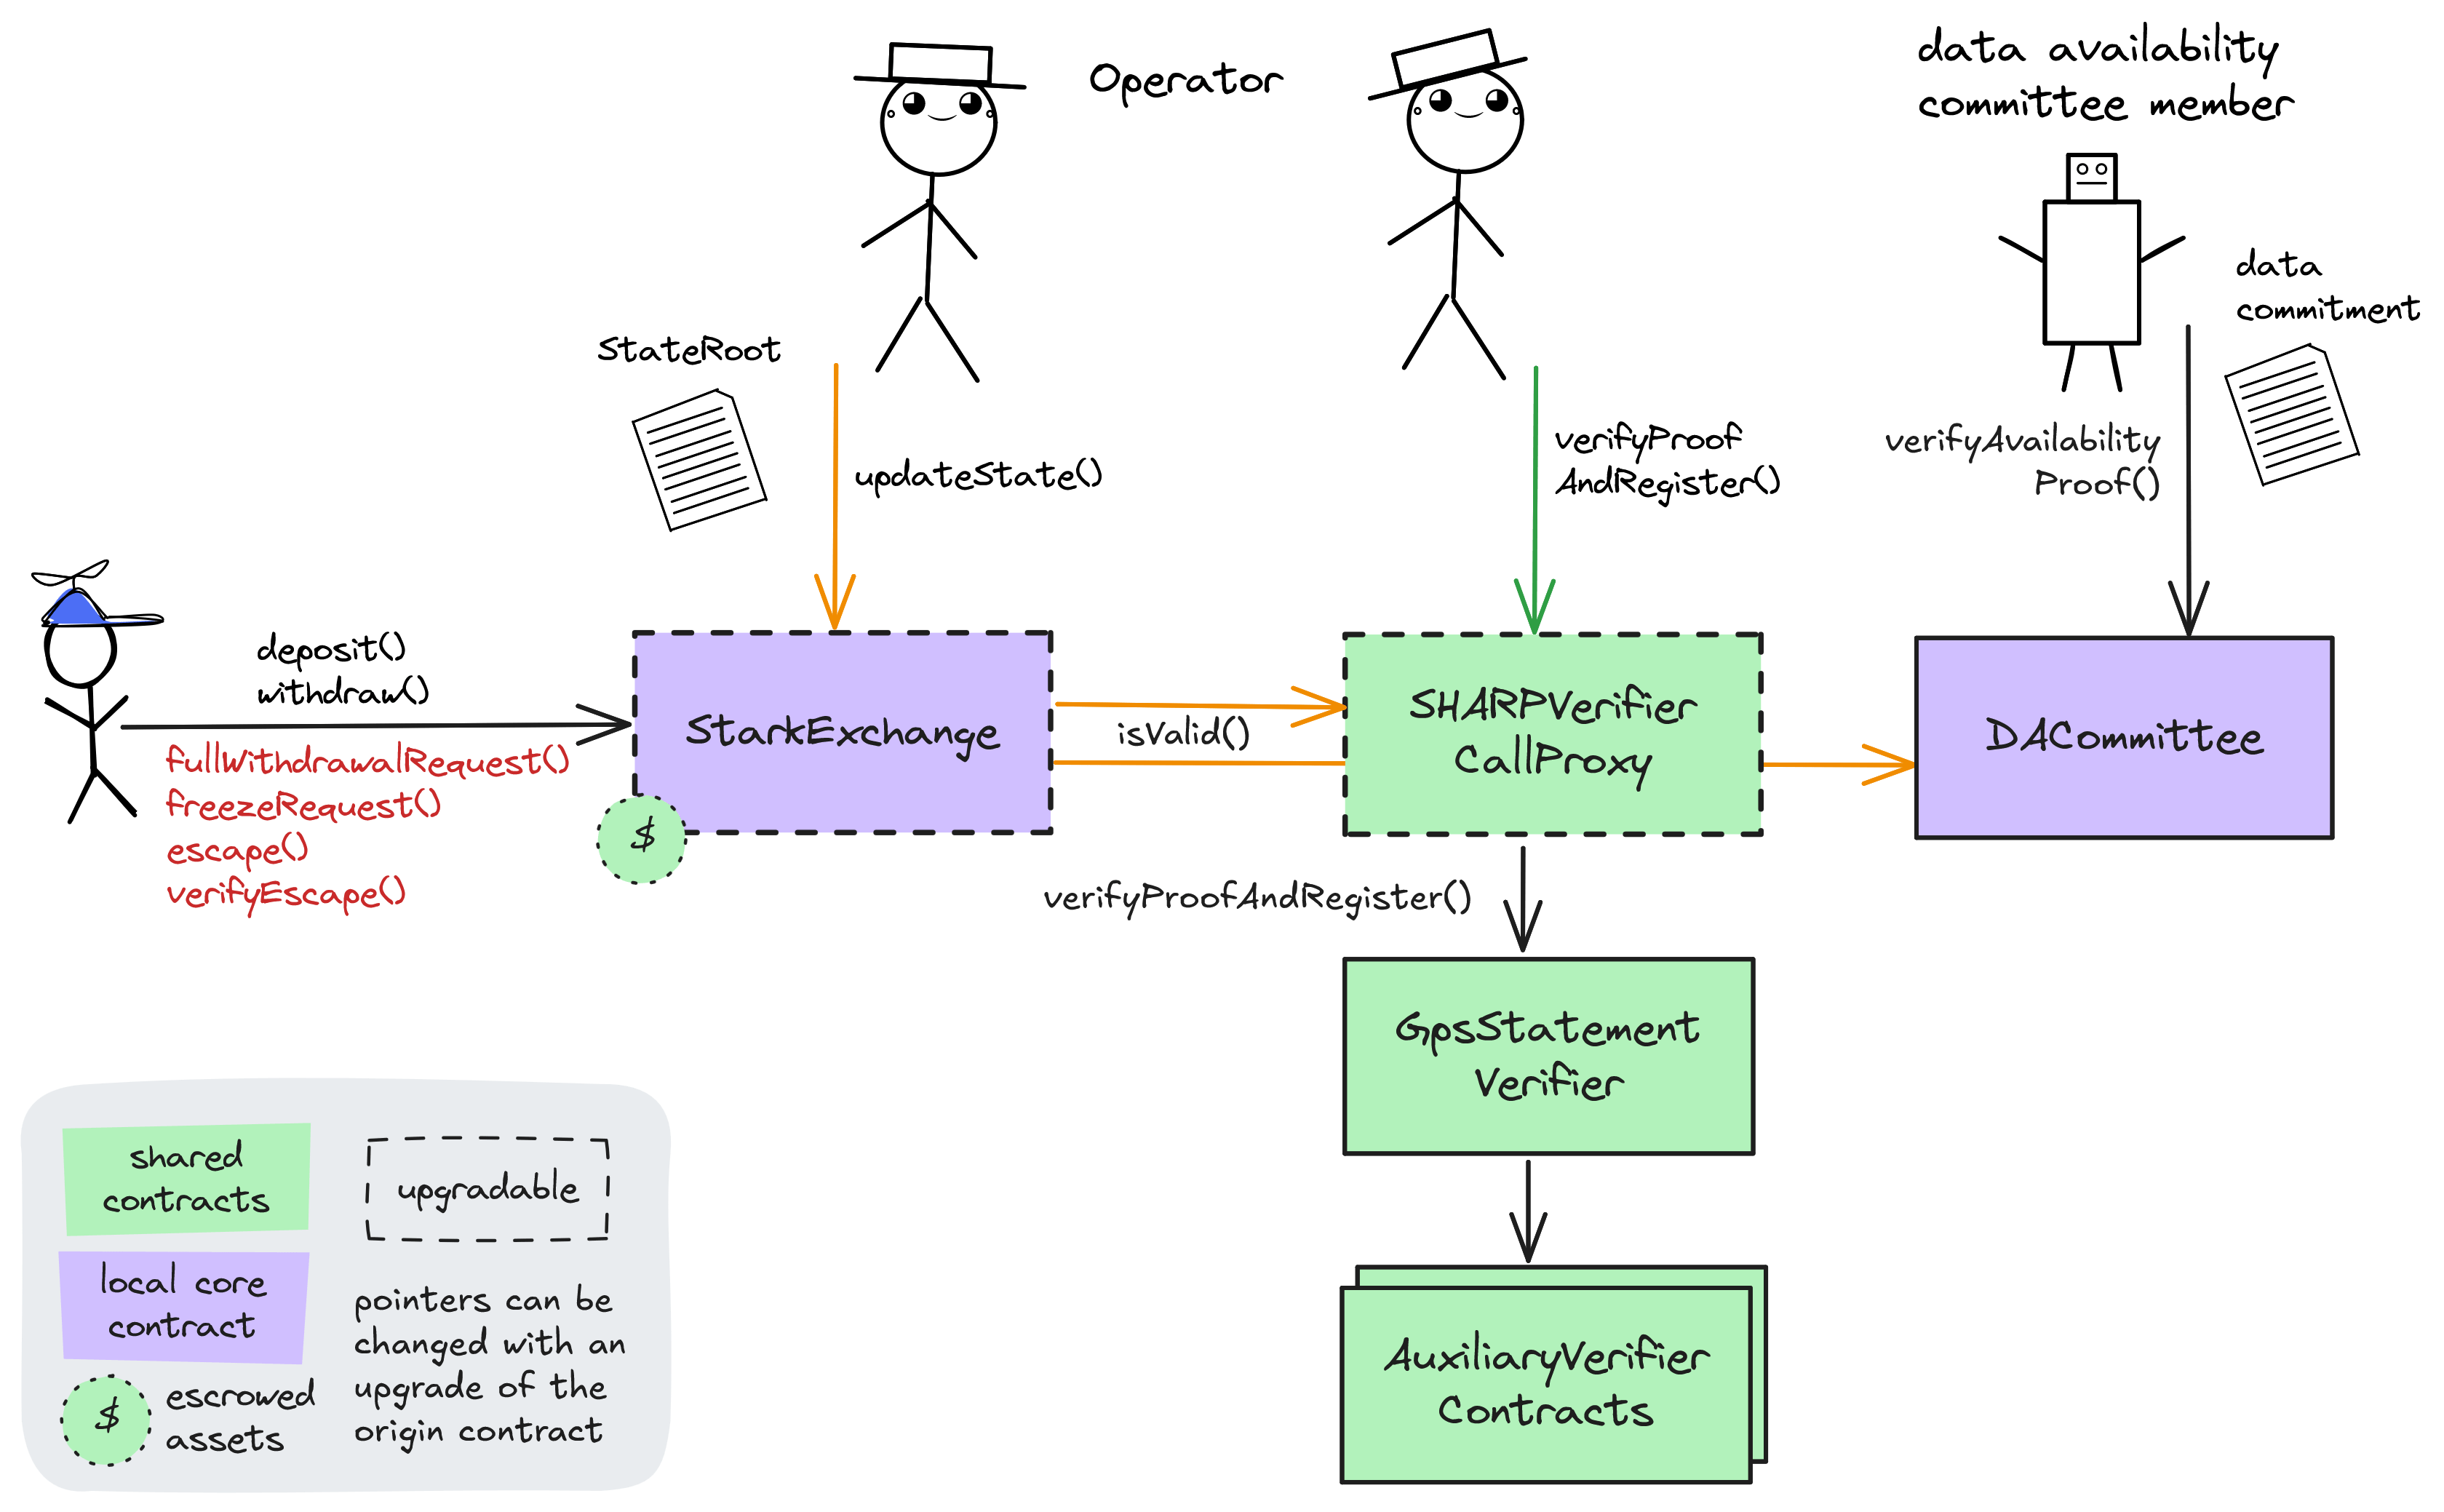
The Committee Verifier contract verifies the signatures and the data hash and if the required threshold of Committee members has signed off on the data, the hash is stored as a registeredFact in the StarkEx contract. In a separate transaction, the operator calls the updateState() function on the StarkEx contract to update the state. Before the state updateA mechanism that allows to update the claimed state of a project. It usually involves verifying a state transition proof, but it can also be done in a trusted manner by a permissioned actor. is accepted, the StarkEx contract verifies the transaction public inputs by calling the isValid() function, which verifies the hash derived from state update inputs matches the hash stored by the Committee Verifier contract.
Funds can be lost if a malicious committee signs a data availability attestation for an unavailable transaction batch.
Each update to the system state must be accompanied by a ZK proof that ensures that the new state was derived by correctly applying a series of valid user transactions to the previous state. These proofs are then verified on Ethereum by a smart contract. The system state is represented using Merkle roots.
Past upgrades
The metrics include upgrades on the currently used proxy contracts. Historical proxy contracts and changes of such are not included.
2025 July 22, 16:06 UTC1changeproject is archived.
project is archived.
| contract StarkPerpetualUSDC (0xA1D5443F2FB80A5A55ac804C948B45ce4C52DCbb) { | |
| +++ description: Central Validium contract. Receives (verified) state roots from the Operator, allows users to consume L2 -> L1 messages and send L1 -> L2 messages. Critical configuration values for the L2's logic are defined here by various governance roles. | |
| values.isFrozen: | |
| - | false |
| + | true |
| } | |
2025 July 14, 12:44 UTC8changesDiscovery rerun on the same block number with only config-related changes.
Discovery rerun on the same block number with only config-related changes.
New and verified contracts
| + | Status: CREATED |
| contract CommitteeUSDC (0x23Cab3CF1aa7B929Df5e9f3712aCA3A6Fb9494E4) | |
| +++ description: Data Availability Committee (DAC) contract verifying and storing data availability claims from DAC Members (via a multisignature check). The threshold of valid signatures is 3. | |
| + | Status: CREATED |
| contract FinalizableGpsFactAdapterUSDT (0x40e1e5Ece49A878062fA9F87eA6dc81281098B22) | |
| +++ description: Adapter between the core contract and the eth:0x47312450B3Ac8b5b8e247a6bB6d523e7605bDb60. Stores the Cairo programHash (`770346231394331402493200980986217737662224545740427952627288191358999988146`). | |
| + | Status: CREATED |
| contract CommitteeUSDT (0x7249082BfAFE9BCA502d38a686Ef3df37A0cf800) | |
| +++ description: Data Availability Committee (DAC) contract verifying and storing data availability claims from DAC Members (via a multisignature check). The threshold of valid signatures is 3. | |
| + | Status: CREATED |
| contract StarkPerpetualUSDC (0xA1D5443F2FB80A5A55ac804C948B45ce4C52DCbb) | |
| +++ description: Central Validium contract. Receives (verified) state roots from the Operator, allows users to consume L2 -> L1 messages and send L1 -> L2 messages. Critical configuration values for the L2's logic are defined here by various governance roles. | |
| + | Status: CREATED |
| contract PerpetualEscapeVerifier (0xaadFdB9CAc145c65f2284fBe24600d07fb37F7BD) | |
| +++ description: Special verifier for the escape() function. | |
| + | Status: CREATED |
| contract ApexAdminMultisig (0xC532d2976209A56DdF4a99B844130f7c0daCa7B6) | |
| +++ description: None | |
| + | Status: CREATED |
| contract StarkPerpetualUSDT (0xe53A6eD882Eb3f90cCe0390DDB04c876C5482E6b) | |
| +++ description: Central Validium contract. Receives (verified) state roots from the Operator, allows users to consume L2 -> L1 messages and send L1 -> L2 messages. Critical configuration values for the L2's logic are defined here by various governance roles. | |
| + | Status: CREATED |
| contract FinalizableGpsFactAdapterUSDC (0xE741e26573782ae3C0ea9EC710FA99Fcd27fB953) | |
| +++ description: Adapter between the core contract and the eth:0x47312450B3Ac8b5b8e247a6bB6d523e7605bDb60. Stores the Cairo programHash (`2530337539466159944237001094809327283009177793361359619481044346150483328860`). | |
2025 July 09, 09:25 UTC2changesUSDT StarkEx instance frozen, project archived. Apex Pro, the app on this StarkEx Validium, is EOL: https://www.apex.exchange/blog/detail/ApeX-Pro-Sunset-Delisting-Timeline-for-Trading-Pairs.
USDT StarkEx instance frozen, project archived.
Apex Pro, the app on this StarkEx Validium, is EOL: https://www.apex.exchange/blog/detail/ApeX-Pro-Sunset-Delisting-Timeline-for-Trading-Pairs.
| contract PerpetualEscapeVerifier (0xaadFdB9CAc145c65f2284fBe24600d07fb37F7BD) { | |
| +++ description: Special verifier for the escape() function. | |
| values.hasRegisteredFact: | |
| - | false |
| + | true |
| } | |
| contract StarkPerpetualUSDT (0xe53A6eD882Eb3f90cCe0390DDB04c876C5482E6b) { | |
| +++ description: Central Validium contract. Receives (verified) state roots from the Operator, allows users to consume L2 -> L1 messages and send L1 -> L2 messages. Critical configuration values for the L2's logic are defined here by various governance roles. | |
| values.isFrozen: | |
| - | false |
| + | true |
| } | |
2025 February 18, 09:12 UTCHigh severity14changesMinor upgrade to the StarkExchangeUSDC contract which is an implementation of StarkEx Perpetual. Two new asset IDs are added: - NON UNIQUE MINTABLE ASSET ID FLAG (ERC-1155) - MINTABLE ERC20 ASSET ID FLAG (ERC-20)
Minor upgrade to the StarkExchangeUSDC contract which is an implementation of StarkEx Perpetual.
Two new asset IDs are added:
- NON_UNIQUE_MINTABLE_ASSET_ID_FLAG (ERC-1155)
- MINTABLE_ERC20_ASSET_ID_FLAG (ERC-20)
| contract StarkExchangeUSDC (0xA1D5443F2FB80A5A55ac804C948B45ce4C52DCbb) { | |
| +++ description: None | |
| sourceHashes.5: | |
| - | "0x0c38b010717f86413abfb52412e5eb50b689b8d172e8c39ef81fc428fe5a1e52" |
| + | "0xe29824efd6d907d93d9b4b2b0737630ab974bce5e0017cb1459975c66a798280" |
| sourceHashes.4: | |
| - | "0xb8c0122f24ea2e559e908278def38aa80b6cd27b39b2d74402dbf5ba2585c7c5" |
| + | "0xdfa7b8bf4884e9f9933980cec5bcf744d2e522c291ed2a383c140cfb8c795f29" |
| sourceHashes.3: | |
| - | "0x473fc9765112e835124640cb91a4642354e09e94f92462929139d9ab5b6ddcf4" |
| + | "0xb5161e812087e15dd53a4c29ab296ade613b540445f7d1eb470de4f81a9c555c" |
| sourceHashes.2: | |
| - | "0x5ebd3f192c54b3d36f0d57e1cb14f418ae69a1694f7dc7d19d006883fc89e525" |
| + | "0xf6d00f2bc5db71a79b854049b38819f78c8fbbd98dcc2e4555f70946f6e58069" |
| sourceHashes.1: | |
| - | "0x758db67adde840068b01898c25f007a0d0549aaf9d431c2e0ae77ae4c2c56b33" |
| + | "0xc8c9c0e9c5171cb82b707e7e4b4ea80d427ba6f1dc21fc604efdce0ffa40323d" |
| values.$implementation.4: | |
| - | "0x34E7cfedF99995A47B3e3D0AB88ba67072B55035" |
| + | "0x31e2d974BaC547101413c24C23443AD488423f64" |
| values.$implementation.3: | |
| - | "0xdD5f42B087C1D2F73a2b443249b7D3DbE148a859" |
| + | "0x45de249eEa8f9CDB70943B17CceDeb42F5BA0175" |
| values.$implementation.2: | |
| - | "0x564EA75a26Dc0Bb5c5033B4752f88953A25AD058" |
| + | "0x1BC9C618B7FA6b5EfAAD31DC801eB55c608B9310" |
| values.$implementation.1: | |
| - | "0x533a7f4bE5453513049EB94A2b115F2CcE161dce" |
| + | "0x540Ad8576d2F90f28994ab001622F964945854A8" |
| values.$implementation.0: | |
| - | "0xdD813397b79f8df581eEb0c4B8aB72304c528396" |
| + | "0x8C43C9bec15d82D153C52518030e0a9590ABD35d" |
| values.$pastUpgrades.4: | |
| + | ["2025-02-17T09:39:23.000Z","0x7c6ca54630321bc1f0e2ad0b68972ec3f6efaab449f09839ef612f90d4292bdd",["0x8C43C9bec15d82D153C52518030e0a9590ABD35d","0x540Ad8576d2F90f28994ab001622F964945854A8","0x1BC9C618B7FA6b5EfAAD31DC801eB55c608B9310","0x45de249eEa8f9CDB70943B17CceDeb42F5BA0175","0x31e2d974BaC547101413c24C23443AD488423f64"]] |
| values.$upgradeCount: | |
| - | 4 |
| + | 5 |
| values.implementation: | |
| - | "0xdD813397b79f8df581eEb0c4B8aB72304c528396" |
| + | "0x8C43C9bec15d82D153C52518030e0a9590ABD35d" |
| values.VERSION: | |
| - | "3.1.0" |
| + | "3.2.0" |
| } | |
2025 January 30, 10:24 UTC2changesUpdates progHash, not found online, added to the library.
Updates progHash, not found online, added to the library.
| contract StarkExchangeUSDC (0xA1D5443F2FB80A5A55ac804C948B45ce4C52DCbb) { | |
| +++ description: None | |
| values.globalConfigurationHash: | |
| - | "0x01897348c8e7a04145727a7d369a76c01711a828d58afeca4c3e7d86596b85ba" |
| + | "0x0274c9dc2096cfe79c5f28f5bfb3a95b3bd0692430b4f9ba79f871068611804a" |
| } | |
| contract FinalizableGpsFactAdapterUSDC (0xE741e26573782ae3C0ea9EC710FA99Fcd27fB953) { | |
| +++ description: None | |
| values.programHash: | |
| - | "3114724292040200590153042023978438629733352741898912919152162079752811928849" |
| + | "2530337539466159944237001094809327283009177793361359619481044346150483328860" |
| } | |
The system has a centralized operator
The operatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades. is the only entity that can propose blocksAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over.. A live and trustworthy operator is vital to the health of the system. Typically, the Operator is the hot wallet of the StarkEx service submitting state updates for which proofs have been already submitted and verified.
MEV can be extracted if the operator exploits their centralized position and frontruns user transactions.
Users can force exit the system
Force exit allows the users to escape censorship by withdrawing their funds. The system allows users to force the withdrawal of funds by submitting a request directly to the contract onchain. The request must be served within 7d. If this does not happen, the system will halt regular operation and permit trustless withdrawal of funds. Perpetual positions can also be force closed before withdrawing, however this requires the user to find the counterparty for the trade themselves.
Users can be censored if the operator refuses to include their transactions. However, there exists a mechanism to independently exit the system.
Funds can be lost if the user is unable to find the counterparty for the force trade.
Regular exit
The user initiates the withdrawal by submitting a regular transaction on this chain. When the blockAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over. containing that transaction is settled the funds become available for withdrawal on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development.. ZK proofs are required to settle blocks. Finally the user submits an L1 transaction to claim the funds.
Forced exit
If the user experiences censorship from the operatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades. with regular exit they can submit their withdrawal requests directly on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development.. The system is then obliged to service this request. Once the force operation is submitted and if the request is serviced, the operation follows the flow of a regular exit.
Emergency exit
If the enough time deadline passes and the forced exit is still ignored the user can put the system into a frozen state, disallowing further state updates. In that case everybody can withdraw by submitting a merkle proof of their funds with their L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. transaction.
Ethereum
Actors:
A Multisig with 2/2 threshold.
- Can upgrade with no delay or with 14d delay
- StarkPerpetualUSDC - or - acting directly with 14d delay
- Can interact with StarkPerpetualUSDC
- manage the token admin role
- Permissioned to appoint and remove the OperatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades., register additional verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. and availability verifier contracts (removals are delayed), unfreeze the exchange and manage the governor set
A Multisig with 2/4 threshold.
- Can upgrade with 8d delay
- SHARPVerifierCallProxy - acting directly with 8d delay
- Can interact with SHARPVerifierCallProxy
- Administer the CallProxy’s
GOVERNANCE_ADMINand role-admin hierarchy. This AccessControl role is separate from the outer proxy governor that schedules implementation upgrades - Grant and revoke application roles, including the
APP_GOVERNORrole that controls caller-specific fallback routes - Route fallback calls from specific callers to a still-active registry in the default verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover.’s reference chain. This principally determines which verifier and bootloader configuration processes their proof submissions; the proxy’s explicit
isValidentry point always queries the default target
- Administer the CallProxy’s
- Can upgrade with no delay or with 14d delay
- StarkPerpetualUSDT - or - acting directly with 14d delay
- Can interact with StarkPerpetualUSDT
- manage the token admin role
- Permissioned to appoint and remove the OperatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades., register additional verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. and availability verifier contracts (removals are delayed), unfreeze the exchange and manage the governor set
- Can upgrade with no delay
- FinalizableGpsFactAdapterUSDT
- FinalizableGpsFactAdapterUSDC
- Can interact with StarkPerpetualUSDC
- manage supported tokens
- Permissioned to regularly update the state of the L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development.. Each state updateA mechanism that allows to update the claimed state of a project. It usually involves verifying a state transition proof, but it can also be done in a trusted manner by a permissioned actor. must have been proven via the SHARP verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. and contains state diffs for data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium.
- Can interact with StarkPerpetualUSDT
- manage supported tokens
- Permissioned to regularly update the state of the L2 on L1. Each state update must have been proven via the SHARP verifier and contains state diffs for data availability
Member of ApexAdminMultisig.
- Can upgrade with no delay or with 14d delay
- StarkPerpetualUSDC - or - acting directly with 14d delay
- Can interact with StarkPerpetualUSDC
- manage the token admin role
- Permissioned to appoint and remove the OperatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades., register additional verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. and availability verifier contracts (removals are delayed), unfreeze the exchange and manage the governor set
- Can interact with StarkPerpetualUSDT
- Permissioned to regularly update the state of the L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development.. Each state updateA mechanism that allows to update the claimed state of a project. It usually involves verifying a state transition proof, but it can also be done in a trusted manner by a permissioned actor. must have been proven via the SHARP verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. and contains state diffs for data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium.
- Can interact with StarkPerpetualUSDC
- Permissioned to regularly update the state of the L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development.. Each state updateA mechanism that allows to update the claimed state of a project. It usually involves verifying a state transition proof, but it can also be done in a trusted manner by a permissioned actor. must have been proven via the SHARP verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. and contains state diffs for data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium.
Ethereum
Data Availability Committee (DAC)A set of members whose task is attesting and ensuring that the data is available for the public. An onchain DAC verifier checks that a threshold of signatures from the DAC members is reached before considering a data commitment as available and therefore valid to be used in the system. contract verifying and storing data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium. claims from DAC Members (via a multisignature check). The threshold of valid signatures is 3.
Data Availability Committee (DAC)A set of members whose task is attesting and ensuring that the data is available for the public. An onchain DAC verifier checks that a threshold of signatures from the DAC members is reached before considering a data commitment as available and therefore valid to be used in the system. contract verifying and storing data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium. claims from DAC Members (via a multisignature check). The threshold of valid signatures is 3.
Central ValidiumAn off-chain solution that uses validity proofs for settlement and publishes the data offchain, therefore requiring an additional trust assumption. contract. Receives (verified) state rootsA cryptographic hash succinctly representing a state using a Merkle tree. from the OperatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades., allows users to consume L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. -> L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. messages and send L1 -> L2 messages. Critical configuration values for the L2’s logic are defined here by various governance roles.
- Roles:
- admin: ApexAdminMultisig, EOA 3
- operators: EOA 2, EOA 5
- tokenAdmins: EOA 2
Central ValidiumAn off-chain solution that uses validity proofs for settlement and publishes the data offchain, therefore requiring an additional trust assumption. contract. Receives (verified) state rootsA cryptographic hash succinctly representing a state using a Merkle tree. from the OperatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades., allows users to consume L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. -> L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. messages and send L1 -> L2 messages. Critical configuration values for the L2’s logic are defined here by various governance roles.
- Roles:
- admin: EOA 1
- operators: EOA 2, EOA 4
- tokenAdmins: EOA 2
Immutable Solidity verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for one Cairo CPU layout. It checks the STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof using layout-specific constraint, OODS, Merkle, FRIA proximity test method that is used to determine whether a set of points is mostly on a polynomial with a degree less than a specified value. It resembles the FFT but the arithmetic complexity of its prover is strictly linear and that of the verifier is strictly logarithmic., and periodic-column helper contracts. The SHARP verifier can select any configured layout by cairoVerifierId.
Immutable Solidity verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for one Cairo CPU layout. It checks the STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof using layout-specific constraint, OODS, Merkle, FRIA proximity test method that is used to determine whether a set of points is mostly on a polynomial with a degree less than a specified value. It resembles the FFT but the arithmetic complexity of its prover is strictly linear and that of the verifier is strictly logarithmic., and periodic-column helper contracts. The SHARP verifier can select any configured layout by cairoVerifierId.
Stores the complete compiled Cairo outer bootloader used as the top-level program of a SHARP proof. The SHARP verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. copies these words into public memory, pinning this exact executable onchain independently of the separately committed simple, applicative, and recursive-verifier programs.
Immutable Solidity verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for one Cairo CPU layout. It checks the STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof using layout-specific constraint, OODS, Merkle, FRIA proximity test method that is used to determine whether a set of points is mostly on a polynomial with a degree less than a specified value. It resembles the FFT but the arithmetic complexity of its prover is strictly linear and that of the verifier is strictly logarithmic., and periodic-column helper contracts. The SHARP verifier can select any configured layout by cairoVerifierId.
Immutable Solidity verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for one Cairo CPU layout. It checks the STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof using layout-specific constraint, OODS, Merkle, FRIA proximity test method that is used to determine whether a set of points is mostly on a polynomial with a degree less than a specified value. It resembles the FFT but the arithmetic complexity of its prover is strictly linear and that of the verifier is strictly logarithmic., and periodic-column helper contracts. The SHARP verifier can select any configured layout by cairoVerifierId.
PermissionlessAnyone willing should be able to join and leave the network at any time, without causing significant disturbance to the network or being detrimental to the party in question. No single entity should have the power to allowlist or blocklist participants. commitment calculator and registry used by the Solidity STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. verifiers. Anyone may submit a public-memory page and interaction elements; the contract computes its hashA fixed-length fingerprint of variable-size input, produced by a hash function. and cumulative product and registers the fact key committing to them, which the CPU verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. must bind to the proof. It is part of the proof verifier, not an application-level program registry. A malicious or nonconforming implementation can break public-memory soundness; binding to a different honest registry generally causes a livenessLiveness refers to the ability of a system to respond to requests and to process them in a timely manner. In the context of L2s, it refers to the ability of settling transactions, proofs and state roots to the base layer. failure instead.
Upgradeable call router through which Starknet and other applications access SHARP fact registries. It uses call, not delegatecall, so facts and immutable verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. configuration remain at each target registry. The explicit isValid entry point always queries the default target. Other calls handled by the fallback, principally proof submissions, can be routed per caller to a still-active registry in the default target’s reference chain. The default target can be replaced by SHARP Multisig after 8d.
- Roles:
- admin: SHARP Multisig
- appGovernor: SHARP Multisig
- appRoleAdmin: SHARP Multisig
- governanceAdmin: SHARP Multisig
Immutable GPS statement verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. shared by Starknet and other StarkWare systems. It verifies a STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof of the exact Cairo bootloader stored onchain, forces the bootloader configuration into public memory, and registers a fact for every bootloader task. A fact is also considered valid when it exists in the time-limited reference fact registry.
Immutable GPS statement verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. shared by Starknet and other StarkWare systems. It verifies a STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof of the exact Cairo bootloader stored onchain, forces the bootloader configuration into public memory, and registers a fact for every bootloader task. A fact is also considered valid when it exists in the time-limited reference fact registry.
Immutable Solidity verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for one Cairo CPU layout. It checks the STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof using layout-specific constraint, OODS, Merkle, FRIA proximity test method that is used to determine whether a set of points is mostly on a polynomial with a degree less than a specified value. It resembles the FFT but the arithmetic complexity of its prover is strictly linear and that of the verifier is strictly logarithmic., and periodic-column helper contracts. The SHARP verifier can select any configured layout by cairoVerifierId.
Immutable Solidity verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for one Cairo CPU layout. It checks the STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof using layout-specific constraint, OODS, Merkle, FRIA proximity test method that is used to determine whether a set of points is mostly on a polynomial with a degree less than a specified value. It resembles the FFT but the arithmetic complexity of its prover is strictly linear and that of the verifier is strictly logarithmic., and periodic-column helper contracts. The SHARP verifier can select any configured layout by cairoVerifierId.
Immutable GPS statement verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. shared by Starknet and other StarkWare systems. It verifies a STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof of the exact Cairo bootloader stored onchain, forces the bootloader configuration into public memory, and registers a fact for every bootloader task. A fact is also considered valid when it exists in the time-limited reference fact registry.
Immutable Solidity verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for one Cairo CPU layout. It checks the STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof using layout-specific constraint, OODS, Merkle, FRIA proximity test method that is used to determine whether a set of points is mostly on a polynomial with a degree less than a specified value. It resembles the FFT but the arithmetic complexity of its prover is strictly linear and that of the verifier is strictly logarithmic., and periodic-column helper contracts. The SHARP verifier can select any configured layout by cairoVerifierId.
PermissionlessAnyone willing should be able to join and leave the network at any time, without causing significant disturbance to the network or being detrimental to the party in question. No single entity should have the power to allowlist or blocklist participants. commitment calculator and registry used by the Solidity STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. verifiers. Anyone may submit a public-memory page and interaction elements; the contract computes its hashA fixed-length fingerprint of variable-size input, produced by a hash function. and cumulative product and registers the fact key committing to them, which the CPU verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. must bind to the proof. It is part of the proof verifier, not an application-level program registry. A malicious or nonconforming implementation can break public-memory soundness; binding to a different honest registry generally causes a livenessLiveness refers to the ability of a system to respond to requests and to process them in a timely manner. In the context of L2s, it refers to the ability of settling transactions, proofs and state roots to the base layer. failure instead.
Immutable GPS statement verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. shared by Starknet and other StarkWare systems. It verifies a STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof of the exact Cairo bootloader stored onchain, forces the bootloader configuration into public memory, and registers a fact for every bootloader task. A fact is also considered valid when it exists in the time-limited reference fact registry.
Immutable Solidity verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for one Cairo CPU layout. It checks the STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof using layout-specific constraint, OODS, Merkle, FRIA proximity test method that is used to determine whether a set of points is mostly on a polynomial with a degree less than a specified value. It resembles the FFT but the arithmetic complexity of its prover is strictly linear and that of the verifier is strictly logarithmic., and periodic-column helper contracts. The SHARP verifier can select any configured layout by cairoVerifierId.
Adapter between the core contract and the SHARPVerifierCallProxy. Stores the Cairo programHash (770346231394331402493200980986217737662224545740427952627288191358999988146), which can be changed until the adapter is finalized.
- Roles:
- owner: EOA 2 if the adapter is not finalized
Special verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for the escape() function.
Adapter between the core contract and the SHARPVerifierCallProxy. Stores the Cairo programHash (2530337539466159944237001094809327283009177793361359619481044346150483328860), which can be changed until the adapter is finalized.
- Roles:
- owner: EOA 2 if the adapter is not finalized
The current deployment carries some associated risks:
Funds can be stolen if a contract receives a malicious code upgrade. There is a 8d delay on code upgrades.