Search
Search for projects by name or address
 Aleph Zero EVM
Badges
About
Aleph Zero is an Optimium on Ethereum, built on the Orbit stack. It aims to offer seamless interoperability with the Aleph Zero Layer 1 and a suite of developer tools for building privacy-enhancing dapps.
Badges
About
Aleph Zero is an Optimium on Ethereum, built on the Orbit stack. It aims to offer seamless interoperability with the Aleph Zero Layer 1 and a suite of developer tools for building privacy-enhancing dapps.
Why is the project listed in others?
Consequence: projects without a sufficiently decentralized set of challengers rely on few entities to safely update the state. A small set of challengers can collude with the proposer to finalize an invalid state, which can cause loss of funds.
Consequence: projects without a sufficiently decentralized data availability committee rely on few entities to safely attest data availability on Ethereum. A small set of entities can collude with the proposer to finalize an unavailable state, which can cause loss of funds.
Learn more about the recategorisation here.
The section shows the operating costs that L2s pay to Ethereum.
This section shows how "live" the project's operators are by displaying how frequently they submit transactions of the selected type. It also highlights anomalies - significant deviations from their typical schedule.
Mainnet Launch
2024 Aug 12th
Aleph Zero EVM L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. is open for all users.
Funds can be stolen if
- a contract receives a malicious code upgrade. There is no delay on code upgrades (CRITICAL),
- none of the whitelisted verifiers checks the published state. Fraud proofs assume at least one honest and able validator (CRITICAL),
- validators with the 'fast-confirmer' permission finalize a malicious state root before the challenge period has passed (CRITICAL).
Funds can be lost if
Users can be censored if
MEV can be extracted if
In the event of a sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. failure, users can force transactions to be included in the project’s chain by sending them to L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development.. There can be up to a 4d delay on this operation.
Fraud proofs allow 6 WHITELISTED actors watching the chain to prove that the state is incorrect. There are fewer than 5 Challengers external to the OperatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades. among these. Interactive proofs (INT) require multiple transactions over time to resolve. There is a 6d 8h challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled..
Proof construction relies fully on data that is NOT published onchain. There exists a Data Availability Committee (DAC)A set of members whose task is attesting and ensuring that the data is available for the public. An onchain DAC verifier checks that a threshold of signatures from the DAC members is reached before considering a data commitment as available and therefore valid to be used in the system. with a threshold of 1/2 that is tasked with protecting and supplying the data.
There is no window for users to exit in case of an unwanted upgrade since contracts are instantly upgradable.
Anyone can become a ProposerIn the context of L2s, the actor that proposes a claimed state root on L1. The term is also used in the context of Ethereum to refer to the actor that proposes a new block. after 12d 17h of inactivity from the currently whitelisted Proposers.
Set of parties responsible for signing and attesting to the availability of data.
There are no onchain assets at risk of being slashed in case of a data withholding attack, and the committee members are not publicly known.
There is no fraud detection mechanism in place. A data withholding attack can only be detected by nodes downloading the full data from the DA layerAn infrastructure that is used to make publish data so that it's available to the public. They take the form of Data Availability Committees (DACs) or blockchains. Not to confuse with the layer responsible with ordering, since ordering and DA can be separated..
The committee does not meet basic security standards, either due to insufficient size, lack of member diversity, or poorly defined threshold parameters. The system lacks an effective DA bridgeSystem that verifies that data has been made available. It takes the form of a smart contract verifying a consensus or, if the data is verified directly by either downloading the full data or sampling, of an enshrined bridge. and it is reliant on the assumption of an honest sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs., creating significant risks to data integrity and availability.
There is no delay in the upgradeabilityThe ability for rollup smart contracts and parameters used in a rollup to be updated by holders of an admin key. Upgradeability represents a vector of risk for users, and should be decentralized and combined with time delays for greater security guarantees. of the bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge.. Users have no time to exit the system before the bridge implementation update is completed.
The relayer role is permissioned, and the DA bridgeSystem that verifies that data has been made available. It takes the form of a smart contract verifying a consensus or, if the data is verified directly by either downloading the full data or sampling, of an enshrined bridge. does not have a Security CouncilA Security Council is a sufficiently decentralized set of members that is able to upgrade a system. A properly set up Security Council consists of at least 8 members with a threshold greater than 75%. What 'sufficiently decentralized' means is fundamentally subjective and L2BEAT evaluates each case individually. A Security Council is allowed to instantly upgrade Stage 1 rollups. or a governance mechanism to propose new relayers. In case of relayer failure, the DA bridge will halt and be unable to recover without the intervention of a centralized entity.
Architecture
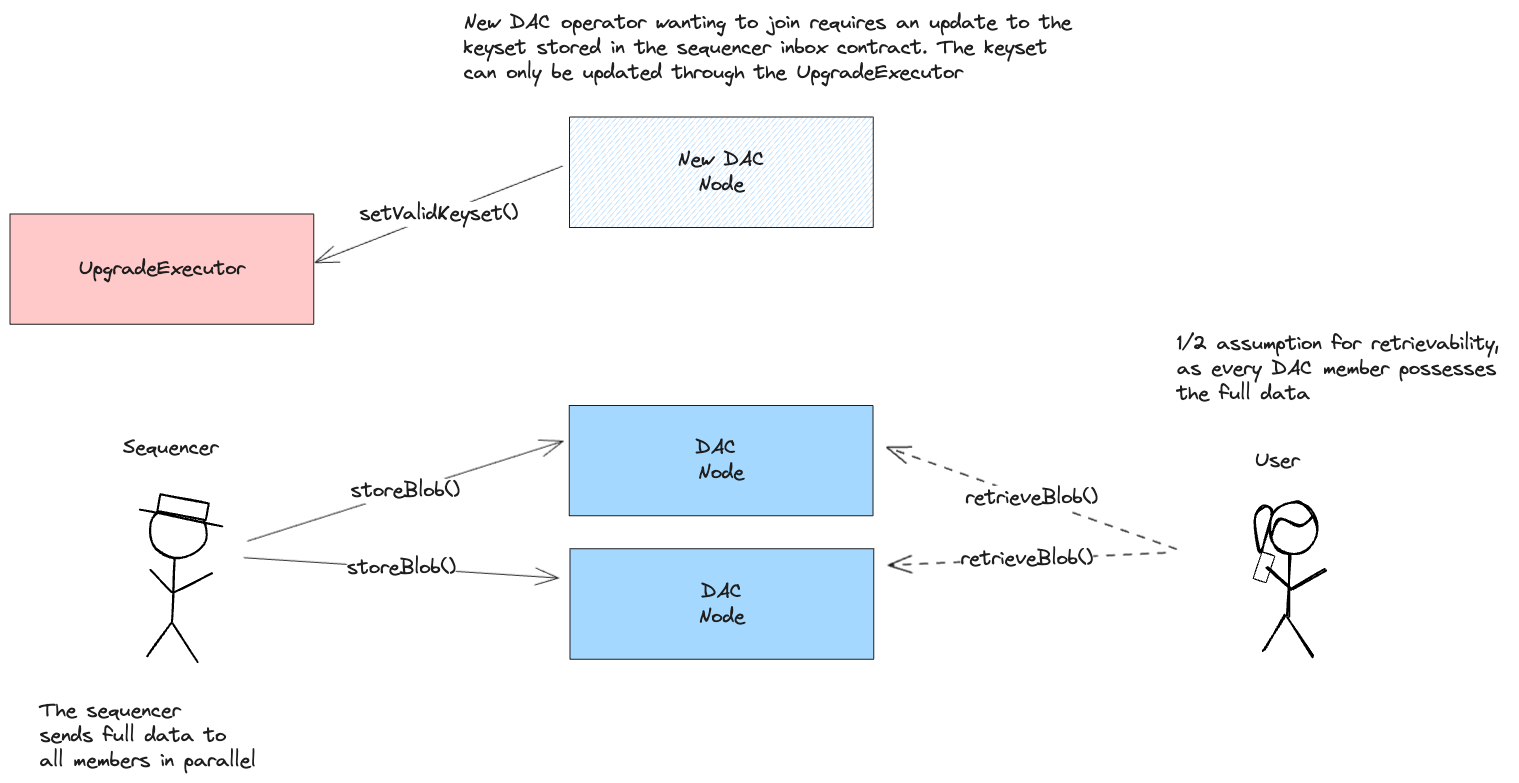
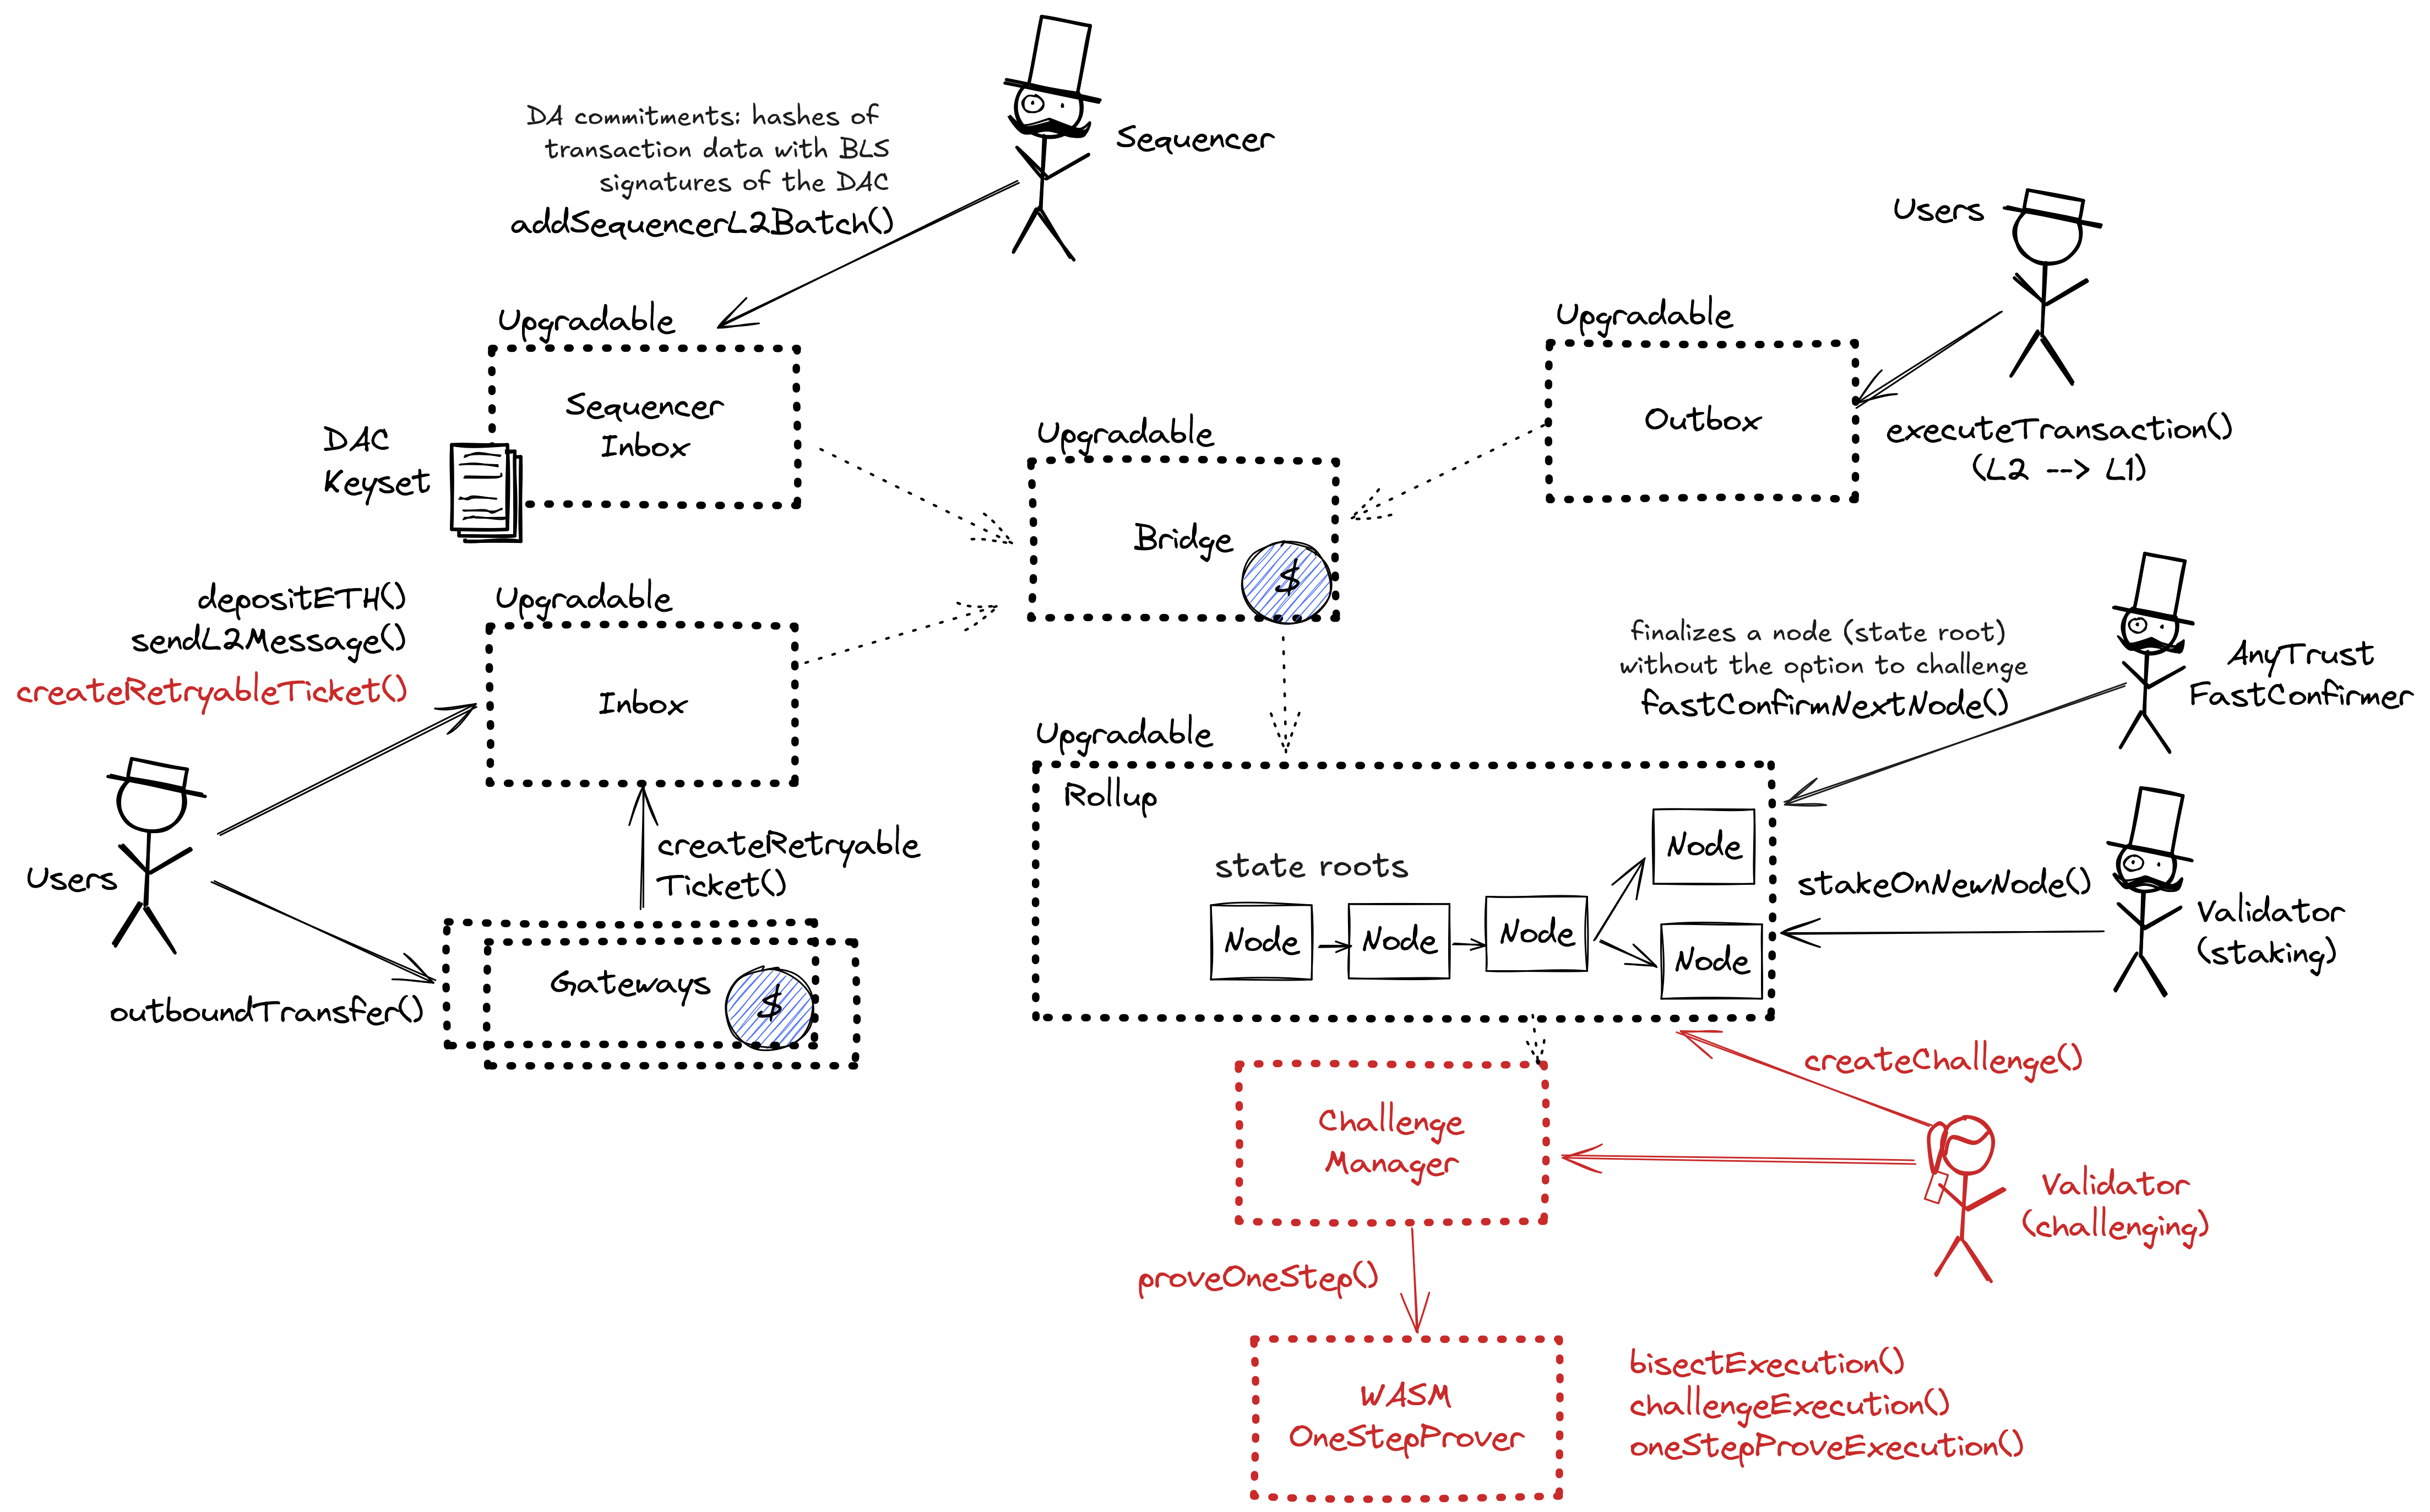
The DAC uses a data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium. solution built on the AnyTrust protocol. It is composed of the following components:
- SequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. Inbox: Main entry point for the Sequencer submitting transaction batches.
- Data Availability Committee (DAC)A set of members whose task is attesting and ensuring that the data is available for the public. An onchain DAC verifier checks that a threshold of signatures from the DAC members is reached before considering a data commitment as available and therefore valid to be used in the system.: A group of members responsible for storing and providing data on demand.
- Data Availability Certificate (DACert): A commitment ensuring that data blobsThe data that a rollup publishes to its L1/data availability (DA) layer. They consist of the L2 transactions that are rolled up, along with some metadata. Blobs are introduced as a new transaction type within Ethereum with EIP-4844, and has rollup scaling specifically in mind. Blobs persist on Ethereum’s Beacon Chain ephemerally. are available without needing full data posting on the L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. chain.
Committee members run servers that support APIs for storing and retrieving data blobs. The Sequencer API allows the rollupA blockchain that inherits consensus and data availability from another blockchain called L1. Rollups enable trust minimized bridges with the base layer via proof systems, either optimistic or zero-knowledge. A rollup without a bridge, or without considering the bridge, is called a sovereign rollup. Sequencer to submit data blobs for storage, while the REST API enables anyone to fetch data by hashA fixed-length fingerprint of variable-size input, produced by a hash function.. When the Sequencer produces a data batch, it sends the batch along with an expiration time to Committee members, who store it and sign it. Once enough signatures are collected, the Sequencer aggregates them into a valid DACert and posts it to the L1 chain inbox. If the Sequencer fails to collect enough signatures, it falls back to posting the full data to the L1 chain as calldata.
A DACert includes a hash of the data blockAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over., an expiration time, and proof that the required threshold of Committee members have signed off on the data. The proof consists of a hash of the Keyset used in signing, a bitmap indicating which members signed, and a BLS aggregated signature. L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. nodes reading from the sequencer inbox verify the certificate’s validity by checking the number of signers, the aggregated signature, and that the expiration time is at least two weeks ahead of the L2 timestamp. If the DACert is valid, it provides a proof that the corresponding data is available from honest committee members.
DA BridgeSystem that verifies that data has been made available. It takes the form of a smart contract verifying a consensus or, if the data is verified directly by either downloading the full data or sampling, of an enshrined bridge. Architecture
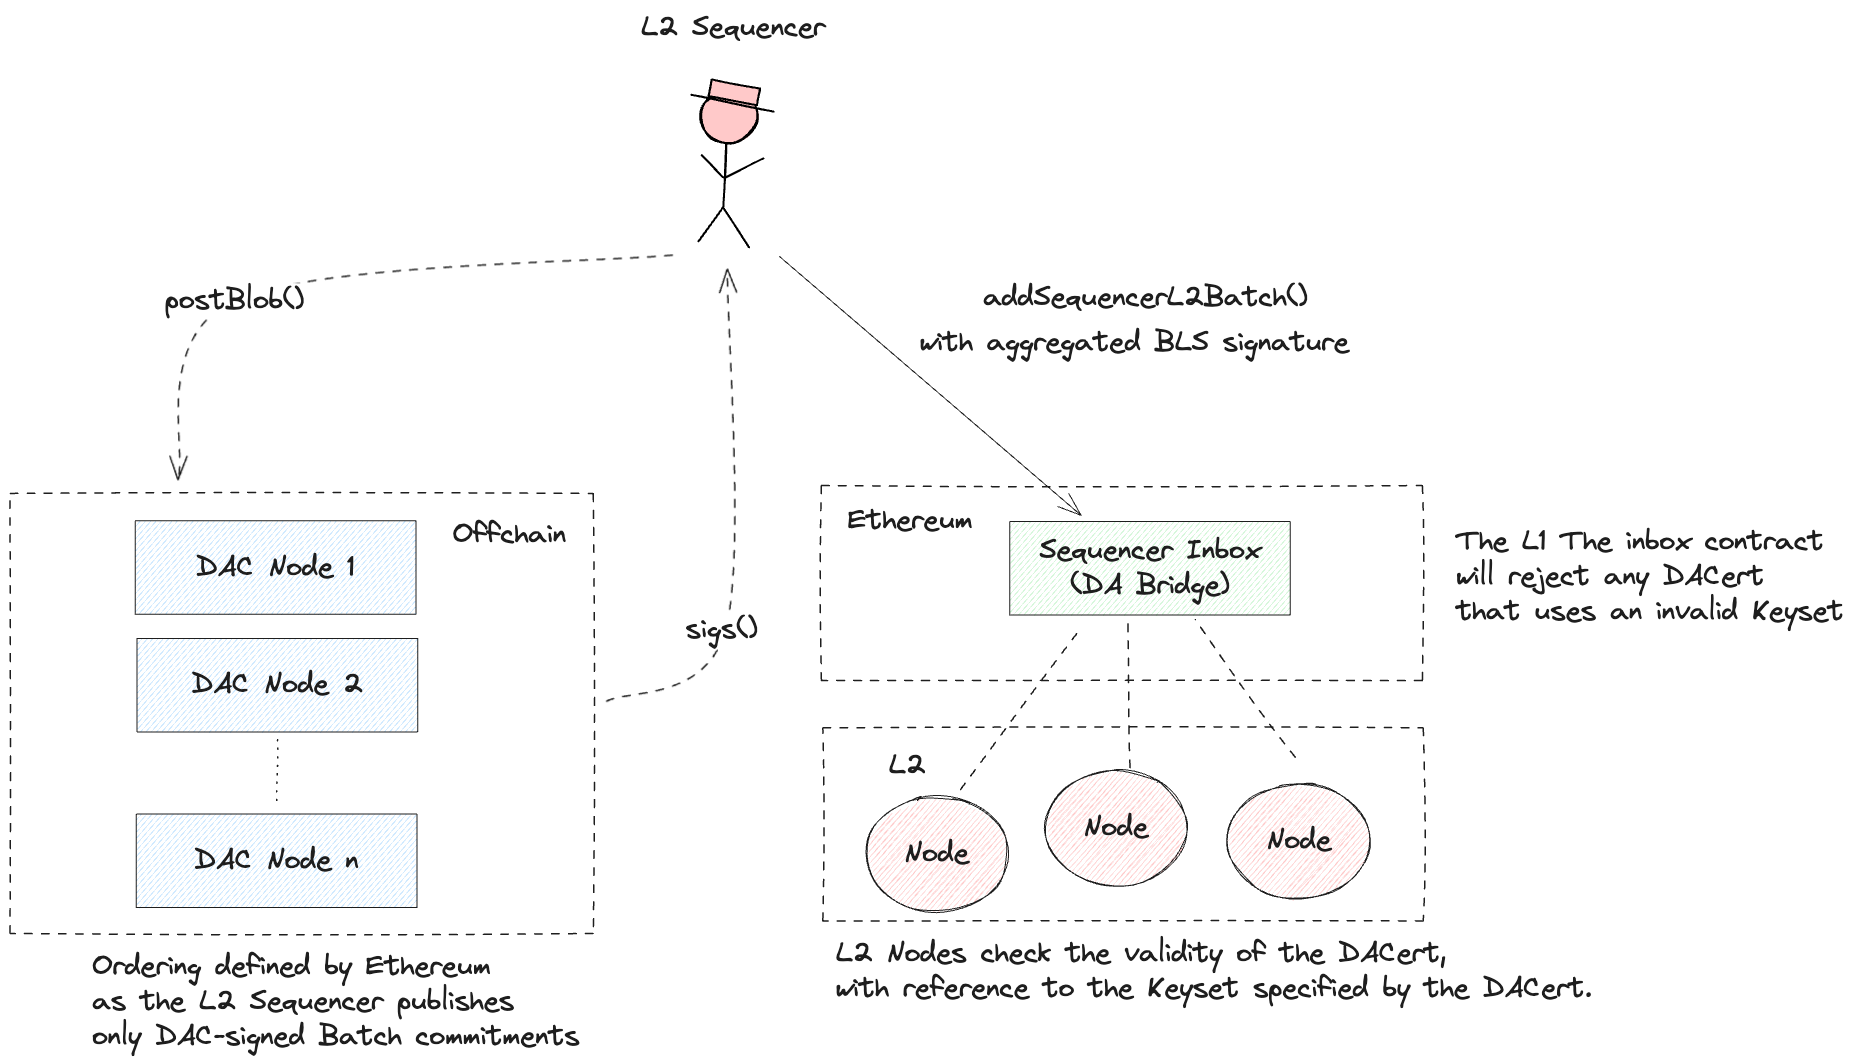
The DA commitments are posted to the destination chain through the sequencer inbox, using the inbox as a DA bridge. The DA commitment consists of Data Availability Certificate (DACert), including a hash of the data block, an expiration time, and a proof that the required threshold of Committee members have signed off on the data. The sequencer distributes the data and collects signatures from Committee members offchain. Only the DACert is posted by the sequencer to the destination chain inbox (the DA bridge), achieving destination chain transaction ordering finalityStrongest confirmation rule that can be given on the ordering of transactions. On Ethereum, a transaction is finalized when the corresponding epoch becomes final, which currently takes around 15 mins from transaction inclusion. A rollup transaction can be said to be final when the corresponding data is published to L1 and its ordering cannot be reverted. If outputs, i.e. state diffs are published, then also a proof proving their correctness must be verified to consider the transaction final. in a single onchain transaction.
Funds can be lost if a malicious committee attests to an invalid data availability certificate.
Funds can be lost if the bridge contract or its dependencies receive a malicious code upgrade. There is no delay on code upgrades.
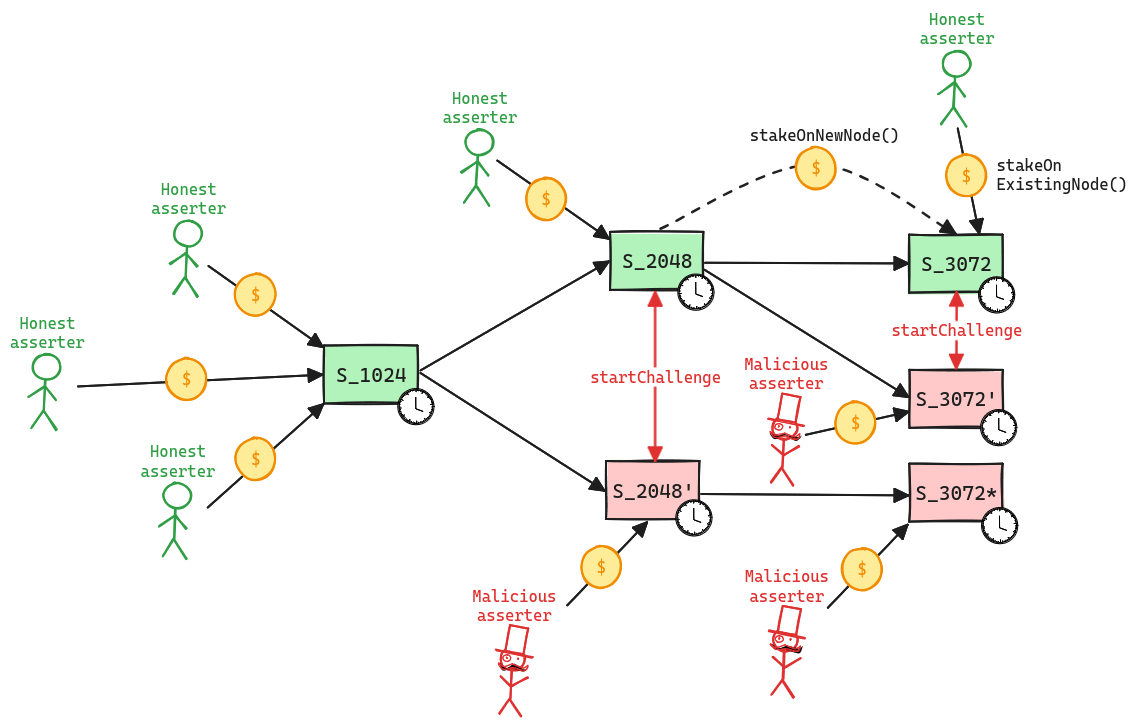
Updates to the system state can be proposed and challenged by a set of whitelisted validatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier. If a state rootA cryptographic hash succinctly representing a state using a Merkle tree. passes the challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled., it is optimistically considered correct and made actionable for withdrawals.
Whitelisted validatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier propose state rootsA cryptographic hash succinctly representing a state using a Merkle tree. as children of a previous state root. A state root can have multiple conflicting children. This structure forms a graph, and therefore, in the contracts, state roots are referred to as nodes. Each proposal requires a stake, currently set to 0.1 ETH, that can be slashed if the proposal is proven incorrect via a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system.. Stakes can be moved from one nodeA software client that participates in the network. to one of its children, either by calling stakeOnExistingNode or stakeOnNewNode. New nodes cannot be created faster than the minimum assertion period by the same validator, currently set to 15m. The oldest unconfirmed node can be confirmed if the challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled. has passed and there are no siblings, and rejected if the parent is not a confirmed node or if the challenge period has passed and no one is staked on it.
Funds can be stolen if none of the whitelisted verifiers checks the published state. Fraud proofs assume at least one honest and able validator (CRITICAL).
A challenge can be started between two siblings, i.e. two different state rootsA cryptographic hash succinctly representing a state using a Merkle tree. that share the same parent, by calling the startChallenge function. ValidatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier cannot be in more than one challenge at the same time, meaning that the protocol operates with partial concurrency. Since each challenge lasts 6d 8h, this implies that the protocol can be subject to delay attacks, where a malicious actor can delay withdrawals as long as they are willing to pay the cost of losing their stakes. If the protocol is delayed attacked, the new stake requirement increases exponentially for each challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled. of delay. Challenges are played via a bisection game, where asserter and challenger play together to find the first instruction of disagreement. Such instruction is then executed onchain in the WASM OneStepProver contract to determine the winner, who then gets half of the stake of the loser. As said before, a state root is rejected only when no one left is staked on it. The protocol does not enforces valid bisections, meaning that actors can propose correct initial claim and then provide incorrect midpoints.
Whitelisted validatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier can fast-confirm state-roots after the initial 15m minimum assertion period has passed on a state rootA cryptographic hash succinctly representing a state using a Merkle tree. and skip the 6d 8h challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled.. This finalizes the fast-confirmed state root an permits withdrawals based on it.
Funds can be stolen if validators with the 'fast-confirmer' permission finalize a malicious state root before the challenge period has passed (CRITICAL).
Program Hashes
Name | Hash | Repository | Verification | Used in | |||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
0xdb69...b69a |      Projects used inSearch for projects used in | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
Past upgrades
The metrics include upgrades on the currently used proxy contracts. Historical proxy contracts and changes of such are not included.
2025 December 15, 10:43 UTCHigh severity4changesEOA enabled calibur smart wallet. Project is archived.
EOA enabled calibur smart wallet. Project is archived.
| EOA (eth:0xB65540bBA534E88EB4a5062D0E6519C07063b259) { | |
| +++ description: None | |
| proxyType: | |
| - | "EOA" |
| + | "EIP7702 EOA" |
| template: | |
| + | "uniswap/calibur7702" |
| sourceHashes: | |
| + | ["0xb3eb47d8d57eba02013e5d347d05147f7ac072ef2e5e4e1f9a5c6fbced93f8b0"] |
| values: | |
| + | {"$implementation":"eth:0x000000009B1D0aF20D8C6d0A44e162d11F9b8f00","CUSTOM_STORAGE_ROOT":"0x3b86514c5c56b21f08d8e56ab090292e07c2483b3e667a2a45849dcb71368600","domainBytes":"0xc7e4f5b2d381bdfacf8506a24542052ab4e951573cab4ce34bb1c9509c84cbbf06c015bd22b4c69690933c1058878ebdfef31f9aaae40bbe86d8a09fe1b2972c0000000000000000000000000000000000000000000000000000000000000001000000000000000000000000b65540bba534e88eb4a5062d0e6519c07063b259000000000000000000000000000000009b1d0af20d8c6d0a44e162d11f9b8f00","domainSeparator":"0xae1ae59b43b99665a7d7de7c1ca92017a6e8c484587869daf07b2bd3a6aa0301","eip712Domain":{"fields":"0x1f","name":"Calibur","version":"1.0.0","chainId":1,"verifyingContract":"eth:0xB65540bBA534E88EB4a5062D0E6519C07063b259","salt":"0x000000000000000000000000000000009b1d0af20d8c6d0a44e162d11f9b8f00","extensions":[]},"ENTRY_POINT":"eth:0x4337084D9E255Ff0702461CF8895CE9E3b5Ff108","keyAt":[],"keyCount":0,"keyHashes":0,"namespaceAndVersion":"Uniswap.Calibur.1.0.0"} |
| } | |
2025 August 25, 14:05 UTC2changesUpgrade to ArbOS v40 wasmModuleRoot.
Upgrade to ArbOS v40 wasmModuleRoot.
| contract RollupProxy (0x1CA12290D954CFe022323b6A6Df92113ed6b1C98) { | |
| +++ description: Central contract for the project's configuration like its execution logic hash (`wasmModuleRoot`) and addresses of the other system contracts. Entry point for Proposers creating new Rollup Nodes (state commitments) and Challengers submitting fraud proofs (In the Orbit stack, these two roles are both held by the Validators). | |
| +++ description: ArbOS version derived from known wasmModuleRoots. | |
| values.arbOsFromWmRoot: | |
| - | "ArbOS v32 wasmModuleRoot" |
| + | "ArbOS v40 wasmModuleRoot" |
| +++ description: Root hash of the WASM module used for execution, like a fingerprint of the L2 logic. Can be associated with ArbOS versions. | |
| values.wasmModuleRoot: | |
| - | "0x184884e1eb9fefdc158f6c8ac912bb183bf3cf83f0090317e0bc4ac5860baa39" |
| + | "0xdb698a2576298f25448bc092e52cf13b1e24141c997135d70f217d674bbeb69a" |
| } | |
2025 July 15, 09:05 UTC3changesGelato MS: one signer removed, one changed.
Gelato MS: one signer removed, one changed.
| contract Gelato Multisig (0xBeA2Bc852a160B8547273660E22F4F08C2fa9Bbb) { | |
| +++ description: None | |
| values.$members.2: | |
| - | "eth:0xB0C2CBFfCd4C31AFFEe14993b6d48f99D285f621" |
| + | "eth:0x58edE8C66A15f23c61b8EadD1191FdaD904f7a87" |
| values.$members.8: | |
| - | "eth:0xf83bC4688979b13Da02CB94c76cEB169540760b5" |
| values.multisigThreshold: | |
| - | "4 of 10 (40%)" |
| + | "4 of 9 (44%)" |
| } | |
2025 July 14, 12:44 UTC19changesDiscovery rerun on the same block number with only config-related changes.
Discovery rerun on the same block number with only config-related changes.
New and verified contracts
| + | Status: CREATED |
| contract OneStepProverHostIo (0x0003A96B27ce73505b43ea1b71a5aB06bec568C4) | |
| +++ description: One of the modular contracts used for the last step of a fraud proof, which is simulated inside a WASM virtual machine. | |
| + | Status: CREATED |
| contract RollupProxy (0x1CA12290D954CFe022323b6A6Df92113ed6b1C98) | |
| +++ description: Central contract for the project's configuration like its execution logic hash (`wasmModuleRoot`) and addresses of the other system contracts. Entry point for Proposers creating new Rollup Nodes (state commitments) and Challengers submitting fraud proofs (In the Orbit stack, these two roles are both held by the Validators). | |
| + | Status: CREATED |
| contract OneStepProverMemory (0x1cD76B9C33b2e3b04D7B181399d492B3e49AD7fB) | |
| +++ description: One of the modular contracts used for the last step of a fraud proof, which is simulated inside a WASM virtual machine. | |
| + | Status: CREATED |
| contract ValidatorUtils (0x2b0E04Dc90e3fA58165CB41E2834B44A56E766aF) | |
| +++ description: This contract implements view only utilities for validators. | |
| + | Status: CREATED |
| contract OneStepProver0 (0x2dCCAbE89cF76132619a9B18e9F9e48E837222b5) | |
| +++ description: One of the modular contracts used for the last step of a fraud proof, which is simulated inside a WASM virtual machine. | |
| + | Status: CREATED |
| contract Bridge (0x41Ec9456AB918f2aBA81F38c03Eb0B93b78E84d9) | |
| +++ description: Escrow contract for the project's gas token (can be different from ETH). Keeps a list of allowed Inboxes and Outboxes for canonical bridge messaging. | |
| + | Status: CREATED |
| contract RollupEventInbox (0x4e008aEeA79Fcd5708A7b46CA1732dFAf2a25B7d) | |
| +++ description: Helper contract sending configuration data over the bridge during the systems initialization. | |
| + | Status: CREATED |
| contract Inbox (0x56D8EC76a421063e1907503aDd3794c395256AEb) | |
| +++ description: Facilitates sending L1 to L2 messages like depositing ETH, but does not escrow funds. | |
| + | Status: CREATED |
| contract Outbox (0x73bb50c32a3BD6A1032aa5cFeA048fBDA3D6aF6e) | |
| +++ description: Facilitates L2 to L1 contract calls: Messages initiated from L2 (for example withdrawal messages) eventually resolve in execution on L1. | |
| + | Status: CREATED |
| contract ProxyAdmin (0x80622fe04c5e1c3fbb3A9c62996dB27B53E9F77b) | |
| +++ description: None | |
| + | Status: CREATED |
| contract UpgradeExecutor (0x830D41c5624EE982cddEd92Ba01DAB3a4856116f) | |
| +++ description: Central contract defining the access control permissions for upgrading the system contract implementations. | |
| + | Status: CREATED |
| contract OneStepProofEntry (0x8Faa21891B0b928afEbd5314D1D313f8f7B34DaC) | |
| +++ description: One of the modular contracts used for the last step of a fraud proof, which is simulated inside a WASM virtual machine. | |
| + | Status: CREATED |
| contract ChallengeManager (0xb9e6987d1E0936b93f512bC89632E15DcA706d87) | |
| +++ description: Contract that allows challenging state roots. Can be called through the RollupProxy by Validators or the UpgradeExecutor. | |
| + | Status: CREATED |
| contract Gelato Multisig (0xBeA2Bc852a160B8547273660E22F4F08C2fa9Bbb) | |
| +++ description: None | |
| + | Status: CREATED |
| contract ERC20Gateway (0xccaF21F002EAF230c9Fa810B34837a3739B70F7B) | |
| +++ description: Escrows deposited ERC-20 assets for the canonical Bridge. Upon depositing, a generic token representation will be minted at the destination. Withdrawals are initiated by the Outbox contract. | |
| + | Status: CREATED |
| contract OneStepProverMath (0xCf4b98cFF2976E4eb579B9498f398b5bd279A6eD) | |
| +++ description: One of the modular contracts used for the last step of a fraud proof, which is simulated inside a WASM virtual machine. | |
| + | Status: CREATED |
| contract GatewayRouter (0xeBb17f398ed30d02F2e8733e7c1e5cf566e17812) | |
| +++ description: This routing contract maps tokens to the correct escrow (gateway) to be then bridged with canonical messaging. | |
| + | Status: CREATED |
| contract AlephZeroMultisig (0xeC475675629B38E42d4aC5d40761618268E7Ed21) | |
| +++ description: None | |
| + | Status: CREATED |
| contract SequencerInbox (0xF75206c49c1694594E3e69252E519434f1579876) | |
| +++ description: A sequencer (registered in this contract) can submit transaction batches or commitments here. | |
2025 March 25, 08:22 UTCHigh severity18changesMinor upgrade of Bridge, Inbox and SequencerInbox: - logic for tokens with custom decimals - 7702 adjustments - SequencerInbox upgraded to known implementation
Minor upgrade of Bridge, Inbox and SequencerInbox:
- logic for tokens with custom decimals
- 7702 adjustments
- SequencerInbox upgraded to known implementation
| contract Bridge (0x41Ec9456AB918f2aBA81F38c03Eb0B93b78E84d9) { | |
| +++ description: Escrow contract for the project's gas token (can be different from ETH). Keeps a list of allowed Inboxes and Outboxes for canonical bridge messaging. | |
| sourceHashes.1: | |
| - | "0x057de68a7007d55f4394ba6eafb2c802efcaf13583ff9342ea4d0ee3924d9be1" |
| + | "0xa7e3f6c355703ed46fcb2156862c4f01792b87beb10a87a81ce3bd5beee79b67" |
| sourceHashes.0: | |
| - | "0xa7e3f6c355703ed46fcb2156862c4f01792b87beb10a87a81ce3bd5beee79b67" |
| + | "0x32c73666d391a33c17183e4ab20bcb0f2b925d8a99da436d2ff99c13f403e289" |
| values.$implementation: | |
| - | "0x7EfcB76D0e2E776A298aAa603d433336e5F8b6ab" |
| + | "0xEfA1De858293593732a09c9dAA238BEC49595751" |
| values.$pastUpgrades.1: | |
| + | ["2025-03-24T11:51:11.000Z","0x5837fef008eaaa8871086f7e53f38a95b768926562e2e82cae17ddc7ab61b070",["0xEfA1De858293593732a09c9dAA238BEC49595751"]] |
| values.$upgradeCount: | |
| - | 1 |
| + | 2 |
| values.nativeTokenDecimals: | |
| + | 18 |
| } | |
| contract Inbox (0x56D8EC76a421063e1907503aDd3794c395256AEb) { | |
| +++ description: Facilitates sending L1 to L2 messages like depositing ETH, but does not escrow funds. | |
| sourceHashes.0: | |
| - | "0xcb390b491549387c8fcc09fb22fbea7adf54cc74b7247a0c738369ddd7049b92" |
| + | "0x25984fdfffb8141859c99299fb29e7a7460732d77111e5fe23792baa99f336a3" |
| values.$implementation: | |
| - | "0x31fAAAB44e74eB408d1FC69A14806B4b9cA09da2" |
| + | "0x6C051397fee2d79ccf92d1f3c5c6547fEBD838F4" |
| values.$pastUpgrades.1: | |
| + | ["2024-07-29T13:18:23.000Z","0x16528bf78b7d2110129529a7a0435a35b5443e3638f89fb2f917a7c92ef587b9",["0x31fAAAB44e74eB408d1FC69A14806B4b9cA09da2"]] |
| values.$pastUpgrades.0.2: | |
| - | "2024-07-29T13:18:23.000Z" |
| + | ["0x6C051397fee2d79ccf92d1f3c5c6547fEBD838F4"] |
| values.$pastUpgrades.0.1: | |
| - | ["0x31fAAAB44e74eB408d1FC69A14806B4b9cA09da2"] |
| + | "2025-03-24T16:55:11.000Z" |
| values.$pastUpgrades.0.0: | |
| - | "0x16528bf78b7d2110129529a7a0435a35b5443e3638f89fb2f917a7c92ef587b9" |
| + | "0x2ecdabc185a5e5350c23c45cfbf746bd874b272e363729adcf975533d38790b8" |
| values.$upgradeCount: | |
| - | 1 |
| + | 2 |
| } | |
| contract SequencerInbox (0xF75206c49c1694594E3e69252E519434f1579876) { | |
| +++ description: A sequencer (registered in this contract) can submit transaction batches or commitments here. | |
| sourceHashes.0: | |
| - | "0x50cf57b01499408fa99da27cf0fee96ec30f0d40667d1aa090c442bc80f0636b" |
| + | "0x6bb86ac4bd0d31e049f543fcf0a8f94c952252222f115246ef9d5b8104d803cc" |
| values.$implementation: | |
| - | "0x383f16fB2809a56fC639c1eE2c93Ad2aa7Ee130A" |
| + | "0xaEd84B70Be8117112a5aa0d93a7fBff463A03b18" |
| values.$pastUpgrades.1: | |
| + | ["2025-03-24T16:55:11.000Z","0x2ecdabc185a5e5350c23c45cfbf746bd874b272e363729adcf975533d38790b8",["0xaEd84B70Be8117112a5aa0d93a7fBff463A03b18"]] |
| values.$upgradeCount: | |
| - | 1 |
| + | 2 |
| values.reader4844: | |
| - | "0x7Deda2425eC2d4EA0DF689A78de2fBF002075576" |
| + | "0x6c5c9E6c080a6C25f49DfFE85cfA71aaEAAfdE74" |
| } | |
The system has a centralized sequencer
While forcing transaction is open to anyone the system employs a privileged sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. that has priority for submitting transaction batches and ordering transactions.
MEV can be extracted if the operator exploits their centralized position and frontruns user transactions.
Users can force any transaction
Because the state of the system is based on transactions submitted on the underlying host chain and anyone can submit their transactions there it allows the users to circumvent censorship by interacting with the smart contract on the host chain directly. After a delay of 4d in which a SequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. has failed to include a transaction that was directly posted to the smart contract, it can be forcefully included by anyone on the host chain, which finalizes its ordering.
Delayed forced transactions
To force transactions from the host chain, users must first enqueue “delayed” messages in the “delayed” inbox of the BridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. contract. Only authorized Inboxes are allowed to enqueue delayed messages, and the so-called Inbox contract is the one used as the entry point by calling the sendMessage or sendMessageFromOrigin functions. If the centralized sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. doesn’t process the request within some time bound, users can call the forceInclusion function on the SequencerInbox contract to include the message in the canonical chain. The time bound is hardcoded to be 4d.
Regular messaging
The user initiates L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups.->L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. messages by submitting a regular transaction on this chain. When the blockAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over. containing that transaction is settled, the message becomes available for processing on L1. The process of block finalization usually takes several days to complete.
Autonomous exit
Users can (eventually) exit the system by pushing the transaction on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. and providing the corresponding state rootA cryptographic hash succinctly representing a state using a Merkle tree.. The only way to prevent such withdrawal is via an upgrade.
EVM compatible smart contracts are supported
Arbitrum One uses Nitro technology that allows running fraud proofs by executing EVM code on top of WASM.
Ethereum
Actors:
A Multisig with 4/9 threshold.
- Can upgrade with no delay
- RollupProxy UpgradeExecutor
- BridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. UpgradeExecutor → ProxyAdmin
- RollupEventInbox UpgradeExecutor → ProxyAdmin
- Inbox UpgradeExecutor → ProxyAdmin
- Outbox UpgradeExecutor → ProxyAdmin
- UpgradeExecutor UpgradeExecutor → ProxyAdmin
- ChallengeManager UpgradeExecutor → ProxyAdmin
- ERC20Gateway UpgradeExecutor → ProxyAdmin
- GatewayRouter UpgradeExecutor → ProxyAdmin
- SequencerInbox UpgradeExecutor → ProxyAdmin
- Can interact with RollupProxy
- Pause and unpause and set important roles and parameters in the system contracts: Can delegate SequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. management to a BatchPosterManager address, manage data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium., DACs and the fastConfirmer role, set the Sequencer-only window, introduce an allowList to the bridge and whitelist Inboxes/Outboxes UpgradeExecutor
Participants (9):
0x349f…Adb90xB655…b2590x58ed…7a870x28bB…680c0x691C…aAD20x5bE3…A54d0x88De…fD520x01a0…c32e0x547D…1a26Member of AlephZeroMultisig.
- Can interact with RollupProxy
- Can finalize a state rootA cryptographic hash succinctly representing a state using a Merkle tree. before the challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled. has passed. This allows withdrawing from the bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. based on the state root AlephZeroMultisig
- Can propose new state roots (called nodes) and challenge state roots on the host chain AlephZeroMultisig - or - acting directly
- Can interact with RollupProxy
- Can propose new state rootsA cryptographic hash succinctly representing a state using a Merkle tree. (called nodes) and challenge state roots on the host chain
Ethereum
Central contract for the project’s configuration like its execution logic hashA fixed-length fingerprint of variable-size input, produced by a hash function. (wasmModuleRoot) and addresses of the other system contracts. Entry point for Proposers creating new RollupA blockchain that inherits consensus and data availability from another blockchain called L1. Rollups enable trust minimized bridges with the base layer via proof systems, either optimistic or zero-knowledge. A rollup without a bridge, or without considering the bridge, is called a sovereign rollup. Nodes (state commitments) and Challengers submitting fraud proofs (In the Orbit stack, these two roles are both held by the ValidatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier).
- Roles:
- admin: UpgradeExecutor; ultimately Gelato Multisig
- anyTrustFastConfirmer: AlephZeroMultisig; ultimately EOA 1
- owner: UpgradeExecutor; ultimately Gelato Multisig
- validators: AlephZeroMultisig, EOA 1, EOA 3, EOA 4, EOA 5, EOA 9; ultimately EOA 1
Escrow contract for the project’s gasA virtual fuel used to execute smart contracts on a rollup. The EVM (or other VM within the rollup) uses an accounting mechanism to correspond the consumption of gas to the consumption of computing resources, and to limit the consumption of computing resources. token (can be different from ETH). Keeps a list of allowed Inboxes and Outboxes for canonical bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. messaging.
- Roles:
- admin: ProxyAdmin; ultimately Gelato Multisig

Contract that allows challenging state rootsA cryptographic hash succinctly representing a state using a Merkle tree.. Can be called through the RollupProxy by ValidatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier or the UpgradeExecutor.
- Roles:
- admin: ProxyAdmin; ultimately Gelato Multisig
A sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. (registered in this contract) can submit transaction batches or commitments here.
- Roles:
- admin: ProxyAdmin; ultimately Gelato Multisig
- batchPosters: EOA 10, EOA 2, EOA 6, EOA 7, EOA 8
Central contract defining the access control permissions for upgrading the system contract implementations.
- Roles:
- admin: ProxyAdmin; ultimately Gelato Multisig
- executors: Gelato Multisig
Facilitates sending L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. to L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. messages like depositing ETH, but does not escrow funds.
- Roles:
- admin: ProxyAdmin; ultimately Gelato Multisig
Facilitates L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. to L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. contract calls: Messages initiated from L2 (for example withdrawal messages) eventually resolve in execution on L1.
- Roles:
- admin: ProxyAdmin; ultimately Gelato Multisig
Escrows deposited ERC-20 assets for the canonical BridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge.. Upon depositing, a generic token representation will be minted at the destination. Withdrawals are initiated by the Outbox contract.
- Roles:
- admin: ProxyAdmin; ultimately Gelato Multisig
All supported tokens in this escrow are included in the value secured calculation.
This routing contract maps tokens to the correct escrow (gateway) to be then bridged with canonical messaging.
- Roles:
- admin: ProxyAdmin; ultimately Gelato Multisig
One of the modular contracts used for the last step of a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system., which is simulated inside a WASM virtual machine.
One of the modular contracts used for the last step of a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system., which is simulated inside a WASM virtual machine.
This contract implements view only utilities for validatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier.
One of the modular contracts used for the last step of a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system., which is simulated inside a WASM virtual machine.
Helper contract sending configuration data over the bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. during the systems initialization.
- Roles:
- admin: ProxyAdmin; ultimately Gelato Multisig
- Roles:
- owner: UpgradeExecutor
One of the modular contracts used for the last step of a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system., which is simulated inside a WASM virtual machine.
One of the modular contracts used for the last step of a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system., which is simulated inside a WASM virtual machine.
The current deployment carries some associated risks:
Funds can be stolen if a contract receives a malicious code upgrade. There is no delay on code upgrades (CRITICAL).
Program Hashes
Name | Hash | Repository | Verification | Used in | |||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
0xdb69...b69a | Projects used inSearch for projects used in | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
Aleph Zero EVM