Search
Search for projects by name or address
 WINR
Critical contracts can be upgraded by an EOA which could result in the loss of all funds.
Badges
About
WINR is a Layer 3 on Arbitrum, based on the Orbit stack. It is focused on building a decentralized iGaming infrastructure.
Badges
About
WINR is a Layer 3 on Arbitrum, based on the Orbit stack. It is focused on building a decentralized iGaming infrastructure.
Why is the project listed in others?
Consequence: projects without a sufficiently decentralized set of challengers rely on few entities to safely update the state. A small set of challengers can collude with the proposer to finalize an invalid state, which can cause loss of funds.
Consequence: projects without a sufficiently decentralized data availability committee rely on few entities to safely attest data availability on Ethereum. A small set of entities can collude with the proposer to finalize an unavailable state, which can cause loss of funds.
Learn more about the recategorisation here.
This section shows how much data the project publishes to its data-availability (DA) layer over time. The project currently posts data to Celestia.
WINR stops using Celestia
2025 Nov 18th
WINR stops using Celestia and switches to ArbOS v32 with a DAC for data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium..
WINR starts using Blobstream
2025 May 12th
Upgraded ChallengeManager contract to the version that uses Celestia with Blobstream bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge.
 Arbitrum One
Funds can be stolen if
- a contract receives a malicious code upgrade. There is no delay on code upgrades (CRITICAL),
- none of the whitelisted verifiers checks the published state. Fraud proofs assume at least one honest and able validator (CRITICAL),
- validators with the 'fast-confirmer' permission finalize a malicious state root before the challenge period has passed (CRITICAL).
Funds can be lost if
Users can be censored if
MEV can be extracted if
| SEQUENCER FAILURE | STATE VALIDATION | DATA AVAILABILITY | EXIT WINDOW | PROPOSER FAILURE | |
| Arbitrum One L2 | Self sequence | Fraud proofs (INT) | Onchain | None | Self propose |
| WINR L3 • Individual | Self sequence | Fraud proofs (INT) | External (DAC) | None | Self propose |
| WINR L3 • Combined | Self sequence | Fraud proofs (INT) | External (DAC) | None | Self propose |
In the event of a sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. failure, users can force transactions to be included in the project’s chain by sending them to L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development.. There can be up to a 2d delay on this operation.
Fraud proofs allow 15 WHITELISTED actors watching the chain to prove that the state is incorrect. There are fewer than 5 Challengers external to the OperatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades. among these. Interactive proofs (INT) require multiple transactions over time to resolve. There is a 1h challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled..
Proof construction relies fully on data that is NOT published onchain. There exists a Data Availability Committee (DAC)A set of members whose task is attesting and ensuring that the data is available for the public. An onchain DAC verifier checks that a threshold of signatures from the DAC members is reached before considering a data commitment as available and therefore valid to be used in the system. with a threshold of 1/1 that is tasked with protecting and supplying the data.
There is no window for users to exit in case of an unwanted upgrade since contracts are instantly upgradable.
Anyone can become a ProposerIn the context of L2s, the actor that proposes a claimed state root on L1. The term is also used in the context of Ethereum to refer to the actor that proposes a new block. after 6d 9h of inactivity from the currently whitelisted Proposers.
Data is not stored on chain
Users transactions are not published onchain, but rather sent to external trusted parties, also known as committee members (DAC). Members of the DAC collectively produce a Data AvailabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium. Certificate (comprising BLS signatures from a quorum) guaranteeing that the data behind the new transaction batch will be available until the expiry period elapses (currently a minimum of two weeks). This signature is not verified by L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development., however external ValidatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier will skip the batch if BLS signature is not valid resulting. This will result in a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system. challenge if this batch is included in a consecutive state updateA mechanism that allows to update the claimed state of a project. It usually involves verifying a state transition proof, but it can also be done in a trusted manner by a permissioned actor.. It is assumed that at least one honest DAC member that signed the batch will reveal tx data to the Validators if SequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. decides to act maliciously and withhold the data. If the Sequencer cannot gather enough signatures from the DAC, it will “fall back to rollupA blockchain that inherits consensus and data availability from another blockchain called L1. Rollups enable trust minimized bridges with the base layer via proof systems, either optimistic or zero-knowledge. A rollup without a bridge, or without considering the bridge, is called a sovereign rollup.” mode and by posting the full data directly to the L1 chain. The current DAC threshold is 1 out of 1.
Funds can be lost if the external data becomes unavailable (CRITICAL).
Users can be censored if the committee restricts their access to the external data.
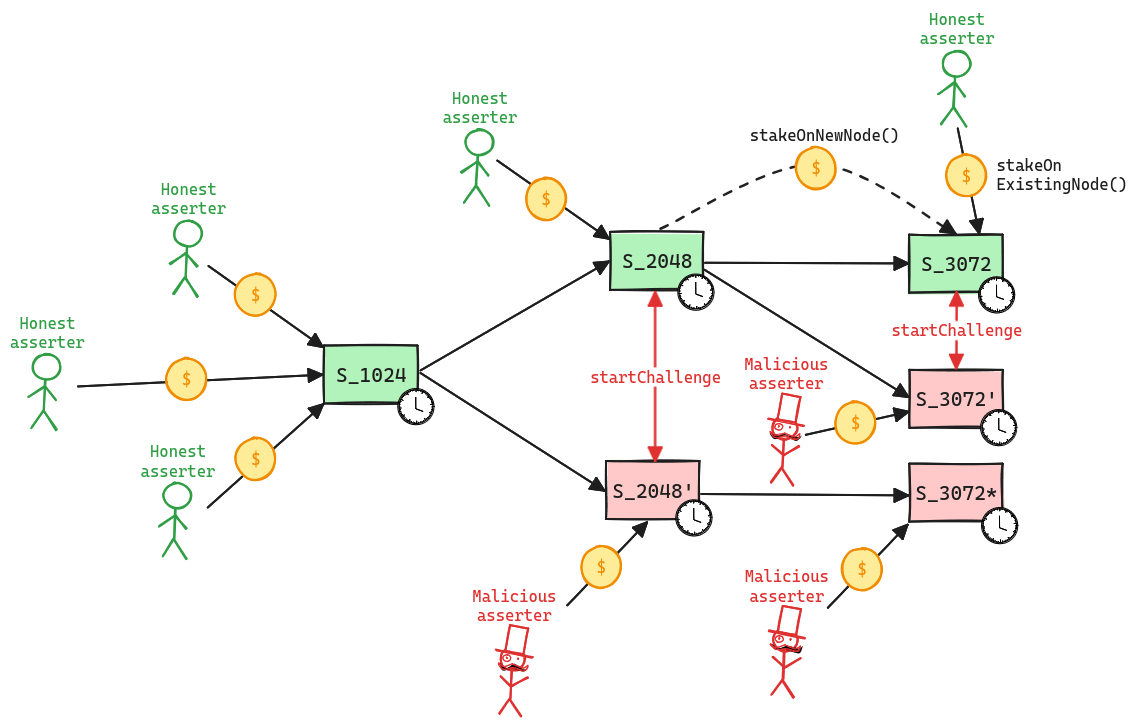
Updates to the system state can be proposed and challenged by a set of whitelisted validatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier. If a state rootA cryptographic hash succinctly representing a state using a Merkle tree. passes the challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled., it is optimistically considered correct and made actionable for withdrawals.
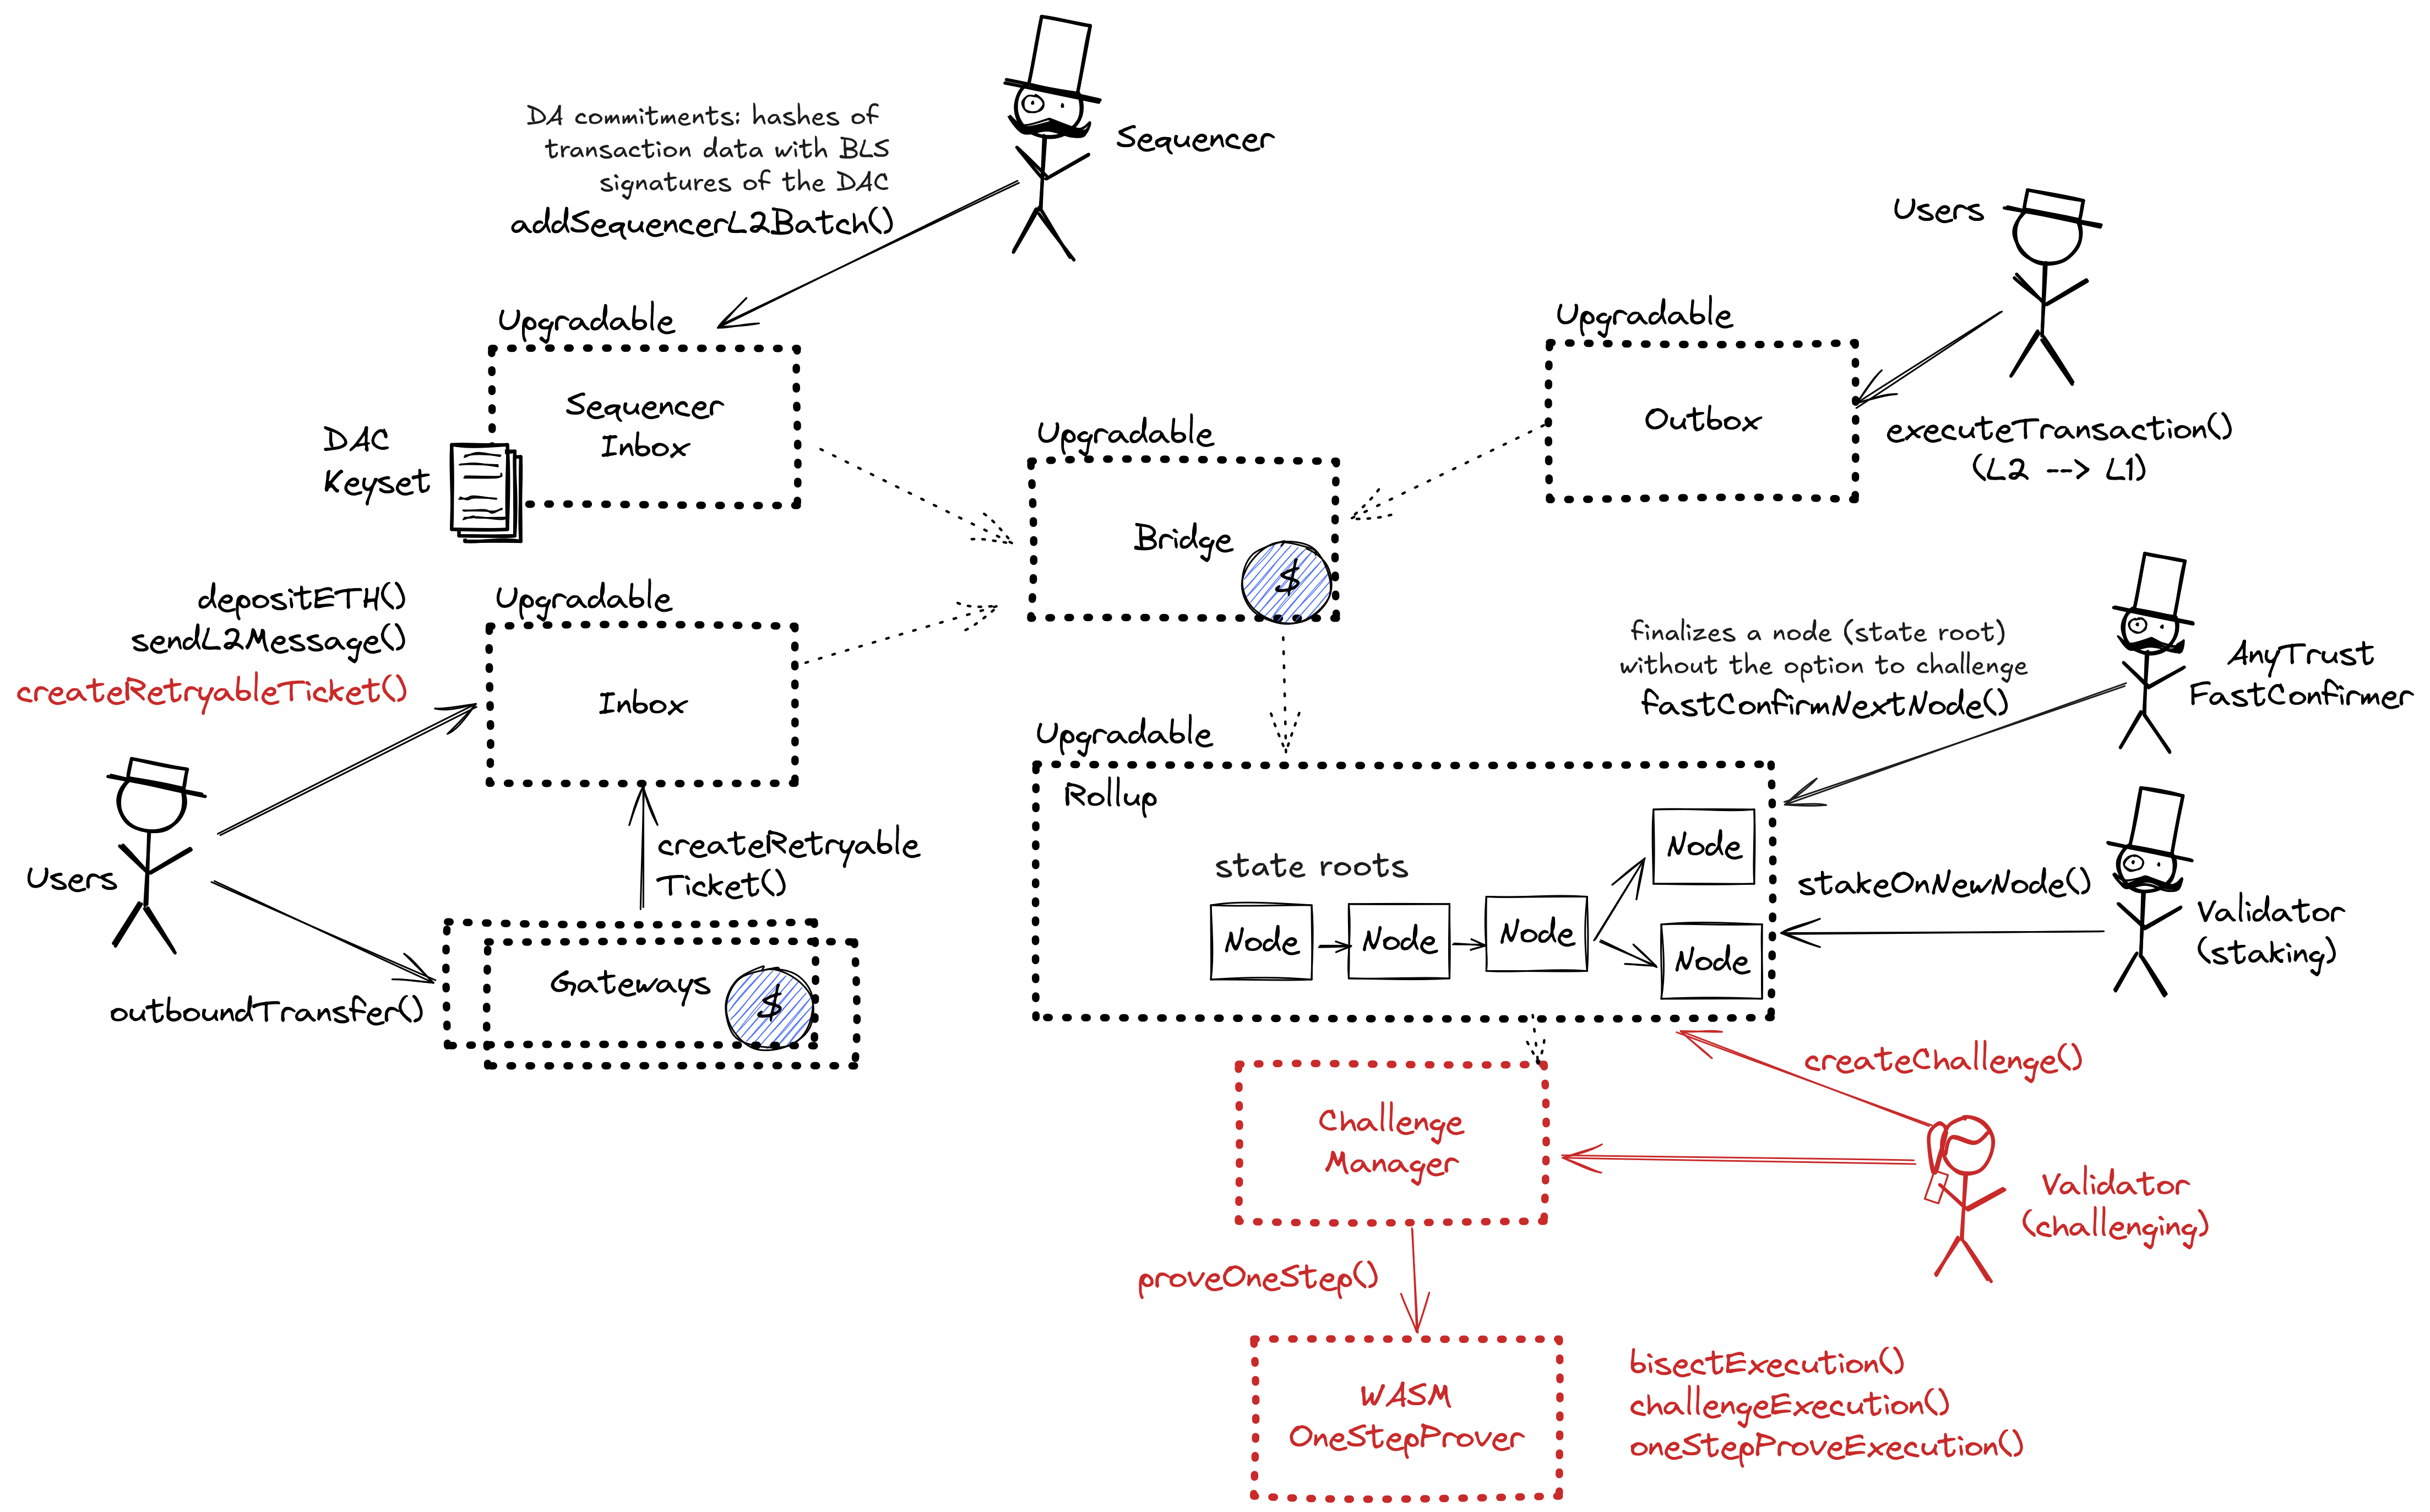
Whitelisted validatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier propose state rootsA cryptographic hash succinctly representing a state using a Merkle tree. as children of a previous state root. A state root can have multiple conflicting children. This structure forms a graph, and therefore, in the contracts, state roots are referred to as nodes. Each proposal requires a stake, currently set to 0.1 ETH, that can be slashed if the proposal is proven incorrect via a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system.. Stakes can be moved from one nodeA software client that participates in the network. to one of its children, either by calling stakeOnExistingNode or stakeOnNewNode. New nodes cannot be created faster than the minimum assertion period by the same validator, currently set to 12s. The oldest unconfirmed node can be confirmed if the challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled. has passed and there are no siblings, and rejected if the parent is not a confirmed node or if the challenge period has passed and no one is staked on it.
Funds can be stolen if none of the whitelisted verifiers checks the published state. Fraud proofs assume at least one honest and able validator (CRITICAL).
A challenge can be started between two siblings, i.e. two different state rootsA cryptographic hash succinctly representing a state using a Merkle tree. that share the same parent, by calling the startChallenge function. ValidatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier cannot be in more than one challenge at the same time, meaning that the protocol operates with partial concurrency. Since each challenge lasts 1h, this implies that the protocol can be subject to delay attacks, where a malicious actor can delay withdrawals as long as they are willing to pay the cost of losing their stakes. If the protocol is delayed attacked, the new stake requirement increases exponentially for each challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled. of delay. Challenges are played via a bisection game, where asserter and challenger play together to find the first instruction of disagreement. Such instruction is then executed onchain in the WASM OneStepProver contract to determine the winner, who then gets half of the stake of the loser. As said before, a state root is rejected only when no one left is staked on it. The protocol does not enforces valid bisections, meaning that actors can propose correct initial claim and then provide incorrect midpoints.
Whitelisted validatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier can fast-confirm state-roots after the initial 12s minimum assertion period has passed on a state rootA cryptographic hash succinctly representing a state using a Merkle tree. and skip the 1h challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled.. This finalizes the fast-confirmed state root an permits withdrawals based on it.
Funds can be stolen if validators with the 'fast-confirmer' permission finalize a malicious state root before the challenge period has passed (CRITICAL).
Program Hashes
Name | Hash | Repository | Verification | Used in | |||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
0xdb69...b69a |      Projects used inSearch for projects used in | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
Past upgrades
The metrics include upgrades on the currently used proxy contracts. Historical proxy contracts and changes of such are not included.
2026 January 21, 08:42 UTC6changesNew member conduit msig2.
New member conduit msig2.
| contract Conduit Multisig 2 (arb1:0x79C2abE3eBA9dc119318FdAaA48118e1CDB53F56) { | |
| +++ description: None | |
| values.$members.0: | |
| + | "arb1:0x381624F7912BddD83dc67c6C53Ef6FE61B87Cf07" |
| values.$members.1: | |
| + | "arb1:0x6BB4249858Ee19b6ABC071AD26bEe690baa783A6" |
| values.$members.5: | |
| - | "arb1:0xa4000bDD2bB92ce6750b31F1eeda47Bd1cB8e6e4" |
| values.multisigThreshold: | |
| - | "4 of 10 (40%)" |
| + | "4 of 11 (36%)" |
| } | |
| contract UpgradeExecutor (arb1:0xc5d17f6e0025a23c0AAFf7832Cc531B3034602DA) { | |
| +++ description: Central contract defining the access control permissions for upgrading the system contract implementations. | |
| values.accessControl.EXECUTOR_ROLE.members.1: | |
| + | "arb1:0x487fb70F28cEb4f320f2D72ed859cEEdC1B8C648" |
| values.executors.1: | |
| + | "arb1:0x487fb70F28cEb4f320f2D72ed859cEEdC1B8C648" |
| } | |
2026 January 09, 15:11 UTC1changestakerCount decreased from 1 to 0, no active validators on the chain.
stakerCount decreased from 1 to 0, no active validators on the chain.
| contract RollupProxy (arb1:0x2633ea91d15BeE85105C9b27E068f406F2F36a4a) { | |
| +++ description: Central contract for the project's configuration like its execution logic hash (`wasmModuleRoot`) and addresses of the other system contracts. Entry point for Proposers creating new Rollup Nodes (state commitments) and Challengers submitting fraud proofs (In the Orbit stack, these two roles are both held by the Validators). | |
| values.stakerCount: | |
| - | 1 |
| + | 0 |
| } | |
2025 December 10, 15:16 UTC3changesConduit multisig added member.
Conduit multisig added member.
| contract Conduit Multisig 2 (arb1:0x79C2abE3eBA9dc119318FdAaA48118e1CDB53F56) { | |
| +++ description: None | |
| values.$members.0: | |
| + | "arb1:0x2103c69696CB2D3779f5445393808239034E911c" |
| values.$members.0: | |
| - | "arb1:0xFe0ab87ebE03DD0bF52DaF34Dfda6639c335e2d4" |
| + | "arb1:0x65D1d44B8B2fE15d45A03708E0835C7E98a56007" |
| values.$members.3: | |
| - | "arb1:0xF0B77EaE7F2dabCC2571c7418406A0dCA3afA4f0" |
| } | |
2025 November 19, 12:25 UTC3changesNo more a Celestia L2.
No more a Celestia L2.
| contract RollupProxy (arb1:0x2633ea91d15BeE85105C9b27E068f406F2F36a4a) { | |
| +++ description: Central contract for the project's configuration like its execution logic hash (`wasmModuleRoot`) and addresses of the other system contracts. Entry point for Proposers creating new Rollup Nodes (state commitments) and Challengers submitting fraud proofs (In the Orbit stack, these two roles are both held by the Validators). | |
| +++ description: ArbOS version derived from known wasmModuleRoots. | |
| values.arbOsFromWmRoot: | |
| - | "Celestia Nitro ArbOS v40 wasmModuleRoot" |
| + | "ArbOS v40 wasmModuleRoot" |
| +++ description: Root hash of the WASM module used for execution, like a fingerprint of the L2 logic. Can be associated with ArbOS versions. | |
| values.wasmModuleRoot: | |
| - | "0x597de35fc2ee60e5b2840157370d037542d6a4bc587af7f88202636c54e6bd8d" |
| + | "0xdb698a2576298f25448bc092e52cf13b1e24141c997135d70f217d674bbeb69a" |
| } | |
| contract SequencerInbox (arb1:0x8AeDdE55Cb361e73a0B0c0cF2A5bB35E97a20456) { | |
| +++ description: A sequencer (registered in this contract) can submit transaction batches or commitments here. | |
| values.sequencerVersion: | |
| - | "0x63" |
| + | "0x88" |
| } | |
2025 October 03, 08:48 UTC2changesMember removed from multisig.
Member removed from multisig.
| contract Conduit Multisig 2 (arb1:0x79C2abE3eBA9dc119318FdAaA48118e1CDB53F56) { | |
| +++ description: None | |
| values.$members.2: | |
| - | "arb1:0x50930d652266EF4127FA3A1906B7Cb9951076628" |
| values.multisigThreshold: | |
| - | "4 of 11 (36%)" |
| + | "4 of 10 (40%)" |
| } | |
Arbitrum OneThe system has a centralized sequencer
While forcing transaction is open to anyone the system employs a privileged sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. that has priority for submitting transaction batches and ordering transactions.
MEV can be extracted if the operator exploits their centralized position and frontruns user transactions.
Users can force any transaction
Because the state of the system is based on transactions submitted on the underlying host chain and anyone can submit their transactions there it allows the users to circumvent censorship by interacting with the smart contract on the host chain directly. After a delay of 1d in which a SequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. has failed to include a transaction that was directly posted to the smart contract, it can be forcefully included by anyone on the host chain, which finalizes its ordering.
Delayed forced transactions
To force transactions from the host chain, users must first enqueue “delayed” messages in the “delayed” inbox of the BridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. contract. Only authorized Inboxes are allowed to enqueue delayed messages, and the so-called Inbox contract is the one used as the entry point by calling the sendMessage or sendMessageFromOrigin functions. If the centralized sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. doesn’t process the request within some time bound, users can call the forceInclusion function on the SequencerInbox contract to include the message in the canonical chain. The time bound is hardcoded to be 1d.
Arbitrum OneRegular messaging
The user initiates L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups.->L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. messages by submitting a regular transaction on this chain. When the blockAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over. containing that transaction is settled, the message becomes available for processing on L1. The process of block finalization usually takes several days to complete.
Autonomous exit
Users can (eventually) exit the system by pushing the transaction on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. and providing the corresponding state rootA cryptographic hash succinctly representing a state using a Merkle tree.. The only way to prevent such withdrawal is via an upgrade.
EVM compatible smart contracts are supported
Arbitrum One uses Nitro technology that allows running fraud proofs by executing EVM code on top of WASM.
Arbitrum One
Actors:
A Multisig with 4/11 threshold.
- Can upgrade with no delay
- ChallengeManager UpgradeExecutor → ProxyAdmin
- RollupProxy UpgradeExecutor
- Inbox UpgradeExecutor → ProxyAdmin
- SequencerInbox UpgradeExecutor → ProxyAdmin
- Outbox UpgradeExecutor → ProxyAdmin
- UpgradeExecutor UpgradeExecutor → ProxyAdmin
- RollupEventInbox UpgradeExecutor → ProxyAdmin
- BridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. UpgradeExecutor → ProxyAdmin
- Can interact with RollupProxy
- Pause and unpause and set important roles and parameters in the system contracts: Can delegate SequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. management to a BatchPosterManager address, manage data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium., DACs and the fastConfirmer role, set the Sequencer-only window, introduce an allowList to the bridge and whitelist Inboxes/Outboxes UpgradeExecutor
Participants (11):
0x3816…Cf070x6BB4…83A60x2103…911c0x65D1…60070x8117…E7Ac0xA073…bda20xF331…647D0x4D80…5BAe0x3840…Fd5f0xa0C6…90380xefCf…dD5CA Multisig with 4/6 threshold.
- Can upgrade with no delay
- ArbitrumBlobstream
- Can interact with ArbitrumBlobstream
- can freeze the bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. contract and update the list of authorized relayers
A Multisig with 2/3 threshold.
- Can interact with SP1VerifierGatewayArb
- affect the livenessLiveness refers to the ability of a system to respond to requests and to process them in a timely manner. In the context of L2s, it refers to the ability of settling transactions, proofs and state roots to the base layer. and safety of the gateway - can transfer ownership, add and freeze verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. routes
- Can upgrade with no delay
- ChallengeManager UpgradeExecutor → ProxyAdmin
- RollupProxy UpgradeExecutor
- Inbox UpgradeExecutor → ProxyAdmin
- SequencerInbox UpgradeExecutor → ProxyAdmin
- Outbox UpgradeExecutor → ProxyAdmin
- UpgradeExecutor UpgradeExecutor → ProxyAdmin
- RollupEventInbox UpgradeExecutor → ProxyAdmin
- BridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. UpgradeExecutor → ProxyAdmin
- Can interact with RollupProxy
- Pause and unpause and set important roles and parameters in the system contracts: Can delegate SequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. management to a BatchPosterManager address, manage data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium., DACs and the fastConfirmer role, set the Sequencer-only window, introduce an allowList to the bridge and whitelist Inboxes/Outboxes UpgradeExecutor
Member of WinrFastconfirmerMultisig.
- Can interact with RollupProxy
- Can finalize a state rootA cryptographic hash succinctly representing a state using a Merkle tree. before the challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled. has passed. This allows withdrawing from the bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. based on the state root WinrFastconfirmerMultisig
- Can propose new state roots (called nodes) and challenge state roots on the host chain WinrFastconfirmerMultisig - or - acting directly
- Can interact with ArbitrumBlobstream
- it is a ‘Relayer’ and can call commitHeaderRange() to commit blockAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over. ranges. Since adding and removing Relayers emits no events, there can be more relayers than are presented here
Arbitrum One
Contract that allows challenging state rootsA cryptographic hash succinctly representing a state using a Merkle tree.. Can be called through the RollupProxy by ValidatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier or the UpgradeExecutor.
- Roles:
- admin: ProxyAdmin; ultimately Conduit Multisig 2, EOA 1
Central contract for the project’s configuration like its execution logic hashA fixed-length fingerprint of variable-size input, produced by a hash function. (wasmModuleRoot) and addresses of the other system contracts. Entry point for Proposers creating new RollupA blockchain that inherits consensus and data availability from another blockchain called L1. Rollups enable trust minimized bridges with the base layer via proof systems, either optimistic or zero-knowledge. A rollup without a bridge, or without considering the bridge, is called a sovereign rollup. Nodes (state commitments) and Challengers submitting fraud proofs (In the Orbit stack, these two roles are both held by the ValidatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier).
- Roles:
- admin: UpgradeExecutor; ultimately Conduit Multisig 2, EOA 1
- anyTrustFastConfirmer: WinrFastconfirmerMultisig; ultimately EOA 2
- owner: UpgradeExecutor; ultimately Conduit Multisig 2, EOA 1
- validators: EOA 11, EOA 13, EOA 15, EOA 18, EOA 2, EOA 20, EOA 23, EOA 25, EOA 27, EOA 28, EOA 29, EOA 3, EOA 4, EOA 5, WinrFastconfirmerMultisig; ultimately EOA 2
A sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. (registered in this contract) can submit transaction batches or commitments here.
- Roles:
- admin: ProxyAdmin; ultimately Conduit Multisig 2, EOA 1
- batchPosters: EOA 10, EOA 12, EOA 14, EOA 16, EOA 17, EOA 19, EOA 21, EOA 22, EOA 24, EOA 26, EOA 6, EOA 7, EOA 8, EOA 9
Escrow contract for the project’s gasA virtual fuel used to execute smart contracts on a rollup. The EVM (or other VM within the rollup) uses an accounting mechanism to correspond the consumption of gas to the consumption of computing resources, and to limit the consumption of computing resources. token (can be different from ETH). Keeps a list of allowed Inboxes and Outboxes for canonical bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. messaging.
- Roles:
- admin: ProxyAdmin; ultimately Conduit Multisig 2, EOA 1
Central contract defining the access control permissions for upgrading the system contract implementations.
- Roles:
- admin: ProxyAdmin; ultimately Conduit Multisig 2, EOA 1
- executors: Conduit Multisig 2, EOA 1
Facilitates sending L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. to L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. messages like depositing ETH, but does not escrow funds.
- Roles:
- admin: ProxyAdmin; ultimately Conduit Multisig 2, EOA 1
Facilitates L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. to L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. contract calls: Messages initiated from L2 (for example withdrawal messages) eventually resolve in execution on L1.
- Roles:
- admin: ProxyAdmin; ultimately Conduit Multisig 2, EOA 1
One of the modular contracts used for the last step of a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system., which is simulated inside a WASM virtual machine.
One of the modular contracts used for the last step of a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system., which is simulated inside a WASM virtual machine.
This contract implements view only utilities for validatorsIn the context of L2s, a Validator is an actor that validates the correctness of state transitions. For optimistic rollups this corresponds to challengers, and for ZK rollups this corresponds to the onchain verifier.
One of the modular contracts used for the last step of a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system., which is simulated inside a WASM virtual machine. This version uses the Blobstream DA bridgeSystem that verifies that data has been made available. It takes the form of a smart contract verifying a consensus or, if the data is verified directly by either downloading the full data or sampling, of an enshrined bridge. (ArbitrumBlobstream) as source of truth for the DA referenced by the fault proof.
One of the modular contracts used for the last step of a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system., which is simulated inside a WASM virtual machine.
- Roles:
- owner: UpgradeExecutor
Helper contract sending configuration data over the bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. during the systems initialization.
- Roles:
- admin: ProxyAdmin; ultimately Conduit Multisig 2, EOA 1
One of the modular contracts used for the last step of a fraud proofAlso referred to as a fault proof, it is the construction of an assertion that fraud was perpetrated on an optimistic rollup. More concretely, that an invalid state transition took place according to the protocol rules. The submitter of a fraud proof would expect a reward from the optimistic rollup protocol for helping maintain the integrity of the system., which is simulated inside a WASM virtual machine.
The Blobstream DA bridgeSystem that verifies that data has been made available. It takes the form of a smart contract verifying a consensus or, if the data is verified directly by either downloading the full data or sampling, of an enshrined bridge.. This contract is used to bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. data commitments between Celestia and the destination chain. It specifies relayers that commit blockAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over. ranges, but due to the lack of emitted events, there may be more relayers than are presented here.
- Roles:
- admin: BlobstreamMultisig
- guardians: BlobstreamMultisig
- relayers: EOA 30, EOA 31
VerifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. contract for SP1 proofs (v5.0.0).
This contract is the router for zk proof verification. It stores the mapping between identifiers and the address of onchain verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. contracts, routing each identifier to the corresponding verifier contract.
- Roles:
- owner: SP1VerifierGatewayMultisig
VerifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. contract for SP1 proofs (v6.0.0).
VerifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. contract for SP1 proofs (v6.1.0).
The current deployment carries some associated risks:
Funds can be stolen if a contract receives a malicious code upgrade. There is no delay on code upgrades (CRITICAL).
Program Hashes
Name | Hash | Repository | Verification | Used in | |||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
0xdb69...b69a | Projects used inSearch for projects used in | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||