Search
Search for projects by name or address
 Forknet
Badges
About
An onchain order book DEX for spot and perpetuals, built on CDK OP Stack and natively integrated with Agglayer for unified liquidity.
Badges
About
An onchain order book DEX for spot and perpetuals, built on CDK OP Stack and natively integrated with Agglayer for unified liquidity.
Why is the project listed in others?
Consequence: projects without a proper proof system fully rely on single entities to safely update the state. A malicious proposer can finalize an invalid state, which can cause loss of funds.
Learn more about the recategorisation here.
The section shows the operating costs that L2s pay to Ethereum.
This section shows how much data the project publishes to its data-availability (DA) layer over time. The project currently posts data to Ethereum.
This section shows how "live" the project's operators are by displaying how frequently they submit transactions of the selected type. It also highlights anomalies - significant deviations from their typical schedule.
Last 30 day anomalies
All liveness anomalies detected for this project in the last 30 days, helping you review recent downtime and availability issues.
No Tx data submissions were performed for 1h 3m (from 2026 Sep 03, 07:09 UTC until 2026 Sep 03, 08:12 UTC). These typically occur every 1h 4m on average.
Funds can be stolen if
In the event of a sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. failure, users can force transactions to be included in the project’s chain by sending them to L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development.. There can be up to a 12h delay on this operation.
Currently the system permits invalid state rootsA cryptographic hash succinctly representing a state using a Merkle tree.. ‘Pessimistic’ proofs only validate the bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. accounting.
All of the data needed for proof construction is published on Ethereum L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development..
There is no window for users to exit in case of an unwanted upgrade since contracts are instantly upgradable.
Only the whitelisted proposers can publish state rootsA cryptographic hash succinctly representing a state using a Merkle tree. on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development., so in the event of failure the withdrawals are frozen.
Data is posted on Ethereum
Transaction data is posted to Ethereum L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. as compressed calldata or blobsThe data that a rollup publishes to its L1/data availability (DA) layer. They consist of the L2 transactions that are rolled up, along with some metadata. Blobs are introduced as a new transaction type within Ethereum with EIP-4844, and has rollup scaling specifically in mind. Blobs persist on Ethereum’s Beacon Chain ephemerally. through the OP Stack batch inbox.
Ethereum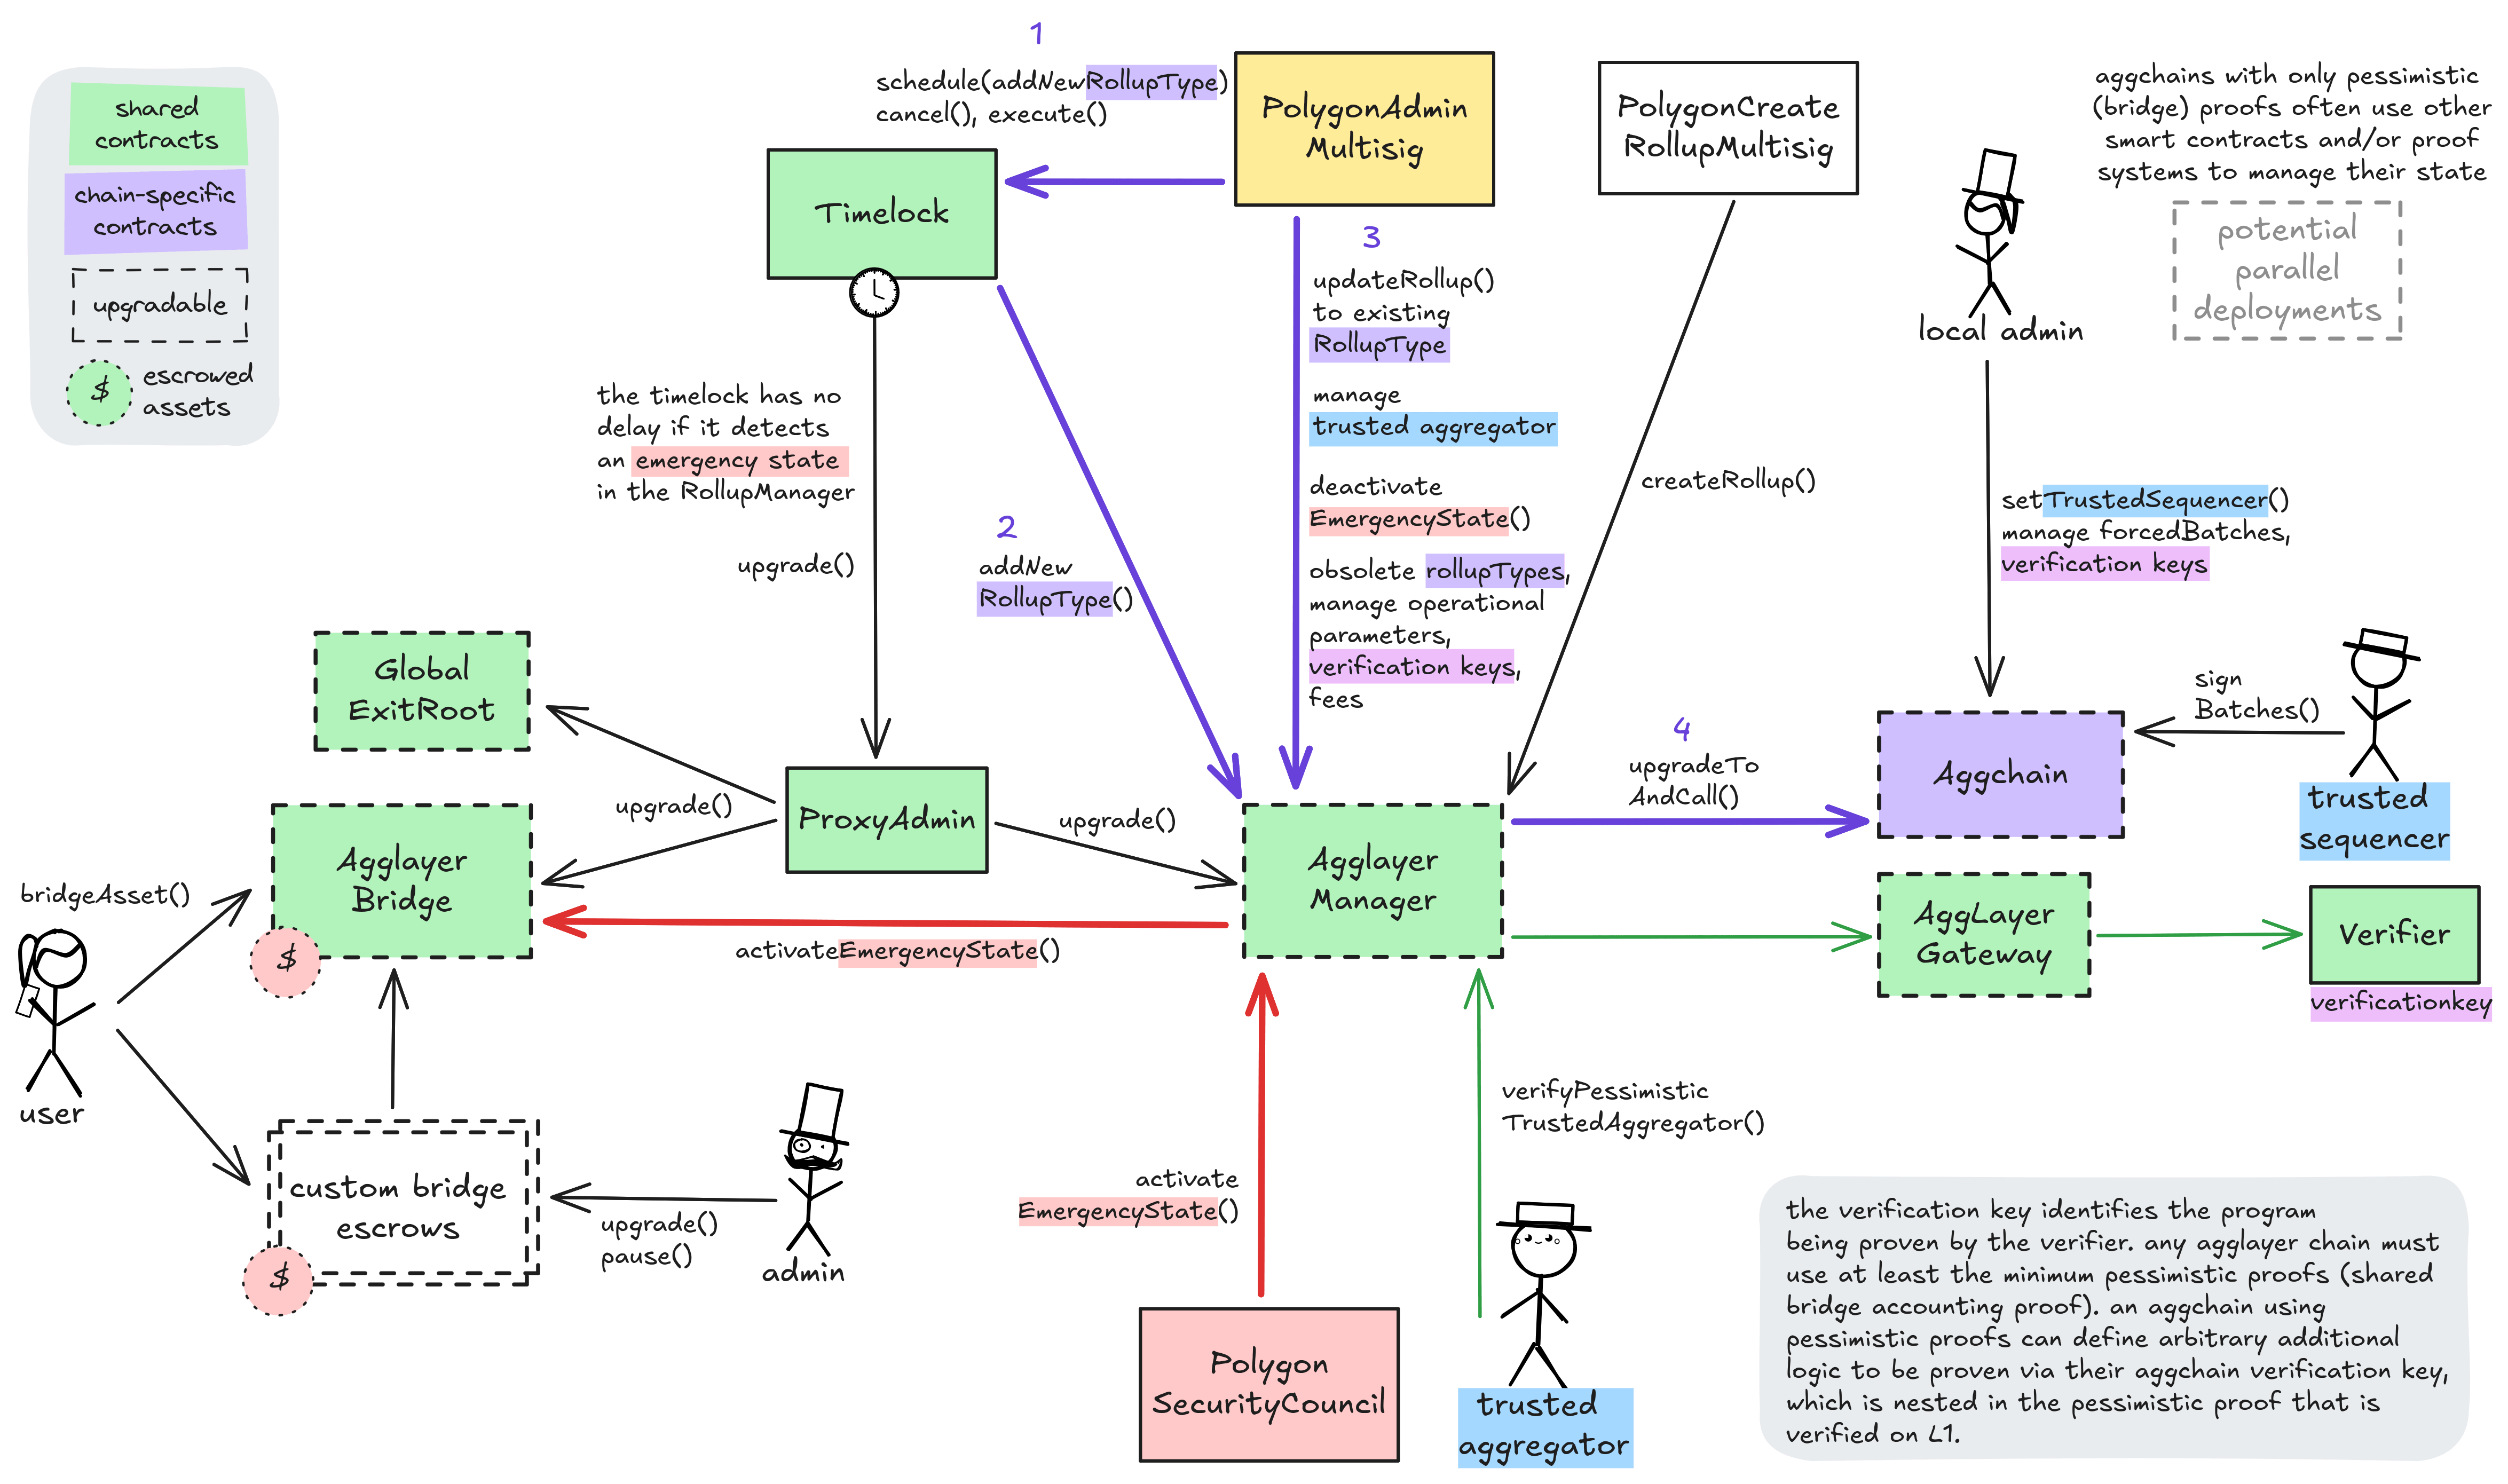
The regular upgrade process for shared system contracts and L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups.-specific validiumAn off-chain solution that uses validity proofs for settlement and publishes the data offchain, therefore requiring an additional trust assumption. contracts starts at the PolygonAdminMultisig. For the shared contracts, they schedule a transaction that targets the ProxyAdmin via the Timelock, wait for 3d and then execute the upgrade. An upgrade of the Layer 2 specific validium contract requires first adding a new rollupType through the Timelock and the AgglayerManager (defining the new implementation and verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. contracts). Now that the rollupType is created, either the local admin or the PolygonAdminMultisig can immediately upgrade the local system contracts to it. Chains using pessimistic proofs often have completely sovereign upgrade paths from the ones described here, but the shared contracts still remain relevant to them because they use them as escrow.
The PolygonSecurityCouncil can expedite the upgrade process by declaring an emergency state. This state pauses both the shared bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. and the AgglayerManager and allows for instant upgrades through the timelock. Accordingly, instant upgrades for all system contracts are possible with the cooperation of the SecurityCouncil. The emergency state has been activated 1 time(s) since inception.
Furthermore, the PolygonAdminMultisig is permissioned to manage the shared trusted aggregator (proposerIn the context of L2s, the actor that proposes a claimed state root on L1. The term is also used in the context of Ethereum to refer to the actor that proposes a new block. and proverAn entity that generates the cryptographic proof to convince the verifier that the statement is true. In a ZK-Rollup, the prover generates the ZK (validity) proof to submit to the verifier contract.) for all participating Layer 2s, deactivate the emergency state, obsolete rollupTypes and manage operational parameters and fees in the AgglayerManager directly. The local admin of a specific Aggchain can manage their chain by choosing the trusted sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs., manage forced batches and set the data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium. config. For sovereign chains using pessimistic proofs they can manage any proof logic that might be used on top of the minimal pessimistic one. Creating new Layer 2s (of existing rollupType) is outsourced to the PolygonCreateRollupMultisig but can also be done by the PolygonAdminMultisig. Custom non-shared bridge escrows have their custom upgrade admins listed in the permissions section.
Past upgrades
The metrics include upgrades on the currently used proxy contracts. Historical proxy contracts and changes of such are not included.
2026 August 25, 07:57 UTC2changesMultisig signer change.
Multisig signer change.
| contract Conduit Multisig 1 (eth:0x4a4962275DF8C60a80d3a25faEc5AA7De116A746) [GnosisSafe] { | |
| +++ description: None | |
| values.$members.0: | |
| + | "eth:0x9402c42dB162d5a0927c032136f40Cc9C71853F2" |
| values.multisigThreshold: | |
| - | "4 of 10 (40%)" |
| + | "4 of 11 (36%)" |
| } | |
2026 August 14, 08:40 UTCHigh severity8changesRevert prev. update. SuperchainConfig implementation upgraded v2.4.0 → v2.4.2 (diff) via a StorageSetter step in one transaction; guardian re-initialised unchanged.
Revert prev. update.
SuperchainConfig implementation upgraded v2.4.0 → v2.4.2 (diff) via a StorageSetter step in one transaction; guardian re-initialised unchanged.
| contract SuperchainConfig (eth:0x097f99768A0a4a0A81bAbbCB1ea18193bA9D53cC) [opstack/SuperchainConfigFake_expiry] { | |
| +++ description: Since this contract is deployed in the context of a neutered op stack system, the guardian role has no significance. | |
| sourceHashes.1: | |
| - | "0x5fb525d1572fb90d060d122143b915059cbff39e0298b345857fd4267d7f6b28" |
| + | "0x2cd597b7305a446a1df355e6909cbd75fe38aa045faf4876a8e5496eebc1734f" |
| values.$implementation: | |
| - | "eth:0xb08Cc720F511062537ca78BdB0AE691F04F5a957" |
| + | "eth:0xE4F9779ab53070a55db24dFAeFf9AF147c6ED550" |
| values.$pastUpgrades.8: | |
| + | ["2026-08-13T13:32:47.000Z","0x2c62c31e4108c24123b9f5b3c26a87e5ec6b4fc3b85163c7257edb523316f9db",["eth:0x2476c911E6D4D9411E677D8Faf15a64ac1fDEEe8"]] |
| values.$pastUpgrades.9: | |
| + | ["2026-08-13T13:32:47.000Z","0x2c62c31e4108c24123b9f5b3c26a87e5ec6b4fc3b85163c7257edb523316f9db",["eth:0xE4F9779ab53070a55db24dFAeFf9AF147c6ED550"]] |
| values.$upgradeCount: | |
| - | 8 |
| + | 10 |
| values.version: | |
| - | "2.4.0" |
| + | "2.4.2" |
| implementationNames.eth:0xb08Cc720F511062537ca78BdB0AE691F04F5a957: | |
| - | "SuperchainConfig" |
| implementationNames.eth:0xE4F9779ab53070a55db24dFAeFf9AF147c6ED550: | |
| + | "SuperchainConfig" |
| } | |
2026 August 10, 08:37 UTCHigh severity9changesSuperchainConfig downgrade to a known and feature-identical version. https://disco.l2beat.com/diff/eth:0xE4F9779ab53070a55db24dFAeFf9AF147c6ED550/eth:0xb08Cc720F511062537ca78BdB0AE691F04F5a957
SuperchainConfig downgrade to a known and feature-identical version.
https://disco.l2beat.com/diff/eth:0xE4F9779ab53070a55db24dFAeFf9AF147c6ED550/eth:0xb08Cc720F511062537ca78BdB0AE691F04F5a957
| contract SuperchainConfig (eth:0x097f99768A0a4a0A81bAbbCB1ea18193bA9D53cC) [opstack/SuperchainConfigFake_expiry] { | |
| +++ description: Since this contract is deployed in the context of a neutered op stack system, the guardian role has no significance. | |
| sourceHashes.1: | |
| - | "0x2cd597b7305a446a1df355e6909cbd75fe38aa045faf4876a8e5496eebc1734f" |
| + | "0x5fb525d1572fb90d060d122143b915059cbff39e0298b345857fd4267d7f6b28" |
| values.$implementation: | |
| - | "eth:0xE4F9779ab53070a55db24dFAeFf9AF147c6ED550" |
| + | "eth:0xb08Cc720F511062537ca78BdB0AE691F04F5a957" |
| values.$pastUpgrades.5: | |
| + | ["2026-08-04T13:59:35.000Z","0xfb6124f237aaaccedd1f8d1298ae5f3b19871f7af18bd4c791a818487cc199de",["eth:0x4da82a327773965b8d4D85Fa3dB8249b387458E7"]] |
| values.$pastUpgrades.6: | |
| + | ["2026-08-04T14:11:35.000Z","0xf7dd2207111f0f269b7cdfa8a7fa703b664585513bc113e0d2c8bc7ce9eb355f",["eth:0xCe28685EB204186b557133766eCA00334EB441E4"]] |
| values.$pastUpgrades.7: | |
| + | ["2026-08-04T14:16:11.000Z","0xeb6b35d861c5b232c47bc0e604f0834975876f80181776e46cb486f7a398cf03",["eth:0xb08Cc720F511062537ca78BdB0AE691F04F5a957"]] |
| values.$upgradeCount: | |
| - | 5 |
| + | 8 |
| values.version: | |
| - | "2.4.2" |
| + | "2.4.0" |
| implementationNames.eth:0xE4F9779ab53070a55db24dFAeFf9AF147c6ED550: | |
| - | "SuperchainConfig" |
| implementationNames.eth:0xb08Cc720F511062537ca78BdB0AE691F04F5a957: | |
| + | "SuperchainConfig" |
| } | |
2026 July 20, 16:06 UTCHigh severity8changesShared Conduit SuperchainConfig upgraded 2.4.0 → 2.4.2 (diff). No behavioral change — just an import-path move, a stale pause-state warning removed, and the version tick, as with the main-Superchain upgrade on 2026-06-25.
Shared Conduit SuperchainConfig upgraded 2.4.0 → 2.4.2 (diff). No behavioral change — just an import-path move, a stale pause-state warning removed, and the version tick, as with the main-Superchain upgrade on 2026-06-25.
| contract SuperchainConfig (eth:0x097f99768A0a4a0A81bAbbCB1ea18193bA9D53cC) [opstack/SuperchainConfigFake_expiry] { | |
| +++ description: Since this contract is deployed in the context of a neutered op stack system, the guardian role has no significance. | |
| sourceHashes.1: | |
| - | "0x5fb525d1572fb90d060d122143b915059cbff39e0298b345857fd4267d7f6b28" |
| + | "0x2cd597b7305a446a1df355e6909cbd75fe38aa045faf4876a8e5496eebc1734f" |
| values.$implementation: | |
| - | "eth:0xb08Cc720F511062537ca78BdB0AE691F04F5a957" |
| + | "eth:0xE4F9779ab53070a55db24dFAeFf9AF147c6ED550" |
| values.$pastUpgrades.3: | |
| + | ["2026-07-17T11:30:11.000Z","0x1f1d4768cc0d3f218a3f5aea7b6ceed0ae663498958e8194f208e88522c6404b",["eth:0x2476c911E6D4D9411E677D8Faf15a64ac1fDEEe8"]] |
| values.$pastUpgrades.4: | |
| + | ["2026-07-17T11:30:11.000Z","0x1f1d4768cc0d3f218a3f5aea7b6ceed0ae663498958e8194f208e88522c6404b",["eth:0xE4F9779ab53070a55db24dFAeFf9AF147c6ED550"]] |
| values.$upgradeCount: | |
| - | 3 |
| + | 5 |
| values.version: | |
| - | "2.4.0" |
| + | "2.4.2" |
| implementationNames.eth:0xb08Cc720F511062537ca78BdB0AE691F04F5a957: | |
| - | "SuperchainConfig" |
| implementationNames.eth:0xE4F9779ab53070a55db24dFAeFf9AF147c6ED550: | |
| + | "SuperchainConfig" |
| } | |
2026 June 10, 13:12 UTC3changesTwo conduit ms members removed.
Two conduit ms members removed.
| contract Conduit Multisig 1 (eth:0x4a4962275DF8C60a80d3a25faEc5AA7De116A746) [GnosisSafe] { | |
| +++ description: None | |
| values.$members.4: | |
| - | "eth:0x65D1d44B8B2fE15d45A03708E0835C7E98a56007" |
| values.$members.8: | |
| - | "eth:0xa4000bDD2bB92ce6750b31F1eeda47Bd1cB8e6e4" |
| values.multisigThreshold: | |
| - | "4 of 12 (33%)" |
| + | "4 of 10 (40%)" |
| } | |
Users can force any transaction
Because the state of the system is based on transactions submitted on the underlying host chain and anyone can submit their transactions there it allows the users to circumvent censorship by interacting with the smart contract on the host chain directly.
Regular messaging
The user initiates L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups.->L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. messages by submitting a regular transaction on this chain. When the blockAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over. containing that transaction is settled, the message becomes available for processing on L1. ZK proofs are required to settle blocks.
Shared bridge and Pessimistic Proofs
Polygon Agglayer uses a shared bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. escrow for Rollups, Validiums and external chains that opt in to participate in interoperabilityRefers to the capability of different blockchain networks to communicate and share data. It enables the transfer of assets and information between blockchains, facilitating functionality and collaboration between blockchain ecosystems.. Each participating chain needs to provide zk proofs to access any assets in the shared bridge. In addition to the full execution proofs that are used for the state validation of Rollups and Validiums, accounting proofs over the bridges state (Polygon calls them ‘Pessimistic Proofs’) are used by external chains (cdk-erigon-sovereign and cdk-opgeth-sovereign variants). Using the SP1 zkVMA special type of zk proving system that proves the correctness of state transitions of a virtual machine. Computation is represented by a program in a specific instruction language, it can have private and public inputs and public outputs. Most of zkVMs are STARKs. by Succinct, even projects without a full proof systemThe infrastructure that allows projects to verify their state transitions. It is composed by onchain verifiers and offchain provers. The main two flavors are optimistic and ZK proof systems, but they can be combined in a hybrid model. In general though, if a system is able to accept state roots optimistically, even if it has a ZK component, it is considered an optimistic proof system. on Ethereum are able to share the bridge with any other Aggchain without adding additional trust assumptions.
Funds can be lost if the accounting proof system for the bridge (pessimistic proofs, SP1) is implemented incorrectly.
Funds can be stolen if the operator manipulates the L2 state, which is not validated on Ethereum (CRITICAL).
Ethereum
Actors:
A Multisig with 5/9 threshold.
- Can upgrade with 3d delay
- AgglayerGateway Timelock with 3d delay (no delay if in emergency state) → SharedProxyAdmin
- AgglayerBridge Timelock with 3d delay (no delay if in emergency state) → SharedProxyAdmin
- AgglayerManager Timelock with 3d delay (no delay if in emergency state) → SharedProxyAdmin
- AgglayerGER Timelock with 3d delay (no delay if in emergency state) → SharedProxyAdmin
- Can interact with AgglayerGateway
- add new routes from proof selector to verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. / pessimisticVkey for pessimistic proofs with 3d delay Timelock with 3d delay (no delay if in emergency state)
- add or update default aggchain verification keys (aggchainVkey) for any given selectors
- change the aggchainSigners and threshold (a multisig used for permissioned state transitions)
- freeze routes from proof selector to verifier / pessimisticVkey for pessimistic proofs
- Can interact with AgglayerBridge
- upgrade the implementation of wrapped tokens deployed by the bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. with 3d delay Timelock with 3d delay (no delay if in emergency state)
- Can interact with AgglayerManager
- deploy new projects that use predefined rollupA blockchain that inherits consensus and data availability from another blockchain called L1. Rollups enable trust minimized bridges with the base layer via proof systems, either optimistic or zero-knowledge. A rollup without a bridge, or without considering the bridge, is called a sovereign rollup. types (implementations) and connect them or other Agglayer chains to the PolygonRollupManager
- manage all access control roles, add new rollup types (which are implementation contracts that can then be upgraded to by connected projects), update any connected projects to new rollup types, migrate to pessimistic proofs and rollback batches, connect existing rollups to the PolygonRollupManager with 3d delay Timelock with 3d delay (no delay if in emergency state)
- manage parameters like fees for all connected projects, set the trusted aggregator, stop the emergency state, update projects and obsolete rollup types
- Can interact with Timelock
- propose, cancel and execute transactions in the timelock, manage all access control roles and change the minimum delay with 6d delay or with 3d delay Timelock with 3d delay (no delay if in emergency state) with 3d delay (no delay if in emergency state) - or - acting directly with 3d delay (no delay if in emergency state)
Participants (9):
0xEB5E…EA720xAb35…235E0xf02B…D4B20xdFEd…56Da0xffbf…32380xeD44…dB370x516e…46B70x2161…d4170x8B9F…782BA Multisig with 4/11 threshold.
- Can upgrade with no delay
- DelayedWETH ProxyAdmin
- SuperchainConfig ProxyAdmin
- OptimismMintableERC20Factory ProxyAdmin
- SystemConfig ProxyAdmin
- L1StandardBridge ProxyAdmin
- DisputeGameFactory ProxyAdmin
- L1CrossDomainMessenger ProxyAdmin
- L1ERC721Bridge ProxyAdmin
- OptimismPortal2 ProxyAdmin
- AnchorStateRegistry ProxyAdmin
- Can interact with AddressManager
- set and change address mappings ProxyAdmin
- Can interact with SystemConfig
- it can update the preconfer address, the batch submitter (SequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs.) address and the gasA virtual fuel used to execute smart contracts on a rollup. The EVM (or other VM within the rollup) uses an accounting mechanism to correspond the consumption of gas to the consumption of computing resources, and to limit the consumption of computing resources. configuration of the system
Participants (11):
0x9402…53F20xcdC9…48530xA9FC…8d090x6BB4…83A60x2103…911c0x8117…E7Ac0xA073…bda20xF331…647D0xa0C6…90380xefCf…dD5C0x4D80…5BAeThe central shared managing contract for Polygon Agglayer chains. This contract coordinates chain deployments and proof validation. All connected Layer 2s can be globally paused by activating the ‘Emergency State’. This can be done by the PolygonSecurityCouncil or by anyone after 1 week of inactive verifiers.
- Can upgrade with no delay
- AggchainECDSAMultisig
A Multisig with 6/8 threshold.
- Can interact with AgglayerManager
- activate the emergency state in the PolygonRollupManager and in the shared bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. immediately, effectively pausing all projects connected to them and making system contracts instantly upgradable
Participants (8):
0xFe45…2e4b0xaF46…261D0xBDc2…FEFf0x4c16…88910x3ab9…D6220x49c1…0E860x9F7d…86A00x2188…1C28A Multisig with 3/5 threshold.
- Can interact with AgglayerManager
- deploy new projects that use predefined rollupA blockchain that inherits consensus and data availability from another blockchain called L1. Rollups enable trust minimized bridges with the base layer via proof systems, either optimistic or zero-knowledge. A rollup without a bridge, or without considering the bridge, is called a sovereign rollup. types (implementations) and connect them or other Agglayer chains to the PolygonRollupManager
- Can interact with SystemConfig
- Allowed to commit transactions from the current layer to the host chain
- Can interact with AggchainECDSAMultisig
- set the trusted sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. address
- Can interact with AggchainECDSAMultisig
- sign state transitions (replaces state validation for this aggchain)
- Can interact with AgglayerManager
- Permissioned to post new state rootsA cryptographic hash succinctly representing a state using a Merkle tree. and global exit roots accompanied by ZK proofs

Ethereum
System contract defining the forknet Aggchain logic. It only enforces bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. accounting (pessimistic) proofs to protect the shared bridge while the Aggchain state transitions are not proven. They must instead be signed by 1 aggchainSigner(s).
- Roles:
- admin: AgglayerManager, EOA 2
- aggchainSigners: EOA 3
Contains configuration parameters such as the SequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. address, gas limitThe maximum amount of gas a transaction or block may consume. on this chain and the unsafe blockAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over. signer address.
- Roles:
- admin: ProxyAdmin; ultimately Conduit Multisig 1
- batcherHash: EOA 1
- owner: Conduit Multisig 1
The dispute game factory allows the creation of dispute games, used to propose state rootsA cryptographic hash succinctly representing a state using a Merkle tree. and eventually challenge them.
- Roles:
- admin: ProxyAdmin; ultimately Conduit Multisig 1
The OptimismPortal contract usually is the main entry point to deposit funds from L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. to L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. or for finalizing withdrawals. It specifies which game type can be used for withdrawals, which currently is the PermissionedDisputeGame. This specific contract is deployed in the agglayer system context which disables the depositTransaction() function, preventing users from sending or forcing any transactions from L1 to L2, including token deposits. It is instead used for configuration and administration of the system.
- Roles:
- admin: ProxyAdmin; ultimately Conduit Multisig 1
A verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. gateway for pessimistic proofs. Manages a map of chains and their verifier keys and is used to route proofs based on the first 4 bytes of proofBytes data in a proof submission. The SP1 verifier is used for all proofs.
- Roles:
- addPpRoute: Timelock; ultimately PolygonAdminMultisig
- admin: SharedProxyAdmin; ultimately PolygonAdminMultisig
- aggchainDefaultVKey: PolygonAdminMultisig
- alMultisig: PolygonAdminMultisig
- freezePpRoute: PolygonAdminMultisig
The shared bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. contract, escrowing user funds sent to Agglayer chains. It is usually mirrored on each chain and can be used to transfer both ERC20 assets and arbitrary messages.
- Roles:
- admin: SharedProxyAdmin; ultimately PolygonAdminMultisig
- proxiedTokensManager: Timelock; ultimately PolygonAdminMultisig
All supported tokens in this escrow are included in the value secured calculation.
A merkle treeA hash-based data structure in which each leaf node is a hash of a block of data, and each non-leaf node is a hash of its children. The root of the tree is a cryptographic fingerprint of the entire data structure. Merkle trees (Merkle Patricia Tries) are used in Ethereum to efficiently store key-value pairs. storage contract aggregating state rootsA cryptographic hash succinctly representing a state using a Merkle tree. of each participating Layer 2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups., thus creating a single global merkle root representing the global state of the Agglayer, the ‘global exit root’. The global exit root is synchronized to all connected Layer 2s to help with their interoperabilityRefers to the capability of different blockchain networks to communicate and share data. It enables the transfer of assets and information between blockchains, facilitating functionality and collaboration between blockchain ecosystems..
- Roles:
- admin: SharedProxyAdmin; ultimately PolygonAdminMultisig
A timelock with access control. In the case of an activated emergency state in the AgglayerManager, all transactions through this timelock are immediately executable. The current minimum delay is 3d.
- Roles:
- timelockAdmin: PolygonAdminMultisig (no delay if in emergency state), Timelock (no delay if in emergency state); ultimately PolygonAdminMultisig (no delay if in emergency state)
The main entry point to deposit ERC20 tokens from host chain to this chain.
- Roles:
- admin: ProxyAdmin; ultimately Conduit Multisig 1
Sends messages from host chain to this chain, and relays messages back onto host chain. In the event that a message sent from host chain to this chain is rejected for exceeding this chain’s epoch gas limitThe maximum amount of gas a transaction or block may consume., it can be resubmitted via this contract’s replay function.
- Roles:
- admin: ProxyAdmin; ultimately Conduit Multisig 1
Used to bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. ERC-721 tokens from host chain to this chain.
- Roles:
- admin: ProxyAdmin; ultimately Conduit Multisig 1
Contract designed to hold the bonded ETH for each game. It is designed as a wrapper around WETH to allow an owner to function as a backstop if a game would incorrectly distribute funds.
- Roles:
- admin: ProxyAdmin; ultimately Conduit Multisig 1
The PreimageOracle contract is used to load the required data from L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. for a dispute game.
A helper contract that generates OptimismMintableERC20 contracts on the networkA constellation of nodes (peers) that communicate via a peer-to-peer protocol, for example, in propagating transactions and blocks to other nodes. it’s deployed to. OptimismMintableERC20 is a standard extension of the base ERC20 token contract designed to allow the L1StandardBridge contracts to mint and burn tokens. This makes it possible to use an OptimismMintableERC20 as this chain’s representation of a token on the host chain, or vice-versa.
- Roles:
- admin: ProxyAdmin; ultimately Conduit Multisig 1
The MIPS contract is used to execute the final step of the dispute game which objectively determines the winner of the dispute.
Same as FaultDisputeGame, but only two permissioned addresses are designated as proposerIn the context of L2s, the actor that proposes a claimed state root on L1. The term is also used in the context of Ethereum to refer to the actor that proposes a new block. and challenger.
- Roles:
- owner: Conduit Multisig 1
Contains the latest confirmed state rootA cryptographic hash succinctly representing a state using a Merkle tree. that can be used as a starting point in a dispute game. It specifies which game type can be used for withdrawals, which currently is the PermissionedDisputeGame.
- Roles:
- admin: ProxyAdmin; ultimately Conduit Multisig 1
VerifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. contract for SP1 proofs (v5.0.0).
Extension contract of the AgglayerBridge for asset metadata…
VerifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. contract for SP1 proofs (v6.1.0).
The current deployment carries some associated risks:
Funds can be stolen if a contract receives a malicious code upgrade. There is no delay on code upgrades (CRITICAL).