Search
Search for projects by name or address
 MegaETH
There are impactful changes and part of the information might be outdated.
Badges
About
MegaETH is a real-time blockchain based on the OP Stack architecture and the hybrid Kailua proof system, targeting sub-millisecond latency and over 100,000 transactions per second.
Badges
About
MegaETH is a real-time blockchain based on the OP Stack architecture and the hybrid Kailua proof system, targeting sub-millisecond latency and over 100,000 transactions per second.
Why is the project listed in others?
Consequence: projects without a sufficiently decentralized set of challengers rely on few entities to safely update the state. A small set of challengers can collude with the proposer to finalize an invalid state, which can cause loss of funds.
Consequence: projects without a data availability bridge fully rely on single entities (the sequencer) to honestly rely available data roots on Ethereum. A malicious sequencer can collude with the proposer to finalize an unavailable state, which can cause loss of funds.
Learn more about the recategorisation here.
The section shows the operating costs that L2s pay to Ethereum.
This section shows how much data the project publishes to its data-availability (DA) layer over time. The project currently posts data to EigenDA.
This section shows how "live" the project's operators are by displaying how frequently they submit transactions of the selected type. It also highlights anomalies - significant deviations from their typical schedule.
Funds can be stolen if
- a contract receives a malicious code upgrade. There is no delay on code upgrades (CRITICAL),
- the validity proof cryptography is broken or implemented incorrectly,
- no challenger checks the published state,
- the proposer routes proof verification through a malicious or faulty verifier by specifying an unsafe route selector.
Funds can be lost if
Funds can be frozen if
MEV can be extracted if
In the event of a sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. failure, users can force transactions to be included in the project’s chain by sending them to L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development.. There can be up to a 12h delay on this operation.
Fraud proofs allow actors watching the chain to prove that the state is incorrect. Single round proofs (1R) prove the validity of a state proposal, only requiring a single transaction to resolve. A fault proof eliminates a state proposal by proving that any intermediate state transition in the proposal results in a different state rootA cryptographic hash succinctly representing a state using a Merkle tree.. For either, a ZK proof is used. Since the nodeA software client that participates in the network. source is not available, challengers cannot watch the chain independently. vanguardAdvantage applies to every proposal and is set to 36558901084y 8mo, so only the Vanguard can submit state proposals; faulty proposals can be flagged but not replaced, halting the chain until the Vanguard proposes a correct state root.
Proof construction and state derivation fully rely on data that is posted on EigenDA. The sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. is publishing data to EigenDA v2. Sequencer transaction data roots are not checked against the DACert VerifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. onchain.
There is no window for users to exit in case of an unwanted upgrade since contracts are instantly upgradable.
Only the whitelisted proposers can publish state rootsA cryptographic hash succinctly representing a state using a Merkle tree. on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development., so in the event of failure the withdrawals are frozen.
Data is posted to EigenDA
Transactions roots are posted onchain and the full data is posted on EigenDA. The sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. is publishing data to EigenDA v2. Since the DACert VerifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. is not used, availability of the data is not verified against EigenDA operators, meaning that the Sequencer can single-handedly publish unavailable commitments. If EigenDA becomes unavailable, the sequencer falls back to Ethereum.
Funds can be lost if the sequencer posts an unavailable transaction root (CRITICAL).
Funds can be lost if the data is not available on the external provider (CRITICAL).
- EigenDA Docs - Overview
- Derivation: Batch submission - OP Mainnet specs
- BatchInbox - address
- OptimismPortal2.sol - source code, depositTransaction function
EigenDA
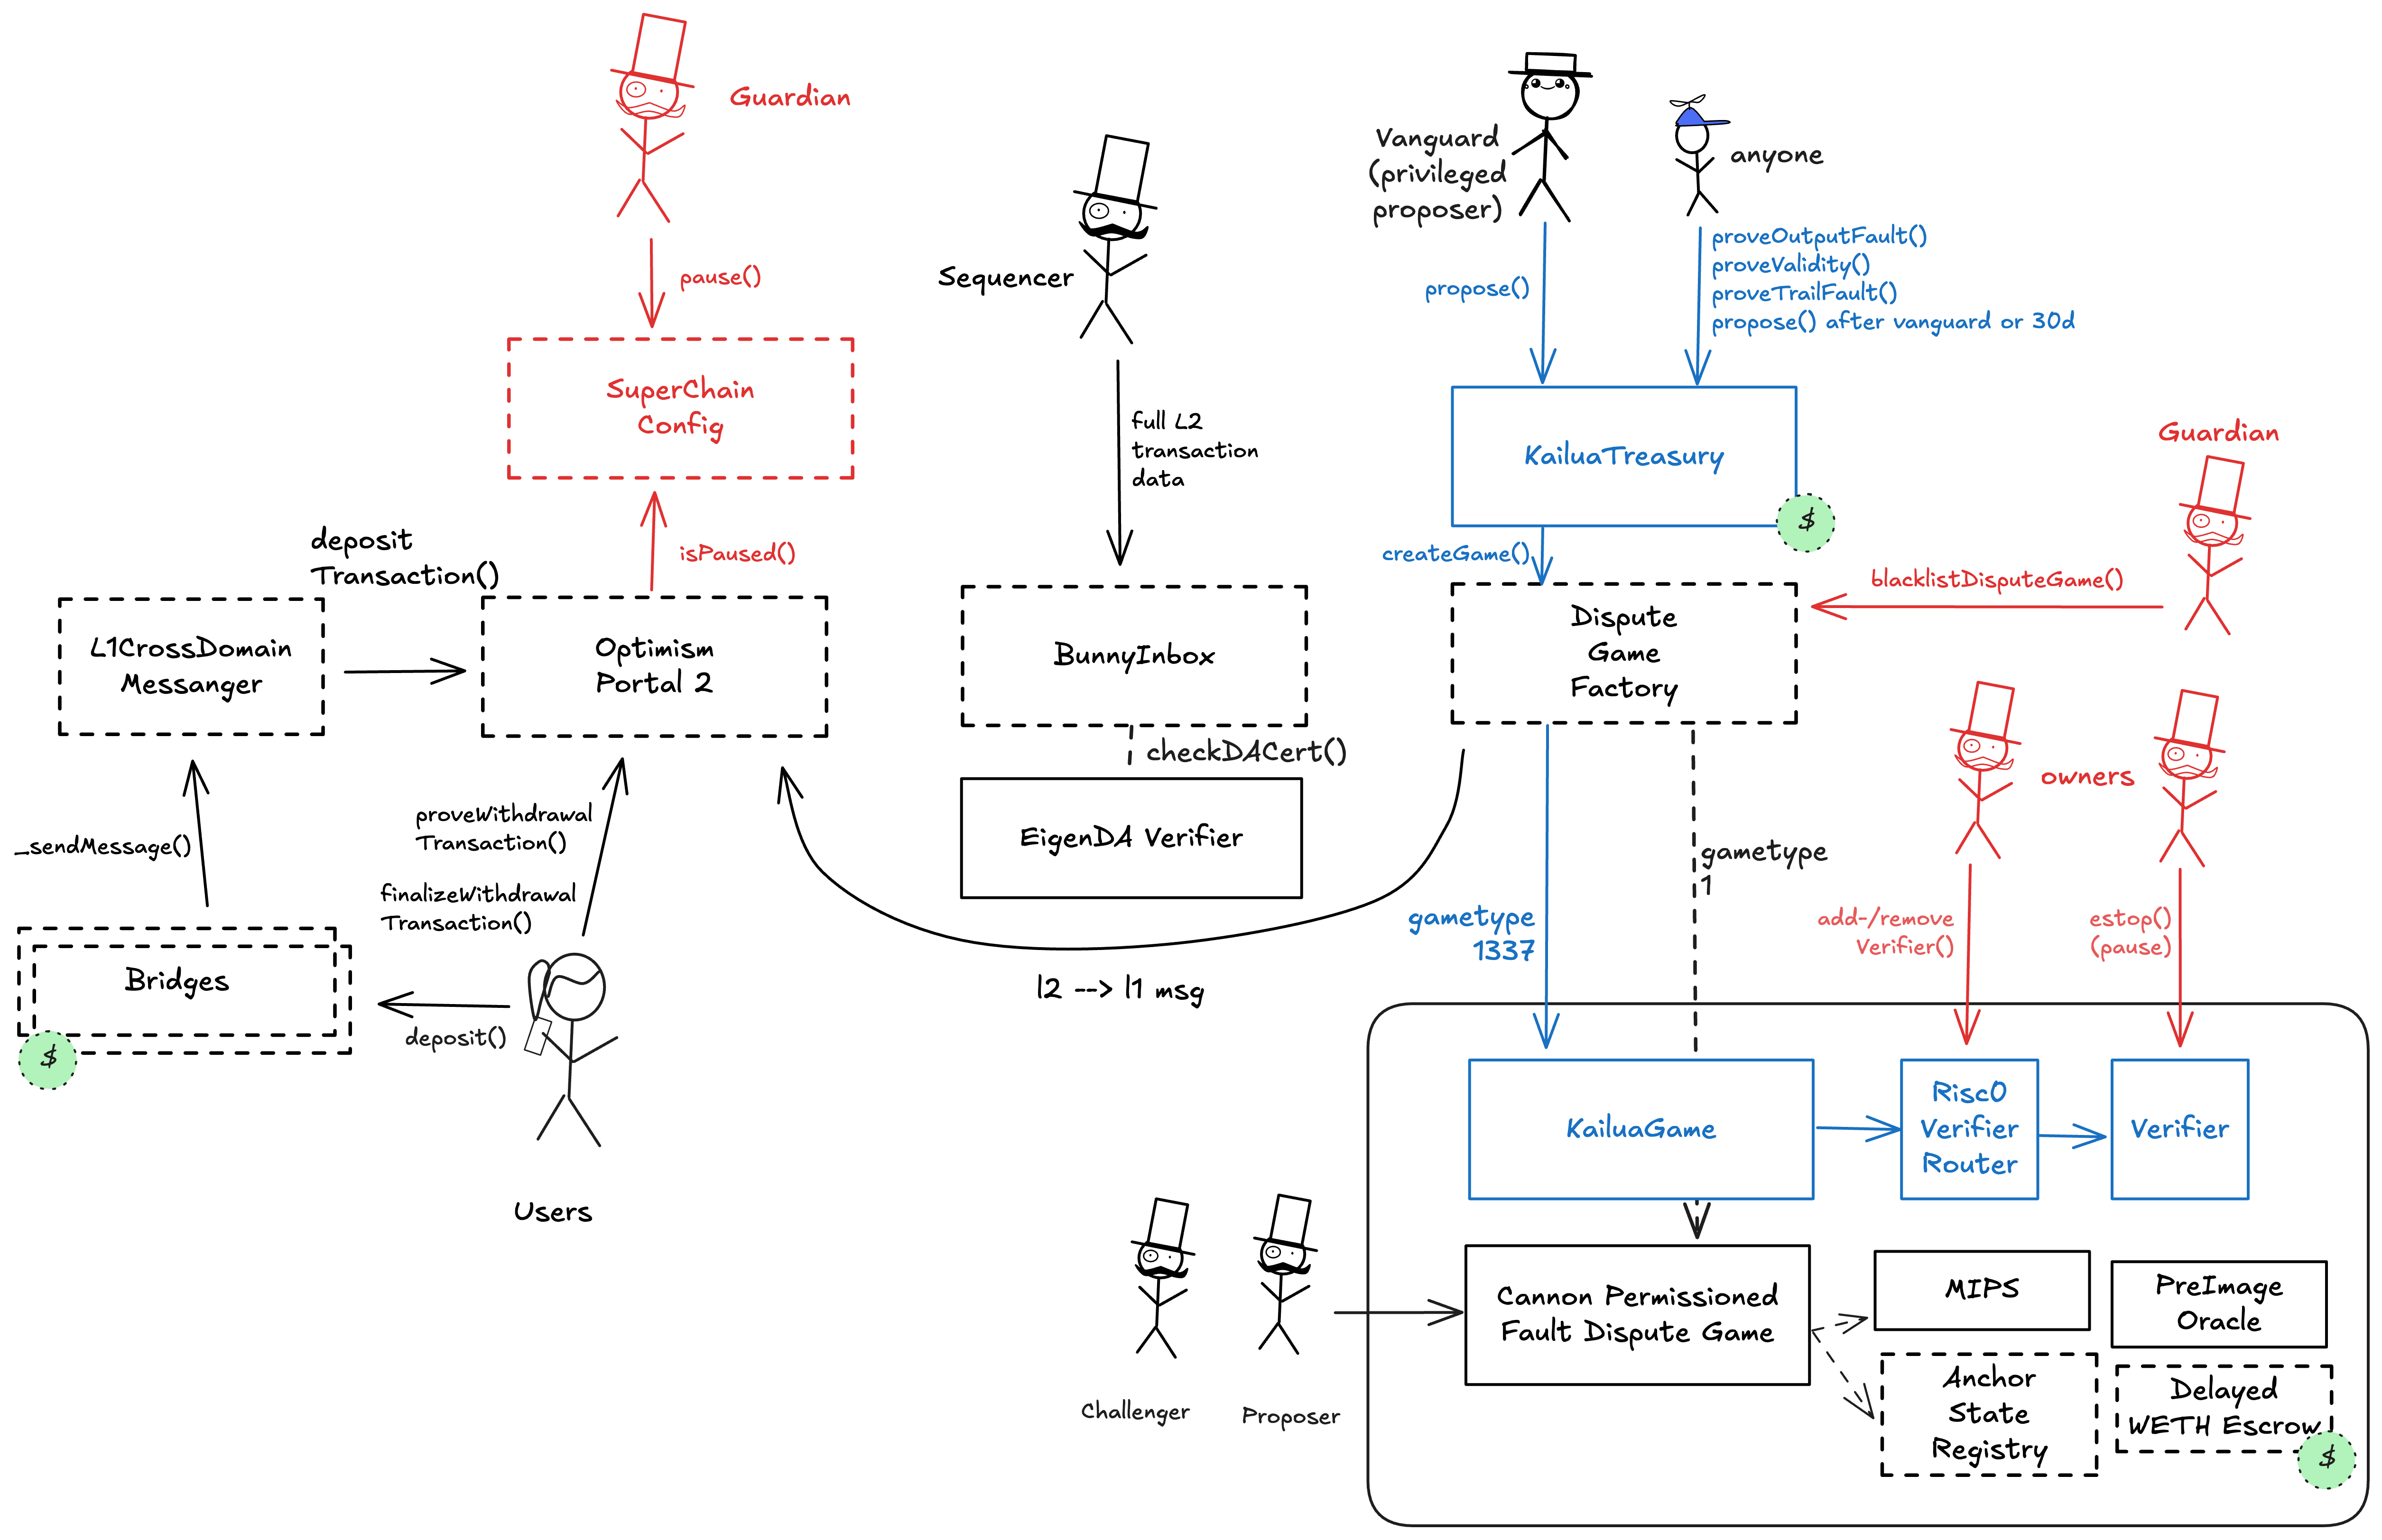
Proposers submit state rootsA cryptographic hash succinctly representing a state using a Merkle tree. as children of any (possibly unresolved) previous state root proposal, by calling the propose() function in the KailuaTreasury. A parent state root can have multiple conflicting children, composing a tournament. Each proposerIn the context of L2s, the actor that proposes a claimed state root on L1. The term is also used in the context of Ethereum to refer to the actor that proposes a new block. requires to lock a bond, currently set to 0.00001 ETH, that can be slashed if any proposal made by them is proven incorrect via a fault proof or a conflicting validity proofThe output of a cryptographic proving system attesting to correct computation. ZK-Rollups use succinct validity proofs (also called zero-knowledge proofs) to prove a batch of rollup transactions and blocks were properly executed. Validity proofs are submitted to a verifier, such as an Ethereum smart contract, which accepts them if properly constructed.. The bond can be withdrawn once the proposer has no more pending proposals that need to be resolved and was not eliminated.
Proposals consist of a state root and a reference to their parent and implicitly challenge any sibling proposals who have the same parent. A proposal asserts that the proposed state root constitutes a valid state transition from the parent’s state root. To offer efficient zk fault proofs, each proposal must include 3600 intermediate state commitments, each spanning 1 L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. blocksAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over..
Proposals target sequential tournament epochs of currently 3600 * 1 L2 blocks. A tournament with a resolved parent tournament, a single child- and no conflicting sibling proposals can be resolved after 7d.
The Vanguard is the only address that can submit any proposal (first child or conflicting sibling) on a parent state root during the vanguardAdvantage window of 36558901084y 8mo. Faulty Vanguard proposals can be flagged via ZK fault proofs (proveOutputFault) but cannot be replaced by an honest sibling, so the chain stalls at that tournament until the Vanguard submits a correct state root.
Funds can be frozen if the vanguard exploits their vanguard advantage (36558901084y 8mo), halting the chain until they propose.
Any actor can submit a ZK fault proof against an existing child proposal via proveOutputFault to mark it faulty during the 7d challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled.; this blocksAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over. the wrong proposal from resolving but does not, by itself, advance the chain. Conflicting sibling proposals (which would survive the tournament and resolve in place of a faulty proposal) can only be submitted by the Vanguard during the vanguardAdvantage window.
In the tree of proposed state rootsA cryptographic hash succinctly representing a state using a Merkle tree., each parent nodeA software client that participates in the network. can have multiple children. These children are indirectly challenging each other in a tournament, which can only be resolved if but a single child survives. A state root can be resolved if it is the only remaining proposal due to any combination of the following elimination methods:
- the proposal’s challenge period of 7d has ended before a conflicting proposal was made
- the proposal is proven correct with a full validity proofThe output of a cryptographic proving system attesting to correct computation. ZK-Rollups use succinct validity proofs (also called zero-knowledge proofs) to prove a batch of rollup transactions and blocks were properly executed. Validity proofs are submitted to a verifier, such as an Ethereum smart contract, which accepts them if properly constructed. (invalidates all conflicting proposals)
- a conflicting sibling proposal is proven faulty
Proving any of the 3600 intermediate state commitments in a proposal faulty invalidates the entire proposal. Proving a proposal valid invalidates all conflicting siblings. Pruning of a tournament’s children happens strictly chronologically, which guarantees that the first faulty proposal of a given proposerIn the context of L2s, the actor that proposes a claimed state root on L1. The term is also used in the context of Ethereum to refer to the actor that proposes a new block. is always pruned first. When pruned, an invalid proposal leads to the elimination of its proposer, which invalidates all their subsequent proposals, slashes their bond, and disallows future proposals by the same address. A slashed bond is transferred to an address chosen by the proverAn entity that generates the cryptographic proof to convince the verifier that the statement is true. In a ZK-Rollup, the prover generates the ZK (validity) proof to submit to the verifier contract. who caused the slashing.
A single remaining child in a tournament can be ‘resolved’ and will be finalized and usable for withdrawals after an execution delay of 3d 12h (time for the Guardian to manually blacklist malicious state roots).
Validity proofs and fault proofs both must be accompanied by a ZK proof that ensures that the new state was derived by correctly applying a series of valid user transactions to the previous state. These proofs are then verified on Ethereum by a smart contract.
The Kailua state validation system is primarily optimistically resolved, so no validity proofs are required in the happy case. But two different zk proofs on unresolved state rootsA cryptographic hash succinctly representing a state using a Merkle tree. are possible and permissionlessAnyone willing should be able to join and leave the network at any time, without causing significant disturbance to the network or being detrimental to the party in question. No single entity should have the power to allowlist or blocklist participants.: The proveValidity() function proves a state root proposal’s full validity, automatically invalidating all conflicting sibling proposals. proveOutputFault() allows any actor to eliminate a state root proposal for which they can prove that any of the 3600 intermediate state transitions in the proposal are not correct. Both are zk proofs of validity, although one is used as an efficient fault proof to invalidate a single conflicting state transition.
Funds can be stolen if the validity proof cryptography is broken or implemented incorrectly.
Funds can be stolen if no challenger checks the published state.
Funds can be stolen if the proposer routes proof verification through a malicious or faulty verifier by specifying an unsafe route selector.
Funds can be frozen if a verifier needed for a given proof is paused by its permissioned owner.

Trusted Setups
Onchain verifier
Used in
Onchain verifier | Used in |
Past upgrades
The metrics include upgrades on the currently used proxy contracts. Historical proxy contracts and changes of such are not included.
2026 August 27, 12:37 UTC3changesEigenDAOperationsMultisig: member removed; threshold 3/5 → 2/4.
EigenDAOperationsMultisig: member removed; threshold 3/5 → 2/4.
| contract EigenDAOperationsMultisig (eth:0x002721B4790d97dC140a049936aA710152Ba92D5) [GnosisSafe] { | |
| +++ description: None | |
| values.$members.1: | |
| - | "eth:0xA3e302a6Ea0cf79B8580d94e92Eb5514292daacE" |
| values.$threshold: | |
| - | 3 |
| + | 2 |
| values.multisigThreshold: | |
| - | "3 of 5 (60%)" |
| + | "2 of 4 (50%)" |
| } | |
2026 July 21, 15:39 UTC2changesEigenDAOperationsMultisig: new signer added. Threshold 3/4 → 3/5.
EigenDAOperationsMultisig: new signer added. Threshold 3/4 → 3/5.
| contract EigenDAOperationsMultisig (eth:0x002721B4790d97dC140a049936aA710152Ba92D5) [GnosisSafe] { | |
| +++ description: None | |
| values.$members.0: | |
| + | "eth:0xB646A0871af2b2c6e115b24D7E36d406780b6ca8" |
| values.multisigThreshold: | |
| - | "3 of 4 (75%)" |
| + | "3 of 5 (60%)" |
| } | |
2026 May 11, 21:38 UTCHigh severity8changesKailua game1337 impl rotated 0x78F8F8FE... → 0x8c0Ed8Dd... (diff). Active KailuaTreasury is now 0x01853F26... ; OptimismPortal2.setRespectedGameType(1337) re-pointed the bridge. The proposalParent.childCount() == 1 gate around the vanguard check was removed: vanguardAdvantage applies to every proposal (first child and every sibling). With vanguardAdvantage ≈ 2^60s , only the Vanguard can submit any proposal. Faulty Vanguard proposals can be marked faulty via proveOutputFault but no honest sibling can replace them — chain halts until the Vanguard submits a correct state root. Plumbing: megaeth.ts resolves the active game/treasury dynamically via OptimismPortal2.respectedGameType → DisputeGameFactory.game{N} → its KAILUA TREASURY ; risc0/KailuaGame and megaeth/KailuaTreasury shapes extended for the new contracts.
Kailua game1337 impl rotated 0x78F8F8FE... → 0x8c0Ed8Dd... (diff). Active KailuaTreasury is now 0x01853F26...; OptimismPortal2.setRespectedGameType(1337) re-pointed the bridge.
The proposalParent.childCount() == 1 gate around the vanguard check was removed: vanguardAdvantage applies to every proposal (first child and every sibling). With vanguardAdvantage ≈ 2^60s, only the Vanguard can submit any proposal. Faulty Vanguard proposals can be marked faulty via proveOutputFault but no honest sibling can replace them — chain halts until the Vanguard submits a correct state root.
Plumbing: megaeth.ts resolves the active game/treasury dynamically via OptimismPortal2.respectedGameType → DisputeGameFactory.game{N} → its KAILUA_TREASURY; risc0/KailuaGame and megaeth/KailuaTreasury shapes extended for the new contracts.
| contract Safe (eth:0x63eCafD27E0B86B37903c8aA64beD47244Ad909A) [GnosisSafe] { | |
| +++ description: None | |
| values.$members.0: | |
| + | "eth:0xEd71403a0cC46ED68E57997A225a9620b5Cf0872" |
| values.multisigThreshold: | |
| - | "1 of 4 (25%)" |
| + | "1 of 5 (20%)" |
| } | |
| - | Status: DELETED |
| contract KailuaGame (eth:0x78F8F8FED1d589b7098EC4B47220465A9Fa071C9) [risc0/KailuaGame] | |
| +++ description: Implementation of the KailuaGame with type 1337. Based on this implementation, new KailuaGames are created with every new state root proposal. | |
| contract OptimismPortal2 (eth:0x7f82f57F0Dd546519324392e408b01fcC7D709e8) [opstack/OptimismPortal2] { | |
| +++ description: The OptimismPortal contract is the main entry point to deposit funds from L1 to L2. It also allows to prove and finalize withdrawals. It specifies which game type can be used for withdrawals, which currently is the KailuaGame. | |
| values.respectedGameTypeUpdatedAt: | |
| - | 1762796999 |
| + | 1778245595 |
| } | |
| contract DisputeGameFactory (eth:0x8546840adF796875cD9AAcc5B3B048f6B2c9D563) [opstack/DisputeGameFactory] { | |
| +++ description: The dispute game factory allows the creation of dispute games, used to propose state roots and eventually challenge them. | |
| +++ severity: HIGH | |
| values.game1337: | |
| - | "eth:0x78F8F8FED1d589b7098EC4B47220465A9Fa071C9" |
| + | "eth:0x8c0Ed8Dd0CcF6d596e321d81eD895ad51fE30B84" |
| } | |
| - | Status: DELETED |
| contract KailuaTreasury (eth:0xE4e456c64B9b0de5FE8a90d809180cA71534D623) [megaeth/KailuaTreasury] | |
| +++ description: Entrypoint for state root proposals. Manages bonds (currently 0.00001 ETH) and tournaments for the OP Kailua state validation system, wrapping the OP stack native DisputeGameFactory. | |
| + | Status: CREATED |
| contract KailuaTreasury (eth:0x01853F268B170D4A15D0c3AE905757b5Ec8375f3) [megaeth/KailuaTreasury] | |
| +++ description: Entrypoint for state root proposals. Manages bonds (currently 0.00001 ETH) and tournaments for the OP Kailua state validation system, wrapping the OP stack native DisputeGameFactory. | |
| + | Status: CREATED |
| contract KailuaGame (eth:0x8c0Ed8Dd0CcF6d596e321d81eD895ad51fE30B84) [risc0/KailuaGame] | |
| +++ description: Implementation of the KailuaGame with type 1337. Based on this implementation, new KailuaGames are created with every new state root proposal. | |
2026 April 28, 15:42 UTC2changesSequencer-side Safe ( eth:0x63eCafD2... ) gained one new signer ( 0x12130aF2 ). Threshold unchanged at 1; total signers 3 → 4 (1-of-3 → 1-of-4 — note this weakens the threshold ratio: any one of 4 can still execute).
Sequencer-side Safe (eth:0x63eCafD2...) gained one new signer (0x12130aF2). Threshold unchanged at 1; total signers 3 → 4 (1-of-3 → 1-of-4 — note this weakens the threshold ratio: any one of 4 can still execute).
| contract Safe (eth:0x63eCafD27E0B86B37903c8aA64beD47244Ad909A) { | |
| +++ description: None | |
| values.$members.0: | |
| + | "eth:0x12130aF2fd6E23Cb4EFD396146bE064e893Fc694" |
| values.multisigThreshold: | |
| - | "1 of 3 (33%)" |
| + | "1 of 4 (25%)" |
| } | |
2026 April 03, 10:27 UTC2changesEigenDAOperationsMultisig member removed (0x4985...), threshold unchanged at 3, now 3-of-4 (75%) instead of 3-of-5 (60%). Shared contract with eigenda/syndicate.
EigenDAOperationsMultisig member removed (0x4985…), threshold unchanged at 3, now 3-of-4 (75%) instead of 3-of-5 (60%). Shared contract with eigenda/syndicate.
| contract EigenDAOperationsMultisig (eth:0x002721B4790d97dC140a049936aA710152Ba92D5) { | |
| +++ description: None | |
| values.$members.1: | |
| - | "eth:0x4985238672d91Baed43dF1B2431F67bc332A1753" |
| values.multisigThreshold: | |
| - | "3 of 5 (60%)" |
| + | "3 of 4 (75%)" |
| } | |
The system has a centralized operator
The operatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades. is the only entity that can propose blocksAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over.. A live and trustworthy operator is vital to the health of the system.
MEV can be extracted if the operator exploits their centralized position and frontruns user transactions.
Users can force any transaction
Because the state of the system is based on transactions submitted on the underlying host chain and anyone can submit their transactions there it allows the users to circumvent censorship by interacting with the smart contract on the host chain directly.
Regular exits
The user initiates the withdrawal by submitting a regular transaction on this chain. When a state rootA cryptographic hash succinctly representing a state using a Merkle tree. containing such transaction is settled, the funds become available for withdrawal on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. after 3d 12h. Withdrawal inclusion can be proven before state root settlementThe mechanism with which the execution of rollup blocks and the resultant state is verified and possible disputes are resolved. In the context of rollups or other modular blockchains, it often refers to the proof system used--validity (ZK) or fraud proofs, or a combination thereof. Sometimes it will refer to this mechanism along with where the mechanism's outputs are ultimately published and verified, as in Ethereum being a settlement layer by verifying the proofs and allowing for withdrawals., but a 7d period has to pass before it becomes actionable. The process of state root settlement takes a challenge periodIn optimistic rollups, the window of time wherein network participants can assert that some fraud was included in a prior block. Most optimistic rollups currently specify a challenge window of 7 days. By extending the period, there is more time for participants to guard against fraud (invalid state transitions), but also more time until withdrawals gets enabled. of at least 7d to complete. Finally the user submits an L1 transaction to claim the funds. This transaction requires a merkle proof.
Forced messaging
If the user experiences censorship from the operatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades. with regular L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups.->L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. messaging they can submit their messages directly on L1. The system is then obliged to service this request or halt all messages, including forced withdrawals from L1 and regular messages initiated on L2. Once the force operation is submitted and if the request is serviced, the operation follows the flow of a regular message.
EVM compatible smart contracts are supported
OP stack chains are pursuing the EVM EquivalenceA perfect degree of compatibility; where one system or concept is indistinguishable from another in the domain being compared. In the context of rollups, it generally refers to the proximity to the EVM and to Ethereum architecture. model. No changes to smart contracts are required regardless of the language they are written in, i.e. anything deployed on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. can be deployed on L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups..
Ethereum
Actors:
A Multisig with 2/4 threshold.
- Can upgrade with no delay
- StakeRegistry ProxyAdmin
- BLSApkRegistry ProxyAdmin
- RegistryCoordinator ProxyAdmin
- EjectionManager ProxyAdmin
- SocketRegistry ProxyAdmin
- EigenDADisperserRegistry ProxyAdmin
- EigenDAServiceManager ProxyAdmin
- PaymentVault ProxyAdmin
- IndexRegistry ProxyAdmin
- EigenDARelayRegistry ProxyAdmin
- EigenDAThresholdRegistry ProxyAdmin
- Can interact with RegistryCoordinator
- can add and remove strategies
- Can interact with EigenDAServiceManager
- can transfer ownership of the contract, update the metadata URI, set reward initiator and set batch confirmer
A Multisig with 6/10 threshold.
- Can upgrade with no delay
- BunnyInbox
- L1StandardBridge ProxyAdmin
- SystemConfig ProxyAdmin
- L1ERC721Bridge ProxyAdmin
- SuperchainConfig ProxyAdmin
- L1CrossDomainMessenger ProxyAdmin
- OptimismPortal2 ProxyAdmin
- DisputeGameFactory ProxyAdmin
- DelayedWETH ProxyAdmin
- AnchorStateRegistry ProxyAdmin
- OptimismMintableERC20Factory ProxyAdmin
- Can interact with SystemConfig
- it can update the preconfer address, the batch submitter (SequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs.) address and the gasA virtual fuel used to execute smart contracts on a rollup. The EVM (or other VM within the rollup) uses an accounting mechanism to correspond the consumption of gas to the consumption of computing resources, and to limit the consumption of computing resources. configuration of the system
- Can interact with DelayedWETH
- can pull funds from the contract in case of emergency
- Can interact with AddressManager
- set and change address mappings ProxyAdmin
A Multisig with 3/4 threshold.
- Can interact with EigenDAServiceManager
- can create rewards submissions
A Multisig with 3/8 threshold.
- Can interact with EjectionManager
- can eject DA operators from a quorum
Participants (8):
0x9308…a1250x5262…0aDA0x9951…683F0xA383…350A0x44aC…B9040x3C20…63e90xA4f7…dD310x542a…Bd7EA Multisig with 4/6 threshold.
- Can interact with MegaPreDepositVaultRefund
- manage all access control roles
- service (execute) refunds from this contract
A Multisig with 1/5 threshold. Member of Safe.
A Multisig with 4/6 threshold.
A Multisig with 1/2 threshold.
A Multisig with 1/7 threshold.
- Can interact with SystemConfig
- Allowed to commit transactions from the current layer to the host chain
- Can interact with EigenDAServiceManager
- can confirm batches to the DA bridgeSystem that verifies that data has been made available. It takes the form of a smart contract verifying a consensus or, if the data is verified directly by either downloading the full data or sampling, of an enshrined bridge.
- Can interact with RegistryCoordinator
- can approve the replacement of churned operators from a quorum
- Can interact with EigenDARelayRegistry
- Can store and serve both unencoded blobsThe data that a rollup publishes to its L1/data availability (DA) layer. They consist of the L2 transactions that are rolled up, along with some metadata. Blobs are introduced as a new transaction type within Ethereum with EIP-4844, and has rollup scaling specifically in mind. Blobs persist on Ethereum’s Beacon Chain ephemerally. as well as encoded chunks
- Can interact with EigenDADisperserRegistry
- Can disperse EigenDA blobsThe data that a rollup publishes to its L1/data availability (DA) layer. They consist of the L2 transactions that are rolled up, along with some metadata. Blobs are introduced as a new transaction type within Ethereum with EIP-4844, and has rollup scaling specifically in mind. Blobs persist on Ethereum’s Beacon Chain ephemerally. to the EigenDA nodeA software client that participates in the network. operators
Member of Safe, Safe, Megaeth Multisig, Safe.
- Can interact with SuperchainConfig
- Allowed to pause withdrawals. In op stack systems with a proof systemThe infrastructure that allows projects to verify their state transitions. It is composed by onchain verifiers and offchain provers. The main two flavors are optimistic and ZK proof systems, but they can be combined in a hybrid model. In general though, if a system is able to accept state roots optimistically, even if it has a ZK component, it is considered an optimistic proof system., the Guardian can also blacklist dispute games and set the respected game type (permissioned / permissionlessAnyone willing should be able to join and leave the network at any time, without causing significant disturbance to the network or being detrimental to the party in question. No single entity should have the power to allowlist or blocklist participants.) Safe
- Can interact with RiscZeroVerifierRouter
- add/remove verifiers and the selectors they are mapped to
A Multisig with 3/6 threshold.
- Can upgrade with 10d delay
- AVSDirectory TimelockControllerOwning with 10d delay → EigenLayerOwningMultisig → EigenLayerProxyAdmin
- DelegationManager TimelockControllerOwning with 10d delay → EigenLayerOwningMultisig → EigenLayerProxyAdmin
- Can interact with EigenDAServiceManager
- can pause the DA bridgeSystem that verifies that data has been made available. It takes the form of a smart contract verifying a consensus or, if the data is verified directly by either downloading the full data or sampling, of an enshrined bridge. with no delay or with 10d delay PauserRegistry - or TimelockControllerOwning with 10d delay → EigenLayerOwningMultisig → PauserRegistry
Ethereum
Entrypoint for state rootA cryptographic hash succinctly representing a state using a Merkle tree. proposals. Manages bonds (currently 0.00001 ETH) and tournaments for the OP Kailua state validation system, wrapping the OP stack native DisputeGameFactory.
Onchain EigenDA certificate verification inbox. Receives batch data, strips 4-byte prefix, RLP-decodes EigenDACertV3 and calls the EigenDACertVerifier to validate the certificate. Used as the batch inbox for EigenDA-based data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium..
- Roles:
- admin: Safe
Contains configuration parameters such as the SequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. address, gas limitThe maximum amount of gas a transaction or block may consume. on this chain and the unsafe blockAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over. signer address.
- Roles:
- admin: ProxyAdmin; ultimately Safe
- batcherHash: EOA 1
- owner: Safe
VerifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. contract for RISC Zero Groth16A zk-SNARK proving system introduced by Groth in 2016 that proves arithmetic circuits and requires a separate trusted setup for each circuit. It allows extremely efficient proof verification. proofs (version 2.0.0-rc.3).
The OptimismPortal contract is the main entry point to deposit funds from L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. to L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups.. It also allows to prove and finalize withdrawals. It specifies which game type can be used for withdrawals, which currently is the KailuaGame.
- Roles:
- admin: ProxyAdmin; ultimately Safe
The dispute game factory allows the creation of dispute games, used to propose state rootsA cryptographic hash succinctly representing a state using a Merkle tree. and eventually challenge them.
- Roles:
- admin: ProxyAdmin; ultimately Safe
Keeps track of the total stake of each operatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades..
- Roles:
- admin: ProxyAdmin; ultimately EigenDAOperationsMultisig
Keeps track of the BLS public keys of each operatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades. and the quorum aggregated keys.
- Roles:
- admin: ProxyAdmin; ultimately EigenDAOperationsMultisig
Operators register here with an AVS The coordinator has three registries 1) a StakeRegistry that keeps track of operators’ stakes, 2) a BLSApkRegistry that keeps track of operators’ BLS public keys and aggregate BLS public keys for each quorum, 3) an IndexRegistry that keeps track of an ordered list of operators for each quorum.
- Roles:
- admin: ProxyAdmin; ultimately EigenDAOperationsMultisig
- churnApprover: EOA 7
- owner: EigenDAOperationsMultisig
Defines and stores pauser and unpauser roles for EigenDA contracts.
- Roles:
- pausers: EigenLayerOperationsMultisig, EigenLayerOwningMultisig, EigenLayerPauserMultisig
Contract used for ejection of operators from the RegistryCoordinator for violating the Service Legal Agreement (SLA).
- Roles:
- admin: ProxyAdmin; ultimately EigenDAOperationsMultisig
- ejectors: EOA 4, EOA 6, EigenDA Multisig
- Roles:
- admin: ProxyAdmin; ultimately EigenDAOperationsMultisig
Registry for EigenDA disperser info such as disperser key to address mapping.
- Roles:
- admin: ProxyAdmin; ultimately EigenDAOperationsMultisig
- dispersers: EOA 9
BridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. contract that accepts blobThe data that a rollup publishes to its L1/data availability (DA) layer. They consist of the L2 transactions that are rolled up, along with some metadata. Blobs are introduced as a new transaction type within Ethereum with EIP-4844, and has rollup scaling specifically in mind. Blobs persist on Ethereum’s Beacon Chain ephemerally. batches data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium. attestations. Batches availability is attested by EigenDA operators signatures and relayed to the service manager contract by the EigenDA disperser.
- Roles:
- admin: ProxyAdmin; ultimately EigenDAOperationsMultisig
- batchConfirmers: EOA 2, EOA 3, EOA 5
- owner: EigenDAOperationsMultisig
- pauserRegistry: PauserRegistry; ultimately EOA 11, EOA 12, EOA 13, EOA 14, EOA 15, EOA 16, EigenLayerCommunityMultisig, EigenLayerOperationsMultisig, EigenLayerOperationsMultisig2, Safe
- rewardsInitiator: EigenLayerRewardsInitiatorMultisig
Entrypoint for making reservations and on demand payments for EigenDA.
- Roles:
- admin: ProxyAdmin; ultimately EigenDAOperationsMultisig
A registry contract that keeps track of an ordered list of operators for each quorum.
- Roles:
- admin: ProxyAdmin; ultimately EigenDAOperationsMultisig
Registry for EigenDA relay keys, maps key to address.
- Roles:
- admin: ProxyAdmin; ultimately EigenDAOperationsMultisig
- relayers: EOA 8
Registry of EigenDA threshold (i.e, adversary and confirmation threshold percentage for a quorum)
- Roles:
- admin: ProxyAdmin; ultimately EigenDAOperationsMultisig
- Roles:
- admin: EigenLayerProxyAdmin; ultimately EigenLayerCommunityMultisig, EigenLayerOperationsMultisig, EigenLayerOperationsMultisig2
The DelegationManager contract is responsible for registering EigenLayer operators and managing the EigenLayer strategies delegations. The EigenDA StakeRegistry contract reads from the DelegationManager to track the total stake of each EigenDA operatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades..
- Roles:
- admin: EigenLayerProxyAdmin; ultimately EigenLayerCommunityMultisig, EigenLayerOperationsMultisig, EigenLayerOperationsMultisig2
This is NOT the shared SuperchainConfig contract of the OP stack Superchain but rather a local fork. It manages the PAUSED_SLOT, a boolean value indicating whether the local chain is paused, and GUARDIAN_SLOT, the address of the guardian which can pause and unpause the system.
- Roles:
- admin: ProxyAdmin; ultimately Safe
- guardian: Safe; ultimately EOA 10
The main entry point to deposit ERC20 tokens from host chain to this chain.
- Roles:
- admin: ProxyAdmin; ultimately Safe
All supported tokens in this escrow are included in the value secured calculation.
Used to bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. ERC-721 tokens from host chain to this chain.
- Roles:
- admin: ProxyAdmin; ultimately Safe
Sends messages from host chain to this chain, and relays messages back onto host chain. In the event that a message sent from host chain to this chain is rejected for exceeding this chain’s epoch gas limitThe maximum amount of gas a transaction or block may consume., it can be resubmitted via this contract’s replay function.
- Roles:
- admin: ProxyAdmin; ultimately Safe
Refund escrow designed to hold the funds extracted from the predeposit vault and send them back to the users listed in the vault.
- Roles:
- defaultAdmin: Safe
- executor: Safe
Predeposit Escrow, not connected to an L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups.: Users can deposit USDC. The system uses off-chain permit signatures to ensure only KYC’d users can deposit. Withdrawals can only be made by Megaeth Multisig to MegaPreDepositVaultRefund.
- Roles:
- owner: Megaeth Multisig
- permitSigner: EOA 17
- Roles:
- owner: Safe
The PreimageOracle contract is used to load the required data from L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. for a dispute game.
Contract designed to hold the bonded ETH for each game. It is designed as a wrapper around WETH to allow an owner to function as a backstop if a game would incorrectly distribute funds.
- Roles:
- admin: ProxyAdmin; ultimately Safe
- owner: Safe
Implementation of the KailuaGame with type 1337. Based on this implementation, new KailuaGames are created with every new state rootA cryptographic hash succinctly representing a state using a Merkle tree. proposal.
A router proxy that routes to verifiers based on selectors. The mapping can be changed by a permissioned owner (0x0A383fF8387CF07315f476D1686E95b1a97adc97).
- Roles:
- owner: EOA 10
A DA verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. contract for EigenDA V2 certificates. The verifier is used to verify the certificate against operatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades. signatures and stake thresholds.
Same as FaultDisputeGame, but only two permissioned addresses are designated as proposerIn the context of L2s, the actor that proposes a claimed state root on L1. The term is also used in the context of Ethereum to refer to the actor that proposes a new block. and challenger.
Contains the latest confirmed state rootA cryptographic hash succinctly representing a state using a Merkle tree. that can be used as a starting point in a dispute game.
- Roles:
- admin: ProxyAdmin; ultimately Safe
The MIPS contract is used to execute the final step of the dispute game which objectively determines the winner of the dispute.
A helper contract that generates OptimismMintableERC20 contracts on the networkA constellation of nodes (peers) that communicate via a peer-to-peer protocol, for example, in propagating transactions and blocks to other nodes. it’s deployed to. OptimismMintableERC20 is a standard extension of the base ERC20 token contract designed to allow the L1StandardBridge contracts to mint and burn tokens. This makes it possible to use an OptimismMintableERC20 as this chain’s representation of a token on the host chain, or vice-versa.
- Roles:
- admin: ProxyAdmin; ultimately Safe
Multisig currently designated as the ‘Treasury’.
The current deployment carries some associated risks:
Funds can be stolen if a contract receives a malicious code upgrade. There is no delay on code upgrades (CRITICAL).