Search
Search for projects by name or address
 Sorare
 froze its StarkEx rollupA blockchain that inherits consensus and data availability from another blockchain called L1. Rollups enable trust minimized bridges with the base layer via proof systems, either optimistic or zero-knowledge. A rollup without a bridge, or without considering the bridge, is called a sovereign rollup. on June 1st, 2026. The core rollup contract is currently frozen.
Critical contracts can be upgraded by an EOA which could result in the loss of all funds.
Badges
About
Sorare is a global fantasy football game where you can play with officially licensed digital cards.
- Compromising ≥75% of the Security Council to push a malicious upgrade, or sequencer+DA-committee collusion to withhold data and finalize invalid state roots, should be the only ways (other than bugs) to steal funds or block withdrawals indefinitely.
Badges
About
Sorare is a global fantasy football game where you can play with officially licensed digital cards.
Sorare StarkEx deprecation
2026 Jun 1st
Sorare finalizes its migration to Solana by sunsetting its StarkEx L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. contract.
Mainnet Launch
2021 Jul 26th
Layer 2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. scaling solution powered by Starkware, is live on Ethereum.
Funds can be stolen if
Funds can be lost if
Users can be censored if
MEV can be extracted if
Users can force the sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. to include a transaction by submitting a request through L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development.. If the sequencer censors or is down for for more than 7d, users can use the exit hatch to withdraw their funds.
STARKs are zero knowledge proofs that ensure state correctness.
Proof construction relies fully on data that is NOT published onchain. There exists a Data Availability Committee (DAC)A set of members whose task is attesting and ensuring that the data is available for the public. An onchain DAC verifier checks that a threshold of signatures from the DAC members is reached before considering a data commitment as available and therefore valid to be used in the system. with a threshold of 2/4 that is tasked with protecting and supplying the data.
There is no window for users to exit in case of an unwanted upgrade since contracts are instantly upgradable.
Users are able to trustlessly exit by submitting a Merkle proof of funds. NFTs will be minted on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. to exit.
Set of parties responsible for signing and attesting to the availability of data.
There are no onchain assets at risk of being slashed in case of a data withholding attack, and the committee members are not publicly known.
There is no fraud detection mechanism in place. A data withholding attack can only be detected by nodes downloading the full data from the DA layerAn infrastructure that is used to make publish data so that it's available to the public. They take the form of Data Availability Committees (DACs) or blockchains. Not to confuse with the layer responsible with ordering, since ordering and DA can be separated..
The committee does not meet basic security standards, either due to insufficient size, lack of member diversity, or poorly defined threshold parameters. The system lacks an effective DA bridgeSystem that verifies that data has been made available. It takes the form of a smart contract verifying a consensus or, if the data is verified directly by either downloading the full data or sampling, of an enshrined bridge. and it is reliant on the assumption of an honest sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs., creating significant risks to data integrity and availability.
The bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. smart contract is immutable and cannot be updated. The bridge committee security is low and cannot be improved.
Anyone can relay data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium. commitments to the DA bridgeSystem that verifies that data has been made available. It takes the form of a smart contract verifying a consensus or, if the data is verified directly by either downloading the full data or sampling, of an enshrined bridge.. In case of current relayer failure, users can collect attestations from committee members and propose new data availability commitments to the DA bridge.
Architecture
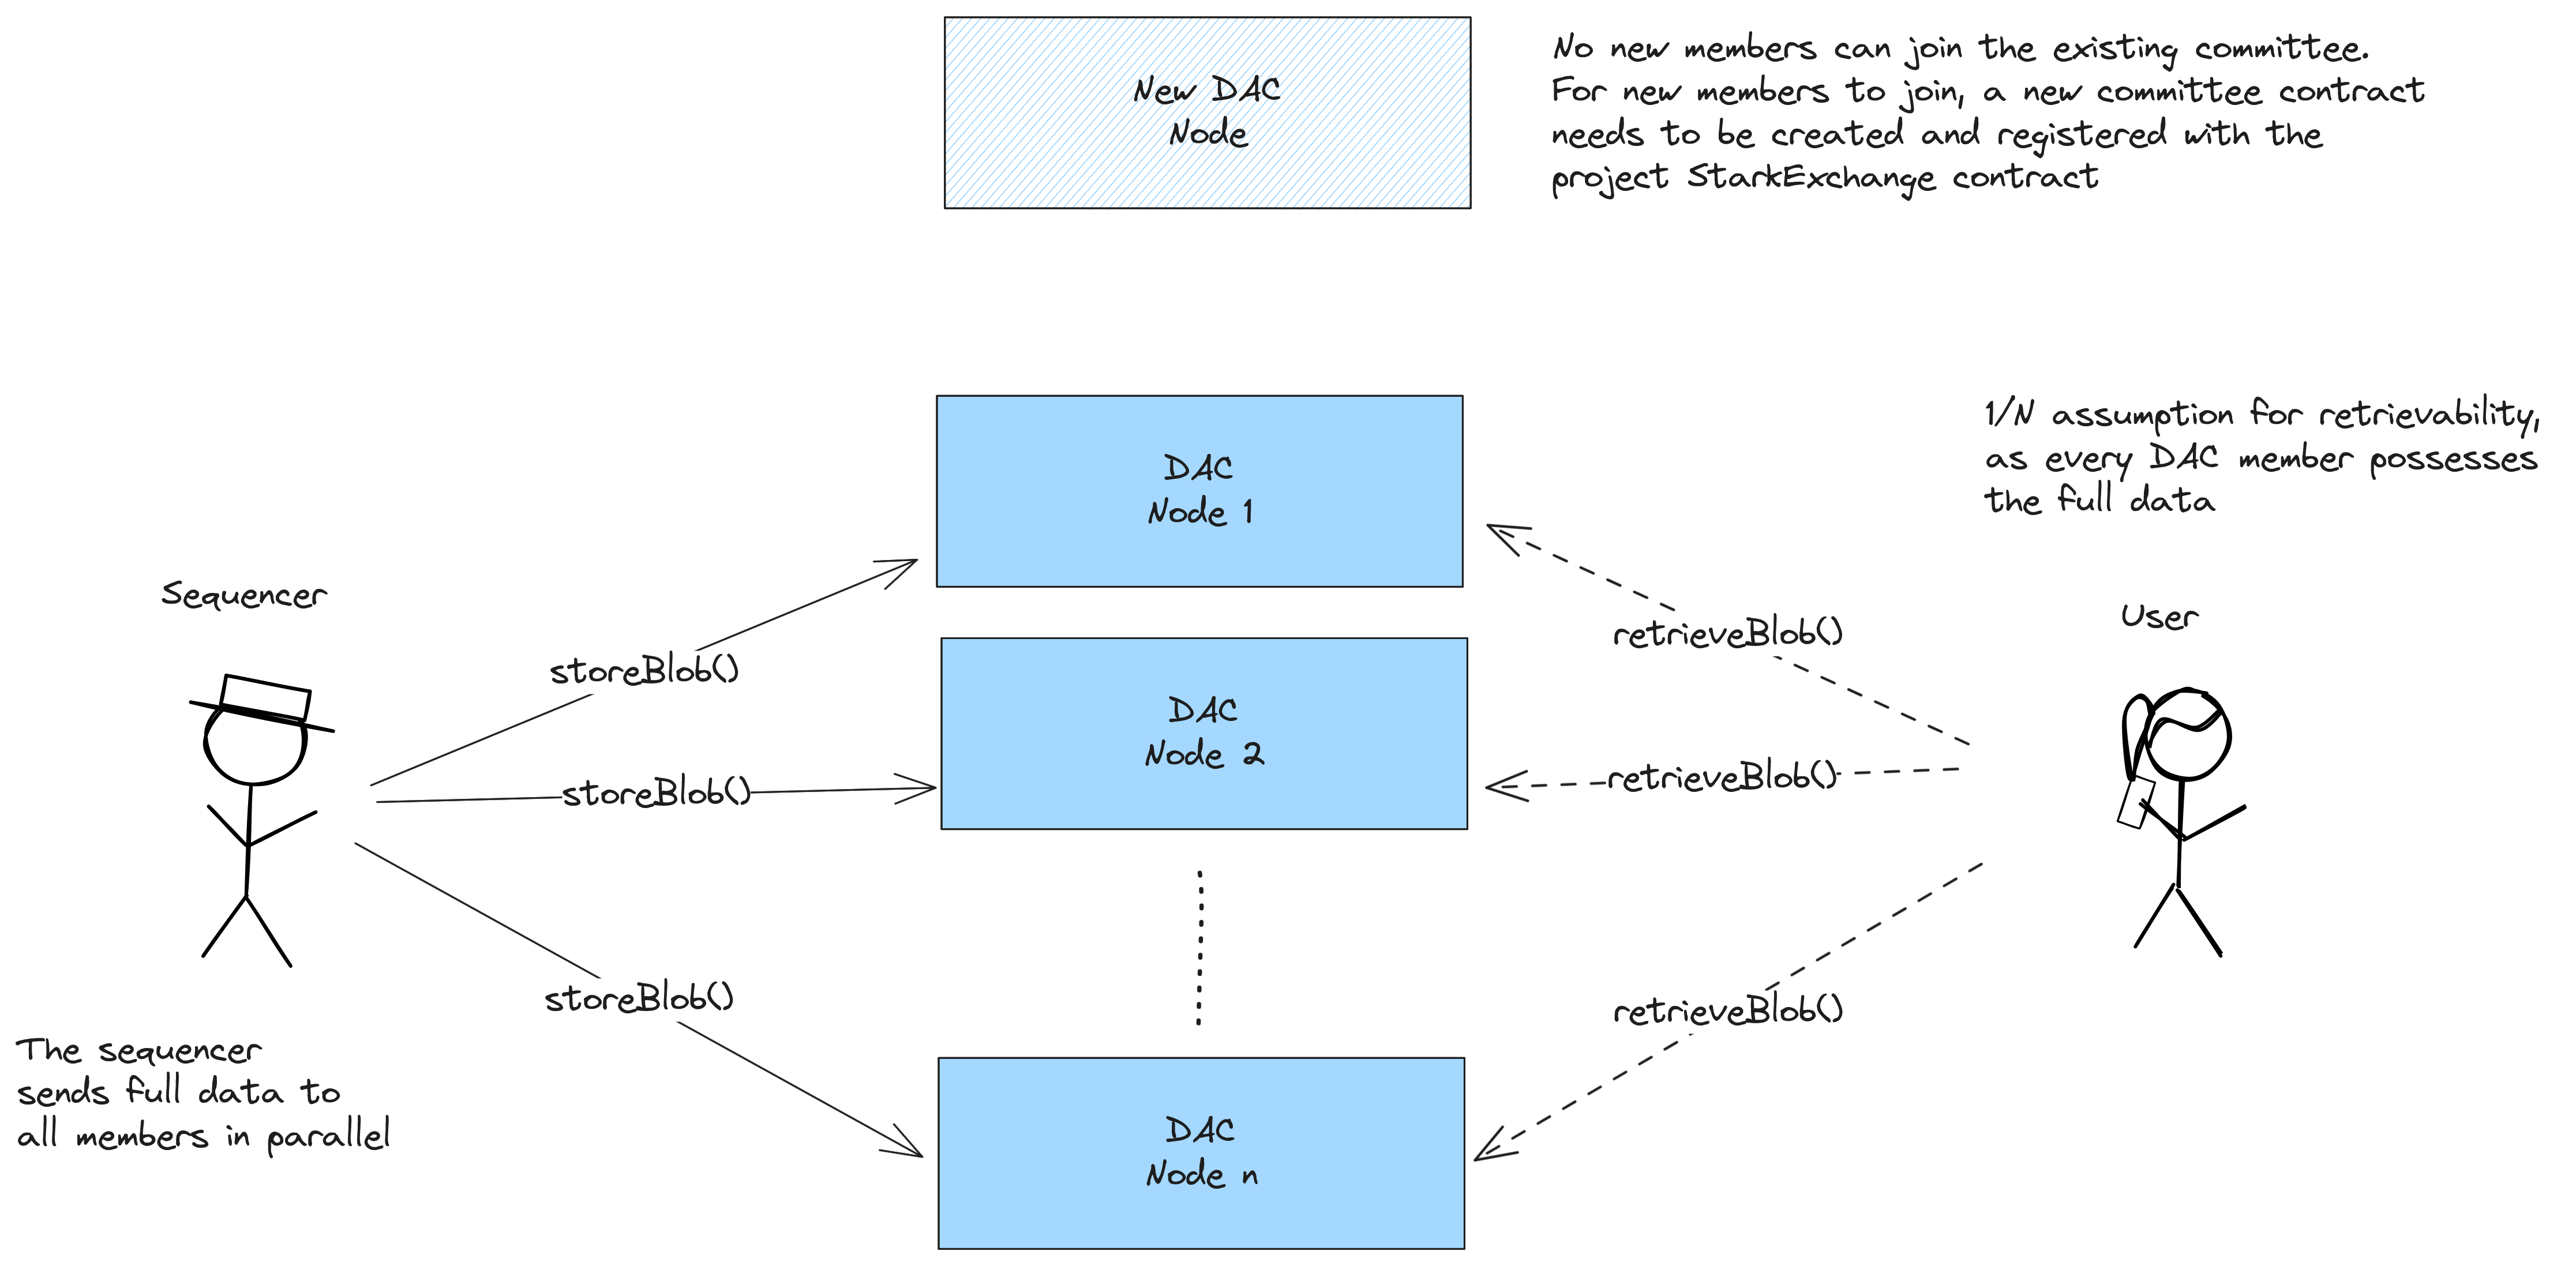
The Starkware application utilizes a data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium. solution that relies on a Committee Service to ensure data persistence. This architecture comprises the following components:
- Availability Gateway: The primary interface provided by the operatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades. for committee members to access new batch information and submit signed availability claims.
- Data Availability Committee (DAC)A set of members whose task is attesting and ensuring that the data is available for the public. An onchain DAC verifier checks that a threshold of signatures from the DAC members is reached before considering a data commitment as available and therefore valid to be used in the system.: A group of nodes responsible for storing state data associated with each Merkle root and attesting to data availability by signing claims.
- Data Batches: Collections of transactions processed in batches that update the state of accounts, resulting in a new Merkle root representing the updated state.
Committee members run services that interact with the Availability Gateway to obtain information about new batches and submit their signed availability claims. Each batch includes a unique batch_id, a reference to a previous batch, and a list of account updates. Committee members combine this information with data from the reference batch to compute the new state and verify the Merkle root.
When the operator produces a new batch, it must be signed by a minimum number of committee members—as defined by the application’s configuration—for it to be accepted onchain. This includes all members designated as mandatory signers. If the operator attempts to submit a batch without the required signatures, it will be rejected, thereby ensuring that data remains available and consistent.
Committee members are expected to maintain a database that stores the data associated with each batch, making use of storage solutions with a replication factor of at least 2.
DA BridgeSystem that verifies that data has been made available. It takes the form of a smart contract verifying a consensus or, if the data is verified directly by either downloading the full data or sampling, of an enshrined bridge. Architecture
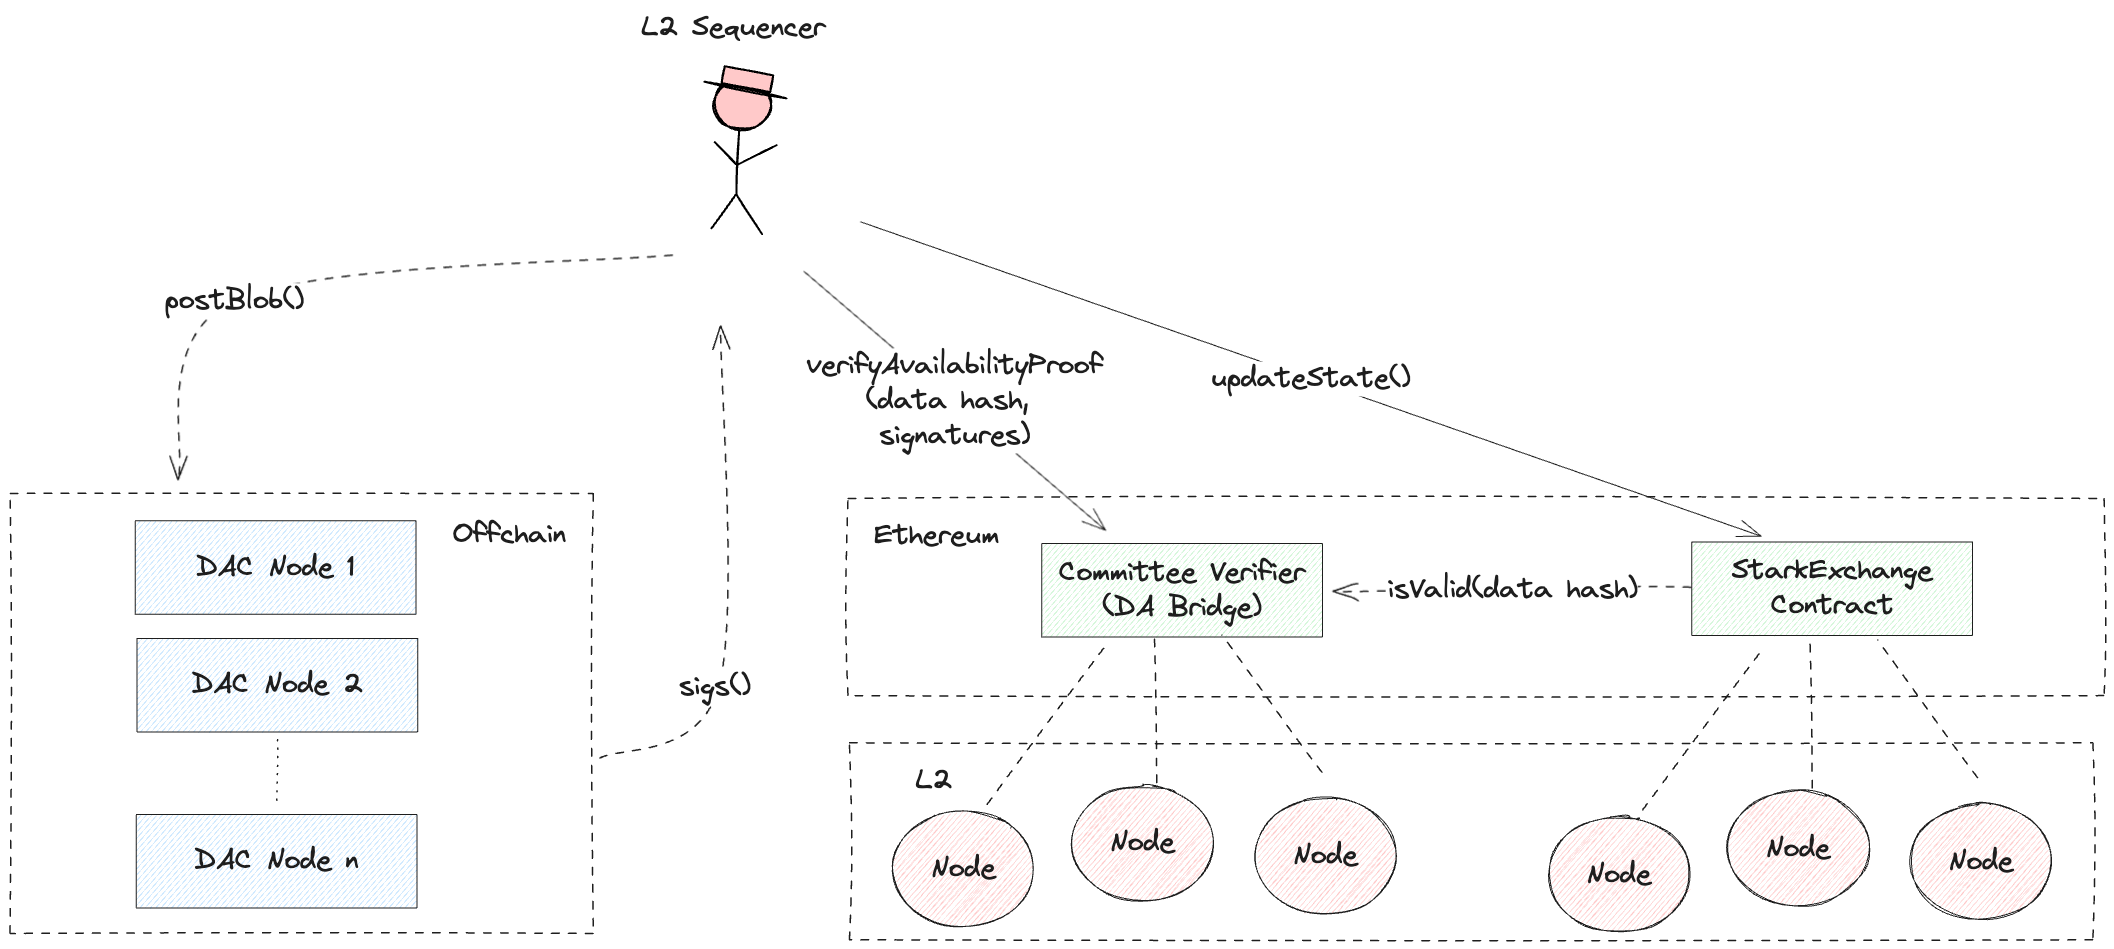
The DA commitments are posted to the destination chain, using the Committee VerifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. contract as a DA bridge. The DA commitment consists of a data hashA fixed-length fingerprint of variable-size input, produced by a hash function. of the transaction batch the Committee has signed off on and a concatenation of ec-signatures by signatories.
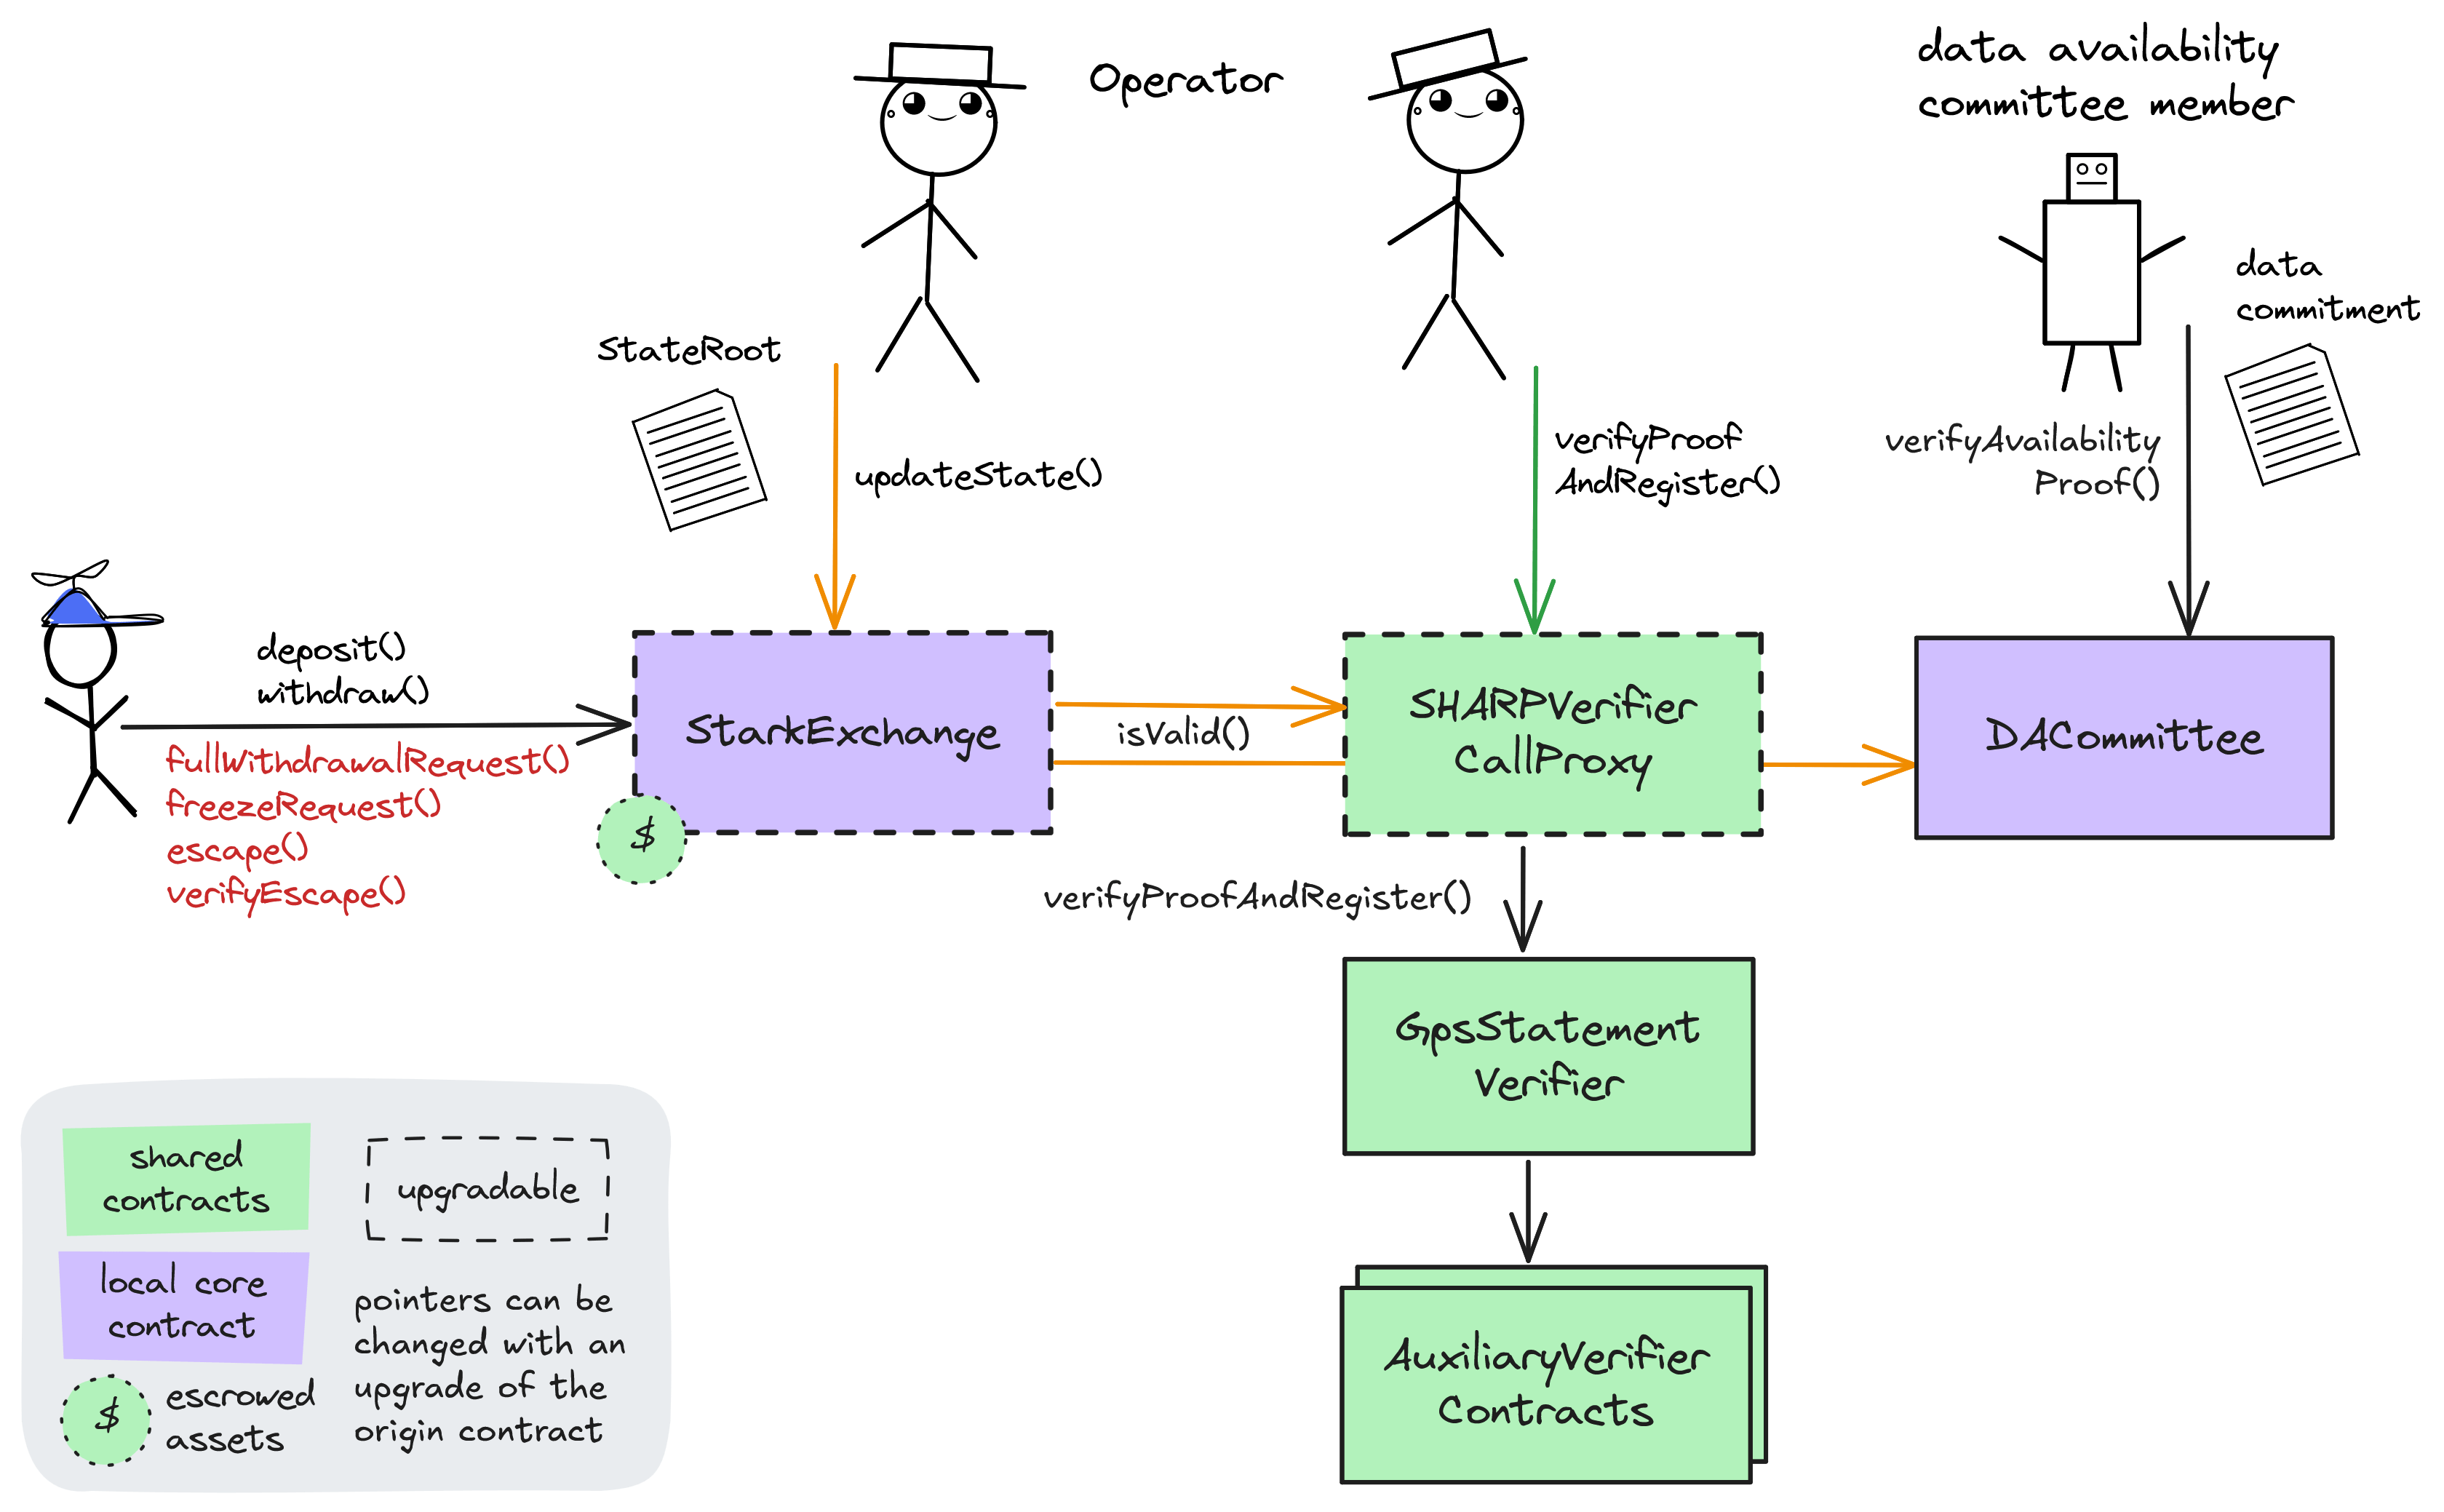
The Committee Verifier contract verifies the signatures and the data hash and if the required threshold of Committee members has signed off on the data, the hash is stored as a registeredFact in the StarkEx contract. In a separate transaction, the operator calls the updateState() function on the StarkEx contract to update the state. Before the state updateA mechanism that allows to update the claimed state of a project. It usually involves verifying a state transition proof, but it can also be done in a trusted manner by a permissioned actor. is accepted, the StarkEx contract verifies the transaction public inputs by calling the isValid() function, which verifies the hash derived from state update inputs matches the hash stored by the Committee Verifier contract.
Funds can be lost if a malicious committee signs a data availability attestation for an unavailable transaction batch.
Each update to the system state must be accompanied by a ZK proof that ensures that the new state was derived by correctly applying a series of valid user transactions to the previous state. These proofs are then verified on Ethereum by a smart contract. The system state is represented using Merkle roots.

Program Hashes
Name | Hash | Repository | Verification | Used in | |||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
317490...6957 | Code unknown | None | | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
342795...2024 |     Projects used inSearch for projects used in | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
344285...1079 | Projects used inSearch for projects used in | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
235884...3330 | Projects used inSearch for projects used in | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
254986...4351 | Projects used inSearch for projects used in | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
Past upgrades
The metrics include upgrades on the currently used proxy contracts. Historical proxy contracts and changes of such are not included.
2026 June 05, 07:57 UTC16changesFroze Sorare rollup contract. Upgraded Sorare diamond facets. Verifiers facet: https://disco.l2beat.com/diff/eth:0xfbea22FeB369DB10C0d3a2aAa8F4939E76815f12/eth:0xA67821bC089B4374e8D62475526E7e84f09Da086: - Refactored governance - Reduced UNFREEZE DELAY (the time after which the rollup may be unfrozen after it froze) from 1 year to 1 day - Added adminFreeze 9994 function that allows governor to freeze the rollup TokensAndRamping facet: https://disco.l2beat.com/diff/eth:0x2Dbc18A3ac126abE1fF90A83Bbc3947ff7912Afb/eth:0xb97394B55b4807a835619EDbCC6aF6b1d3C71e98: - Added support for mintable ERC 1155 - Added withdrawWithFee 10 function that allows withdrawing ETH even when rollup is frozen. User authorizes a withdrawal with a signature passed in calldata, and pays a withdrawal fee. - Added withdrawWithFeeToBaseBank function that allows withdrawing ETH directly to Base L2, otherwise works similarly to the previous function.
Froze Sorare rollup contract.
Upgraded Sorare diamond facets.
Verifiers facet: https://disco.l2beat.com/diff/eth:0xfbea22FeB369DB10C0d3a2aAa8F4939E76815f12/eth:0xA67821bC089B4374e8D62475526E7e84f09Da086:
- Refactored governance
- Reduced
UNFREEZE_DELAY(the time after which the rollup may be unfrozen after it froze) from 1 year to 1 day - Added
adminFreeze_9994function that allows governor to freeze the rollup
TokensAndRamping facet: https://disco.l2beat.com/diff/eth:0x2Dbc18A3ac126abE1fF90A83Bbc3947ff7912Afb/eth:0xb97394B55b4807a835619EDbCC6aF6b1d3C71e98:
- Added support for mintable ERC 1155
- Added
withdrawWithFee_10function that allows withdrawing ETH even when rollup is frozen. User authorizes a withdrawal with a signature passed in calldata, and pays a withdrawal fee. - Added
withdrawWithFeeToBaseBankfunction that allows withdrawing ETH directly to Base L2, otherwise works similarly to the previous function.
| - | Status: DELETED |
| contract OrderRegistry (eth:0x518c4A79a1102eEDc987005CA8cE6B87Ca14dDf8) [starkex/OrderRegistry] | |
| +++ description: Helper contract for registering limit orders from L1. | |
| contract StarkExchange (eth:0xF5C9F957705bea56a7e806943f98F7777B995826) [starkex/StarkExchange_Frozen] { | |
| +++ description: Central Validium contract. Receives (verified) state roots from the Operator, allows users to consume L2 -> L1 messages and send L1 -> L2 messages. Critical configuration values for the L2's logic are defined here by various governance roles. | |
| template: | |
| - | "starkex/StarkExchange" |
| + | "starkex/StarkExchange_Frozen" |
| sourceHashes.1: | |
| - | "0x9b28596a715350d61f719241f35d6ee159c111c93c05da1d4804157142ee790c" |
| + | "0x0843c70dcca99b2fde3a18013b0af9af358e90066af9d8a2d3754785eb0ff2a0" |
| values.$implementation.1: | |
| - | "eth:0xfbea22FeB369DB10C0d3a2aAa8F4939E76815f12" |
| + | "eth:0xA67821bC089B4374e8D62475526E7e84f09Da086" |
| values.$implementation.2: | |
| - | "eth:0x2Dbc18A3ac126abE1fF90A83Bbc3947ff7912Afb" |
| + | "eth:0xb97394B55b4807a835619EDbCC6aF6b1d3C71e98" |
| values.$pastUpgrades.12: | |
| + | ["2026-05-31T10:22:59.000Z","0xfd3455fd60677c360679dc601a13283ad26f7f618c9c67db9a52b9d7d42d5014",["eth:0xdF2f24751F7e84ccDCD39e7b49904FAB0Fb0f583","eth:0xA67821bC089B4374e8D62475526E7e84f09Da086","eth:0xb97394B55b4807a835619EDbCC6aF6b1d3C71e98","eth:0x67e198743BC19fa4757720eDd0e769f8291e1F1D","eth:0x613ee54C54D5548627064B4D648942bF3648f376","eth:0xb2ED005D0278179001a49a9969BB22BA8e98f31F","eth:0xB5353268d8d4D711a92cb838F8fEDFC2A66E50Db"]] |
| values.$upgradeCount: | |
| - | 12 |
| + | 13 |
| values.defaultVaultWithdrawalLock: | |
| - | 0 |
| values.isFrozen: | |
| - | false |
| + | true |
| values.orderRegistryAddress: | |
| - | "eth:0x518c4A79a1102eEDc987005CA8cE6B87Ca14dDf8" |
| values.tokenAdmins: | |
| - | ["eth:0xA5dAd8339d9279c2F16d02F2e903AB4B79a72815","eth:0x7F6d06eCd94bD899872cd2768e41B7d33EC13e19"] |
| values.UNFREEZE_DELAY: | |
| - | 31536000 |
| + | 3600 |
| implementationNames.eth:0xfbea22FeB369DB10C0d3a2aAa8F4939E76815f12: | |
| - | "AllVerifiers" |
| implementationNames.eth:0x2Dbc18A3ac126abE1fF90A83Bbc3947ff7912Afb: | |
| - | "TokensAndRamping" |
| implementationNames.eth:0xA67821bC089B4374e8D62475526E7e84f09Da086: | |
| + | "AllVerifiers" |
| implementationNames.eth:0xb97394B55b4807a835619EDbCC6aF6b1d3C71e98: | |
| + | "TokensAndRamping" |
| } | |
2026 May 04, 10:45 UTC1changeVerifier upgrade finalized, it is now actively used.
Verifier upgrade finalized, it is now actively used.
| contract GpsFactRegistryAdapter (eth:0xbcc17446B99465fF01E6816d9bcb2d8b1D7cEdB1) { | |
| +++ description: Adapter between the core contract and the eth:0x47312450B3Ac8b5b8e247a6bB6d523e7605bDb60. Stores the Cairo programHash (`3174901404014912024702042974619036870715605532092680335571201877913899936957`). | |
| values.hasRegisteredFact: | |
| - | false |
| + | true |
| } | |
2026 April 30, 10:53 UTC7changesReduced upgrade delay to zero. Verifier automatically changed hasRegisteredFact flag, indicating that verifier upgrade is not finalized yet.
Reduced upgrade delay to zero. Verifier automatically changed hasRegisteredFact flag, indicating that verifier upgrade is not finalized yet.
| EOA (eth:0x5918481F777dBe437De249492B90AffB4e655de4) { | |
| +++ description: None | |
| receivedPermissions.2.delay: | |
| - | 1209600 |
| } | |
| contract GpsFactRegistryAdapter (eth:0xbcc17446B99465fF01E6816d9bcb2d8b1D7cEdB1) { | |
| +++ description: Adapter between the core contract and the eth:0x47312450B3Ac8b5b8e247a6bB6d523e7605bDb60. Stores the Cairo programHash (`3174901404014912024702042974619036870715605532092680335571201877913899936957`). | |
| values.hasRegisteredFact: | |
| - | true |
| + | false |
| } | |
| contract SorareAdminMultisig (eth:0xCc928977e4a75d25099e7DA7B6Fd79Dac2f9fD2B) { | |
| +++ description: None | |
| receivedPermissions.2.delay: | |
| - | 1209600 |
| } | |
| contract StarkExchange (eth:0xF5C9F957705bea56a7e806943f98F7777B995826) { | |
| +++ description: Central Validium contract. Receives (verified) state roots from the Operator, allows users to consume L2 -> L1 messages and send L1 -> L2 messages. Critical configuration values for the L2's logic are defined here by various governance roles. | |
| values.$pastUpgrades.11: | |
| + | ["2026-04-28T11:42:11.000Z","0x8133c660c29139f3afcfa0d694829a8e16d5473e74704be6b0aa06869cf329d8",["eth:0xdF2f24751F7e84ccDCD39e7b49904FAB0Fb0f583","eth:0xfbea22FeB369DB10C0d3a2aAa8F4939E76815f12","eth:0x2Dbc18A3ac126abE1fF90A83Bbc3947ff7912Afb","eth:0x67e198743BC19fa4757720eDd0e769f8291e1F1D","eth:0x613ee54C54D5548627064B4D648942bF3648f376","eth:0xb2ED005D0278179001a49a9969BB22BA8e98f31F","eth:0xB5353268d8d4D711a92cb838F8fEDFC2A66E50Db"]] |
| values.$upgradeCount: | |
| - | 11 |
| + | 12 |
| values.getUpgradeActivationDelay: | |
| - | 1209600 |
| + | 0 |
| values.StarkWareDiamond_upgradeDelay: | |
| - | 1209600 |
| + | 0 |
| } | |
2025 September 02, 12:41 UTC1changeChanged admin multisig. Added mapping from Starknet.
Changed admin multisig. Added mapping from Starknet.
| contract SorareAdminMultisig (eth:0xCc928977e4a75d25099e7DA7B6Fd79Dac2f9fD2B) { | |
| +++ description: None | |
| values.$members.1: | |
| - | "eth:0xd38831Bcb40bdEE0577Ee064112Fa77a38cAd3F8" |
| + | "eth:0xaDB26E60FA6e326B9Ee444D886B4B62EC7FA38fc" |
| } | |
2025 July 14, 12:46 UTC5changesDiscovery rerun on the same block number with only config-related changes.
Discovery rerun on the same block number with only config-related changes.
New and verified contracts
| + | Status: CREATED |
| contract OrderRegistry (0x518c4A79a1102eEDc987005CA8cE6B87Ca14dDf8) | |
| +++ description: Helper contract for registering limit orders from L1. | |
| + | Status: CREATED |
| contract DACommittee (0x879cD57975d596004863D30c59d579ef78BBbe32) | |
| +++ description: Data Availability Committee (DAC) contract verifying and storing data availability claims from DAC Members (via a multisignature check). The threshold of valid signatures is 2. | |
| + | Status: CREATED |
| contract GpsFactRegistryAdapter (0xbcc17446B99465fF01E6816d9bcb2d8b1D7cEdB1) | |
| +++ description: Adapter between the core contract and the eth:0x47312450B3Ac8b5b8e247a6bB6d523e7605bDb60. Stores the Cairo programHash (`3174901404014912024702042974619036870715605532092680335571201877913899936957`). | |
| + | Status: CREATED |
| contract SorareAdminMultisig (0xCc928977e4a75d25099e7DA7B6Fd79Dac2f9fD2B) | |
| +++ description: None | |
| + | Status: CREATED |
| contract StarkExchange (0xF5C9F957705bea56a7e806943f98F7777B995826) | |
| +++ description: Central Validium contract. Receives (verified) state roots from the Operator, allows users to consume L2 -> L1 messages and send L1 -> L2 messages. Critical configuration values for the L2's logic are defined here by various governance roles. | |
The system has a centralized operator
The operatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades. is the only entity that can propose blocksAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over.. A live and trustworthy operator is vital to the health of the system. Typically, the Operator is the hot wallet of the StarkEx service submitting state updates for which proofs have been already submitted and verified.
MEV can be extracted if the operator exploits their centralized position and frontruns user transactions.
Users can force exit the system
Force exit allows the users to escape censorship by withdrawing their funds. The system allows users to force the withdrawal of funds by submitting a request directly to the contract onchain. The request must be served within a defined time period. If this does not happen, the system will halt regular operation and permit trustless withdrawal of funds.
Users can be censored if the operator refuses to include their transactions. However, there exists a mechanism to independently exit the system.
Regular exit
The user initiates the withdrawal by submitting a regular transaction on this chain. When the blockAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over. containing that transaction is settled the funds become available for withdrawal on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development.. ZK proofs are required to settle blocks. Finally the user submits an L1 transaction to claim the funds. When withdrawing NFTs they are minted on L1.
Forced exit
If the user experiences censorship from the operatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades. with regular exit they can submit their withdrawal requests directly on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development.. The system is then obliged to service this request. Once the force operation is submitted and if the request is serviced, the operation follows the flow of a regular exit.
Emergency exit
If the enough time deadline passes and the forced exit is still ignored the user can put the system into a frozen state, disallowing further state updates. In that case everybody can withdraw by submitting a merkle proof of their funds with their L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. transaction.
Ethereum
Actors:
A Multisig with 2/4 threshold.
- Can upgrade with 8d delay
- SHARPVerifierCallProxy - acting directly with 8d delay
- Can interact with SHARPVerifierCallProxy
- Administer the CallProxy’s
GOVERNANCE_ADMINand role-admin hierarchy. This AccessControl role is separate from the outer proxy governor that schedules implementation upgrades - Grant and revoke application roles, including the
APP_GOVERNORrole that controls caller-specific fallback routes - Route fallback calls from specific callers to a still-active registry in the default verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover.’s reference chain. This principally determines which verifier and bootloader configuration processes their proof submissions; the proxy’s explicit
isValidentry point always queries the default target
- Administer the CallProxy’s
A Multisig with 2/3 threshold.
- Can upgrade with no delay
- StarkExchange
- Can interact with StarkExchange
- manage the token admin role
- Permissioned to appoint and remove the OperatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades., register additional verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. and availability verifier contracts (removals are delayed), set the default vault withdrawal lock, unfreeze the exchange and manage the governor set
- Can upgrade with no delay
- StarkExchange
- Can interact with StarkExchange
- manage the token admin role
- Permissioned to appoint and remove the OperatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades., register additional verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. and availability verifier contracts (removals are delayed), set the default vault withdrawal lock, unfreeze the exchange and manage the governor set
- Can interact with StarkExchange
- Permissioned to regularly update the state rootsA cryptographic hash succinctly representing a state using a Merkle tree. of the L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development.. Each state updateA mechanism that allows to update the claimed state of a project. It usually involves verifying a state transition proof, but it can also be done in a trusted manner by a permissioned actor. must have been proven via the SHARP verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. and contains commitments to the data that is itself kept offchain
Ethereum
Data Availability Committee (DAC)A set of members whose task is attesting and ensuring that the data is available for the public. An onchain DAC verifier checks that a threshold of signatures from the DAC members is reached before considering a data commitment as available and therefore valid to be used in the system. contract verifying and storing data availabilityThe property of a rollup's data being reachable by any node retrieving the data that were rolled up and executed to reach the proposed state. Data availability (DA), specifically decoupling it from the rollup nodes themselves, is one of the preeminent factors which allows a rollup to scale securely. A rollup is faced with a decision of what to use as a DA layer to guarantee that any node can retrieve this data--permissionlessly under any circumstance. For this reason, using Ethereum for DA currently provides the strongest security guarantees. If data is stored somewhere other than a permissionless L1, then the project is not a rollup, but rather a validium or an optimium. claims from DAC Members (via a multisignature check). The threshold of valid signatures is 2.
Central ValidiumAn off-chain solution that uses validity proofs for settlement and publishes the data offchain, therefore requiring an additional trust assumption. contract. Receives (verified) state rootsA cryptographic hash succinctly representing a state using a Merkle tree. from the OperatorAn operator is the entity charged with managing a rollup and progressing its state. A rollup operator can be a centralized sequencer, proposer, prover, challenger, pauser of admin that is able to perform upgrades., allows users to consume L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. -> L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. messages and send L1 -> L2 messages. Critical configuration values for the L2’s logic are defined here by various governance roles.
- Roles:
- admin: EOA 1, SorareAdminMultisig
- operators: EOA 2, EOA 3
Immutable Solidity verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for one Cairo CPU layout. It checks the STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof using layout-specific constraint, OODS, Merkle, FRIA proximity test method that is used to determine whether a set of points is mostly on a polynomial with a degree less than a specified value. It resembles the FFT but the arithmetic complexity of its prover is strictly linear and that of the verifier is strictly logarithmic., and periodic-column helper contracts. The SHARP verifier can select any configured layout by cairoVerifierId.
Immutable Solidity verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for one Cairo CPU layout. It checks the STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof using layout-specific constraint, OODS, Merkle, FRIA proximity test method that is used to determine whether a set of points is mostly on a polynomial with a degree less than a specified value. It resembles the FFT but the arithmetic complexity of its prover is strictly linear and that of the verifier is strictly logarithmic., and periodic-column helper contracts. The SHARP verifier can select any configured layout by cairoVerifierId.
Stores the complete compiled Cairo outer bootloader used as the top-level program of a SHARP proof. The SHARP verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. copies these words into public memory, pinning this exact executable onchain independently of the separately committed simple, applicative, and recursive-verifier programs.
Immutable Solidity verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for one Cairo CPU layout. It checks the STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof using layout-specific constraint, OODS, Merkle, FRIA proximity test method that is used to determine whether a set of points is mostly on a polynomial with a degree less than a specified value. It resembles the FFT but the arithmetic complexity of its prover is strictly linear and that of the verifier is strictly logarithmic., and periodic-column helper contracts. The SHARP verifier can select any configured layout by cairoVerifierId.
Immutable Solidity verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for one Cairo CPU layout. It checks the STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof using layout-specific constraint, OODS, Merkle, FRIA proximity test method that is used to determine whether a set of points is mostly on a polynomial with a degree less than a specified value. It resembles the FFT but the arithmetic complexity of its prover is strictly linear and that of the verifier is strictly logarithmic., and periodic-column helper contracts. The SHARP verifier can select any configured layout by cairoVerifierId.
PermissionlessAnyone willing should be able to join and leave the network at any time, without causing significant disturbance to the network or being detrimental to the party in question. No single entity should have the power to allowlist or blocklist participants. commitment calculator and registry used by the Solidity STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. verifiers. Anyone may submit a public-memory page and interaction elements; the contract computes its hashA fixed-length fingerprint of variable-size input, produced by a hash function. and cumulative product and registers the fact key committing to them, which the CPU verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. must bind to the proof. It is part of the proof verifier, not an application-level program registry. A malicious or nonconforming implementation can break public-memory soundness; binding to a different honest registry generally causes a livenessLiveness refers to the ability of a system to respond to requests and to process them in a timely manner. In the context of L2s, it refers to the ability of settling transactions, proofs and state roots to the base layer. failure instead.
Upgradeable call router through which Starknet and other applications access SHARP fact registries. It uses call, not delegatecall, so facts and immutable verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. configuration remain at each target registry. The explicit isValid entry point always queries the default target. Other calls handled by the fallback, principally proof submissions, can be routed per caller to a still-active registry in the default target’s reference chain. The default target can be replaced by SHARP Multisig after 8d.
- Roles:
- admin: SHARP Multisig
- appGovernor: SHARP Multisig
- appRoleAdmin: SHARP Multisig
- governanceAdmin: SHARP Multisig
Immutable GPS statement verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. shared by Starknet and other StarkWare systems. It verifies a STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof of the exact Cairo bootloader stored onchain, forces the bootloader configuration into public memory, and registers a fact for every bootloader task. A fact is also considered valid when it exists in the time-limited reference fact registry.
Immutable GPS statement verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. shared by Starknet and other StarkWare systems. It verifies a STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof of the exact Cairo bootloader stored onchain, forces the bootloader configuration into public memory, and registers a fact for every bootloader task. A fact is also considered valid when it exists in the time-limited reference fact registry.
Immutable Solidity verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for one Cairo CPU layout. It checks the STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof using layout-specific constraint, OODS, Merkle, FRIA proximity test method that is used to determine whether a set of points is mostly on a polynomial with a degree less than a specified value. It resembles the FFT but the arithmetic complexity of its prover is strictly linear and that of the verifier is strictly logarithmic., and periodic-column helper contracts. The SHARP verifier can select any configured layout by cairoVerifierId.
Immutable Solidity verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for one Cairo CPU layout. It checks the STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof using layout-specific constraint, OODS, Merkle, FRIA proximity test method that is used to determine whether a set of points is mostly on a polynomial with a degree less than a specified value. It resembles the FFT but the arithmetic complexity of its prover is strictly linear and that of the verifier is strictly logarithmic., and periodic-column helper contracts. The SHARP verifier can select any configured layout by cairoVerifierId.
Immutable GPS statement verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. shared by Starknet and other StarkWare systems. It verifies a STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof of the exact Cairo bootloader stored onchain, forces the bootloader configuration into public memory, and registers a fact for every bootloader task. A fact is also considered valid when it exists in the time-limited reference fact registry.
Immutable Solidity verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for one Cairo CPU layout. It checks the STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof using layout-specific constraint, OODS, Merkle, FRIA proximity test method that is used to determine whether a set of points is mostly on a polynomial with a degree less than a specified value. It resembles the FFT but the arithmetic complexity of its prover is strictly linear and that of the verifier is strictly logarithmic., and periodic-column helper contracts. The SHARP verifier can select any configured layout by cairoVerifierId.
PermissionlessAnyone willing should be able to join and leave the network at any time, without causing significant disturbance to the network or being detrimental to the party in question. No single entity should have the power to allowlist or blocklist participants. commitment calculator and registry used by the Solidity STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. verifiers. Anyone may submit a public-memory page and interaction elements; the contract computes its hashA fixed-length fingerprint of variable-size input, produced by a hash function. and cumulative product and registers the fact key committing to them, which the CPU verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. must bind to the proof. It is part of the proof verifier, not an application-level program registry. A malicious or nonconforming implementation can break public-memory soundness; binding to a different honest registry generally causes a livenessLiveness refers to the ability of a system to respond to requests and to process them in a timely manner. In the context of L2s, it refers to the ability of settling transactions, proofs and state roots to the base layer. failure instead.
Immutable GPS statement verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. shared by Starknet and other StarkWare systems. It verifies a STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof of the exact Cairo bootloader stored onchain, forces the bootloader configuration into public memory, and registers a fact for every bootloader task. A fact is also considered valid when it exists in the time-limited reference fact registry.
Immutable Solidity verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. for one Cairo CPU layout. It checks the STARKShort for "scalable transparent argument of knowledge", a STARK is a type of zero-knowledge proof that resolves one of the primary weaknesses of ZK-SNARKs, its reliance on a "trusted setup”. STARKs also come with much simpler cryptographic assumptions, avoiding the need for elliptic curves, pairings, and the knowledge-of-exponent assumption and instead relying purely on hashes and information theory. This means that they are secure even against attackers with quantum computers. proof using layout-specific constraint, OODS, Merkle, FRIA proximity test method that is used to determine whether a set of points is mostly on a polynomial with a degree less than a specified value. It resembles the FFT but the arithmetic complexity of its prover is strictly linear and that of the verifier is strictly logarithmic., and periodic-column helper contracts. The SHARP verifier can select any configured layout by cairoVerifierId.
Adapter between the core contract and the SHARPVerifierCallProxy. Stores the Cairo programHash (3174901404014912024702042974619036870715605532092680335571201877913899936957).
The current deployment carries some associated risks:
Funds can be stolen if a contract receives a malicious code upgrade. There is no delay on code upgrades (CRITICAL).
Program Hashes
Name | Hash | Repository | Verification | Used in | |||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
317490...6957 | Code unknown | None | | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
342795...2024 | Projects used inSearch for projects used in | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
344285...1079 | Projects used inSearch for projects used in | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
235884...3330 | Projects used inSearch for projects used in | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
254986...4351 | Projects used inSearch for projects used in | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||